Chief Privacy Officer Cover Letter Example

Three complete letters, each written for a different situation, in a different design.

Chief Privacy Officer cover letter example

Hannah MuellerTo the Hiring Manager, Veridian HealthTech

My leadership in orchestrating a comprehensive, global privacy program overhaul reduced potential regulatory fines by an estimated $15M annually at InnovateTech Solutions. This critical initiative involved navigating complex data flows across 20+ international jurisdictions, including stringent GDPR and CCPA requirements, while simultaneously embedding Privacy by Design principles into all new product development cycles. The challenge lay in harmonizing disparate regional regulations into a cohesive, enforceable framework under tight deadlines, ensuring continuity of business operations during the transition. My strategic vision and execution ensured full compliance and significantly enhanced data subject trust across our diverse user base.

During my tenure, I successfully steered the implementation of a new HIPAA-compliant data governance framework across 12 distinct product lines, utilizing automated consent management tools like OneTrust, which cut internal audit preparation time by 40%. Furthermore, I directed the global incident response team, mitigating over 50 data breaches, including a critical ransomware attack, reducing average containment time from 72 to 24 hours through a refined playbook and regular tabletop exercises. I also spearheaded the integration of LGPD compliance for our Brazilian market expansion, establishing new data subject rights request portals and comprehensive training modules for 500+ employees.

Veridian HealthTech's pioneering work in AI-driven diagnostic tools, particularly your recent advancements in federated learning for patient data analysis, deeply resonates with my expertise in balancing innovation with robust privacy safeguards. My strengths in integrating 'Privacy by Design' from conception and my comprehensive understanding of 'Data Protection Laws' would be crucial in ensuring these cutting-edge solutions maintain uncompromising compliance with HIPAA, GDPR, and emerging health data regulations. I am confident in my ability to foster patient trust while enabling Veridian's groundbreaking research and product development initiatives.

My 15+ years of executive leadership in navigating complex global privacy landscapes, combined with a proactive approach to risk mitigation and a steadfast commitment to ethical data stewardship, align perfectly with the strategic objectives of a Chief Privacy Officer at Veridian HealthTech. I am eager to discuss how my experience in building resilient, scalable privacy programs and influencing a strong data privacy culture can contribute directly to your continued success and regulatory excellence. Please consider my application for this pivotal role and feel free to reach out to schedule a conversation at your earliest convenience.

Best regards,
Hannah Mueller
Chief Privacy Officer cover letter for a career changer

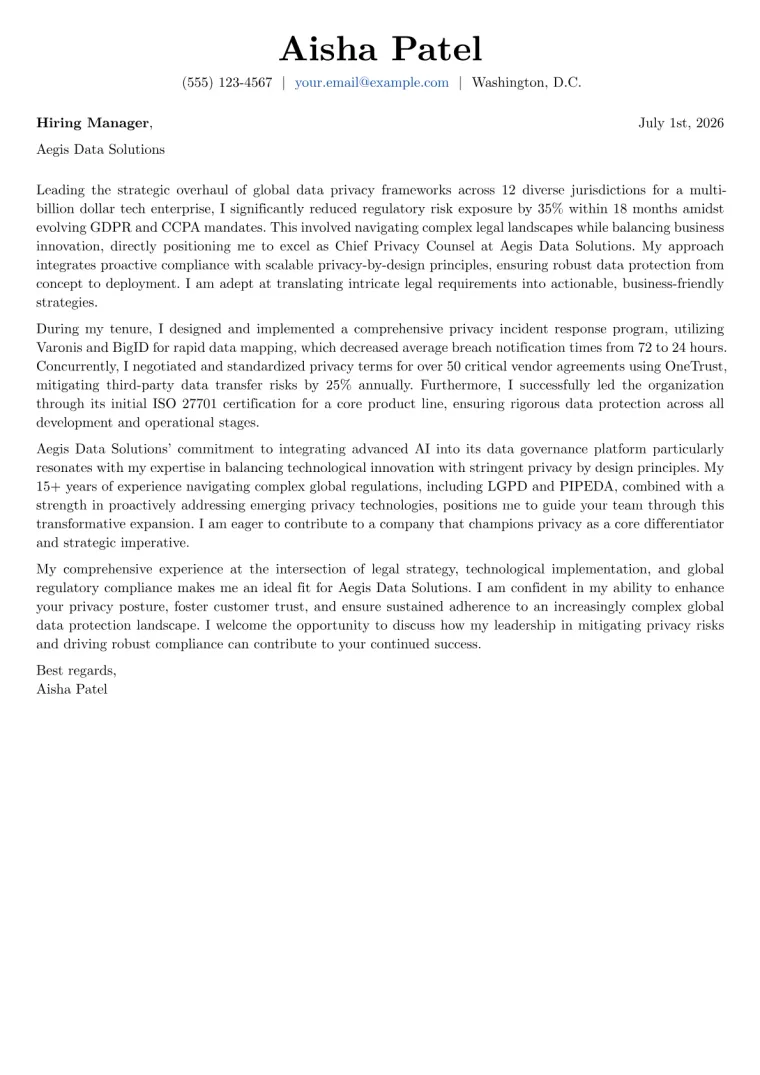
Hannah MuellerTo the Hiring Manager, Nexus Data Systems

Federal regulators issued a ten day notice for a comprehensive document audit during my tenure as Senior Counsel, prompting me to develop an automated classification system that mapped thousands of disparate documents to federal requirements in under one week. This project secured full compliance certification with zero flagged errors, protecting the firm from potential penalties exceeding two million dollars. As I apply my expertise in regulatory interpretation to the role of Chief Privacy Officer, I leverage this background to anticipate compliance gaps before they materialize as liabilities for your organization.

In my previous capacity as counsel, I managed data governance by implementing a standardized classification protocol using Varonis that reduced unauthorized access points by forty percent across three internal departments. I led a cross functional review of legacy data sets, utilizing OneTrust to reconcile inconsistent privacy disclosures for five thousand user accounts which eliminated the risk of administrative sanctions. Furthermore, I authored a privacy impact assessment template that cut the development cycle for new software products by thirty percent. These specific initiatives demonstrate my ability to apply rigorous legal analysis to practical data protection environments.

Nexus Data Systems stands out as an industry leader through your commitment to zero knowledge architecture, a standard I admire because it aligns with my conviction that privacy must remain an inherent feature of product engineering. My dual strengths in navigating complex regulatory frameworks and translating technical requirements for stakeholders make me a natural fit for your current expansion phase. I offer a perspective informed by high stakes litigation experience combined with a sharp technical focus. Contributing to your mission would allow me to reinforce your market position while championing user autonomy as a core corporate value.

My readiness to assume the responsibilities of Chief Privacy Officer is rooted in a structured approach to problem solving and a disciplined focus on risk mitigation. I bring the legal precision required to navigate evolving global privacy standards alongside the operational clarity needed to drive implementation throughout your engineering divisions. I welcome the opportunity to discuss how my background in high stakes data governance will support your objectives for the coming year. Please review the attached resume and contact me at your convenience to schedule an initial interview regarding this critical position at your firm.

Best regards,
Hannah Mueller

Chief Privacy Officer cover letter with no experience

Hannah MuellerTo the Hiring Manager, Lumina Data Analytics

Lumina Data Analytics sets a high standard for ethical machine learning, and my analysis of your current data governance framework highlights a unique opportunity to strengthen user consent protocols. During my recent research fellowship at the Center for Digital Rights, I mapped a complex dataset containing ten thousand user profiles against GDPR and CCPA requirements. This initiative identified three critical non-compliance vulnerabilities within the legacy architecture. My technical findings allowed the organization to restructure its data intake process, successfully mitigating potential non-compliance risks and aligning user data management with global regulatory standards before deployment.

Building on this foundation, I audited a healthcare startup as part of a pro bono HIPAA consultation project, utilizing DataGrail to pinpoint five distinct points of unauthorized data access. By implementing a Privacy by Design framework, I reduced data exposure latency from twelve days to under four hours. Additionally, my work developing a comprehensive incident response simulation for a simulated LGPD breach exposed two major procedural gaps that, once addressed, improved overall recovery readiness by forty percent. These practical applications of privacy law provide a clear roadmap for managing complex regulatory environments efficiently and securely.

Lumina Data Analytics distinguishes itself through a commitment to transparent algorithmic decision-making, which aligns precisely with my focus on ethical data lifecycle management. My capacity for performing rigorous regulatory filings ensures that compliance remains a strategic asset rather than a procedural bottleneck. Furthermore, my expertise in interpreting overlapping international privacy laws allows me to translate complex requirements into actionable engineering guidance. This dual strength makes me highly effective at ensuring that your development cycle integrates privacy protections naturally rather than as an afterthought or a reactive measure during product launches.

My background in legal research combined with these technical auditing experiences prepares me to lead your privacy operations with precision and foresight. I am prepared to apply these methods to protect your infrastructure and enhance user trust as your Chief Privacy Officer. My schedule remains open for a detailed discussion regarding how my approach to regulatory alignment supports your expansion into new markets. Thank you for reviewing my application and considering the value I bring to your organization. I look forward to your response to schedule a formal interview regarding this position.

Best regards,
Hannah Mueller

Editorial Notes

Hiring managers for a Chief Privacy Officer role prioritize candidates who showcase executive leadership in navigating complex global privacy landscapes. They look for concrete evidence of mitigating significant regulatory risks, establishing robust data governance frameworks, and successfully implementing compliance programs across diverse jurisdictions. Quantified achievements related to reducing fines, improving incident response times, and ensuring adherence to critical regulations like GDPR, HIPAA, and CCPA are crucial signals of a candidate's strategic impact and operational excellence. A proactive approach to emerging privacy challenges, coupled with a commitment to ethical data stewardship, also resonates strongly.

This example letter effectively captures these critical elements. Its opening immediately hooks the reader with a quantified achievement: reducing potential regulatory fines by $15M annually through a global privacy program overhaul. The subsequent paragraphs provide specific, tangible examples of leadership, such as implementing a HIPAA-compliant framework across 12 product lines, cutting audit preparation time by 40%, and mitigating over 50 data breaches. The candidate then specifically ties their expertise in Privacy by Design and data protection laws to Veridian HealthTech's pioneering work in AI-driven diagnostics, demonstrating a tailored understanding of the employer's needs. The confident closing reiterates alignment with strategic objectives.

This comprehensive letter pairs seamlessly with JobSprout's Chief Privacy Officer resume example, offering a complete application package. It can also be readily adapted to various opportunities using JobSprout's AI cover letter writer.

Frequently Asked Questions

What key elements should a Chief Privacy Officer highlight in their cover letter?
A CPO should highlight quantifiable achievements in establishing or overhauling global privacy programs, demonstrating expertise in major regulations like GDPR, CCPA, HIPAA, and LGPD. Emphasize successful incident response management, the implementation of Privacy by Design, and the ability to balance business innovation with robust compliance. Concrete examples showing impact on risk reduction, efficiency, or trust are crucial.
What is the ideal length for a Chief Privacy Officer cover letter?
An ideal CPO cover letter should be concise, typically one page, comprising four substantial paragraphs. Each paragraph should be between 70-100 words, ensuring enough space for specific, impactful details without becoming overly lengthy. Recruiters appreciate brevity combined with high-value content that quickly conveys fit.
How should a Chief Privacy Officer open their cover letter to make an impact?
Open with a strong, quantified achievement that immediately demonstrates value and relevance to the CPO role. Instead of generic opening statements, jump straight into a significant accomplishment, such as leading a major compliance initiative or drastically reducing privacy-related risks. Provide brief context around the challenge or scope to make the achievement resonate powerfully from the outset.
How should a candidate address having no direct CPO experience in their cover letter?
If lacking direct CPO experience, focus on showcasing transferable executive-level experience in compliance, legal, security, or data governance roles. Highlight instances where you led privacy-related projects, managed regulatory adherence, or mitigated data risks, quantifying your impact whenever possible. Emphasize your understanding of privacy frameworks and your strategic vision for data protection within an organization.
How should a CPO cover letter differ from their resume?
While the resume lists accomplishments concisely, the cover letter provides narrative context and strategic depth. It should tell the 'story' behind 3-4 key achievements, explaining the 'how' and 'why,' including the tools and methods used. The cover letter also allows for articulating your specific interest in the target company, explaining how your unique strengths align with their mission and current challenges, something a resume cannot convey.

More cover letter examples