Your Axon resume, matched to the job ad
Drop in your resume and it opens next to this job, ready to tailor in one click.
4.8 from 167 in-app reviews
Security Operations Engineer II
Axon · Scottsdale, Arizona, United States; Washington, United States
Tailor your resume to this job
No account needed to start.
What Axon asks for
From Axon's Security Operations Engineer II ad, checked 4 Nov 2026.
Incident response and alert triage
Hands-on experience investigating security alerts and triaging incidents. This includes participating in an on-call rotation to contain events like compromised accounts or exposed credentials.
Security automation and scripting
Using Python, shell scripting, and APIs to replace manual tasks with automation. This involves building playbooks and integrations that handle repetitive work like phishing triage or ticket management.
Detection engineering and SIEM
Writing and tuning detections within a SIEM or log analytics platform. You should have experience onboarding log sources and managing detections as code to find coverage gaps.
Cloud and infrastructure-as-code
Working knowledge of cloud platforms and experience using infrastructure-as-code tools to deploy security tooling with a focus on least-privilege design.
The ad asks for 2 or more years of experience in security engineering, SOC, or related software roles. Candidates must be able to pass an FBI background check and work onsite in Scottsdale, AZ or Seattle, WA.
How the example answers the ad
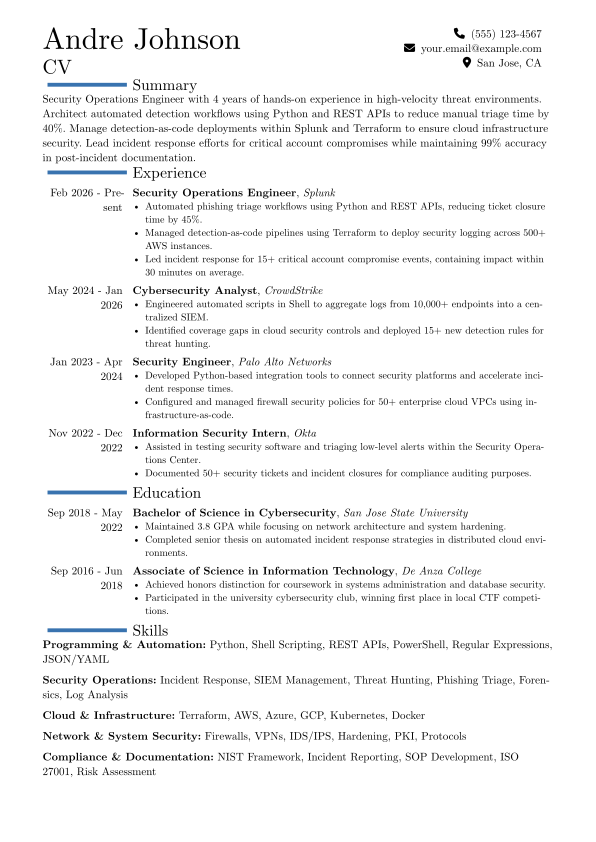
Three of the four requirements above, each matched to a line in the example.
Incident response and alert triage
“Led incident response for 15+ critical account compromise events, containing impact within 30 minutes on average.”
Handling 15 critical compromise events within 30 minutes shows the incident response and triage experience described in the requirement.
Security automation and scripting
“Automated phishing triage workflows using Python and REST APIs, reducing ticket closure time by 45%.”
Using Python and APIs to automate triage for phishing tickets is the specific type of automation and scripting the requirement seeks.
Detection engineering and SIEM
“Identified coverage gaps in cloud security controls and deployed 15+ new detection rules for threat hunting.”
Finding coverage gaps and deploying 15 rules shows the tuning and management aspects of detection engineering.
The whole example as text
Andre Johnson · Security Operations Engineer
Summary
Security Operations Engineer with 4 years of hands-on experience in high-velocity threat environments. Architect automated detection workflows using Python and REST APIs to reduce manual triage time by 40%. Manage detection-as-code deployments within Splunk and Terraform to ensure cloud infrastructure security. Lead incident response efforts for critical account compromises while maintaining 99% accuracy in post-incident documentation.
Experience
Security Operations Engineer · Splunk
San Jose, CA · 2026 - Present
- Automated phishing triage workflows using Python and REST APIs, reducing ticket closure time by 45%.
- Managed detection-as-code pipelines using Terraform to deploy security logging across 500+ AWS instances.
- Led incident response for 15+ critical account compromise events, containing impact within 30 minutes on average.
Cybersecurity Analyst · CrowdStrike
Irvine, CA · 2024 - 2026
- Engineered automated scripts in Shell to aggregate logs from 10,000+ endpoints into a centralized SIEM.
- Identified coverage gaps in cloud security controls and deployed 15+ new detection rules for threat hunting.
Security Engineer · Palo Alto Networks
Santa Clara, CA · 2023 - 2024
- Developed Python-based integration tools to connect security platforms and accelerate incident response times.
- Configured and managed firewall security policies for 50+ enterprise cloud VPCs using infrastructure-as-code.
Information Security Intern · Okta
San Francisco, CA · 2022 - 2022
- Assisted in testing security software and triaging low-level alerts within the Security Operations Center.
- Documented 50+ security tickets and incident closures for compliance auditing purposes.
Education
Bachelor of Science in Cybersecurity · San Jose State University
San Jose, CA · 2018 - 2022
- Maintained 3.8 GPA while focusing on network architecture and system hardening.
- Completed senior thesis on automated incident response strategies in distributed cloud environments.
Associate of Science in Information Technology · De Anza College
Cupertino, CA · 2016 - 2018
- Achieved honors distinction for coursework in systems administration and database security.
- Participated in the university cybersecurity club, winning first place in local CTF competitions.
Skills
Frequently asked questions
Is the example from an employee?
No. It is an AI-written example for this ad, made to show how a resume can answer it.
Do I need to meet every qualification to apply?
No. Axon encourages applicants to apply even if their experience does not perfectly align with every qualification listed.
Is this role remote?
No. The position is based onsite at Axon's Scottsdale, AZ or Seattle, WA offices.
Where do I apply?
On the official Axon posting, through the job link on this page.
What happens when I tailor my resume here?
Your resume opens in the editor next to this job. Tailor it in one click, then keep or discard the edits. You only need an account to download.