Cyber Threat Hunter Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
Cyber Threat Hunter
Salary Range
Salary Trend
12-Month Trend
Based on advertised Human Resources roles.
US market data · Source: Adzuna · Updated Mar 2026
How useful was this template?
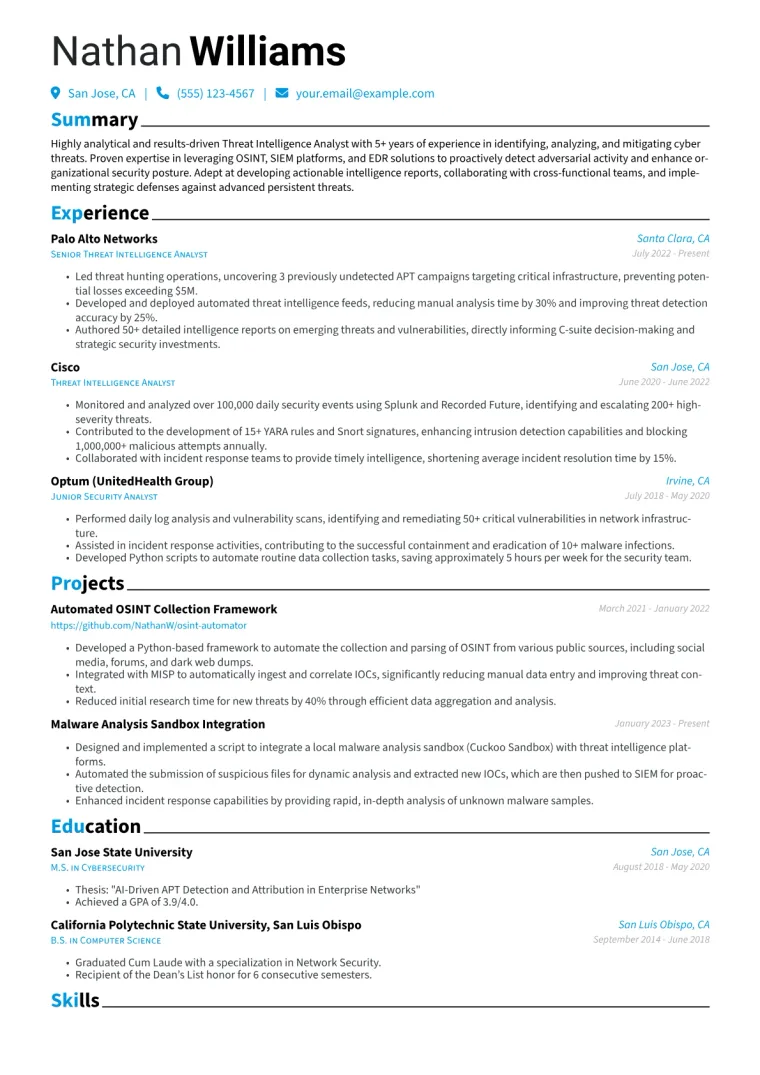
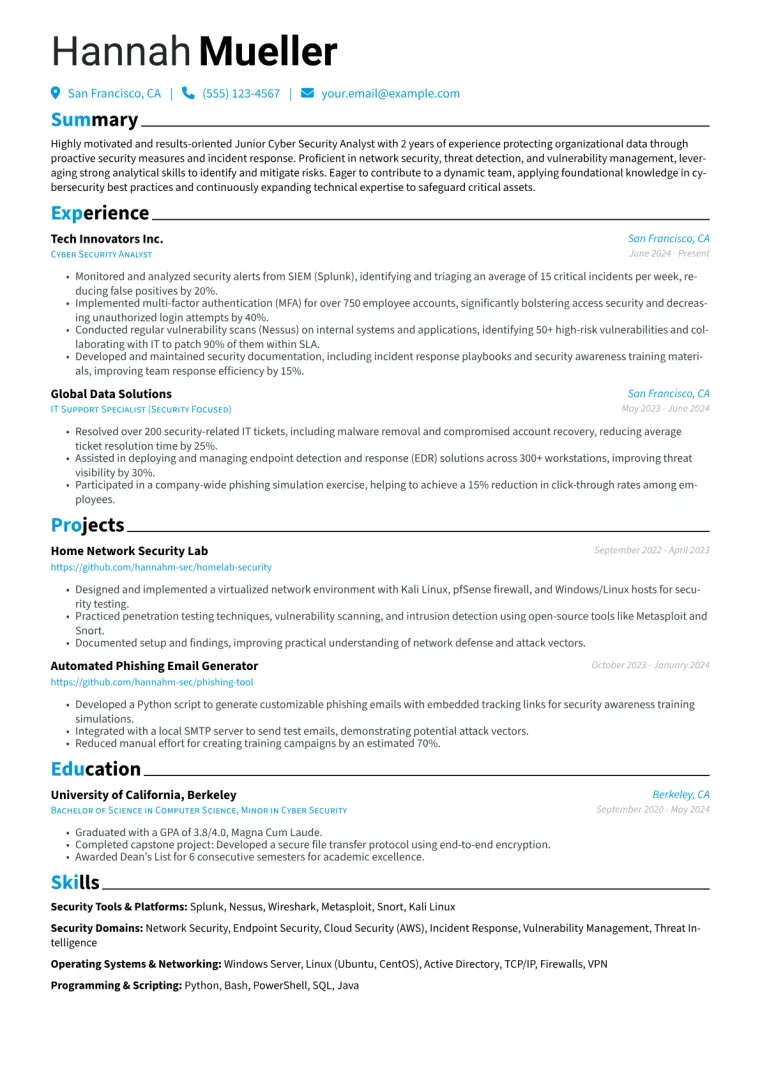
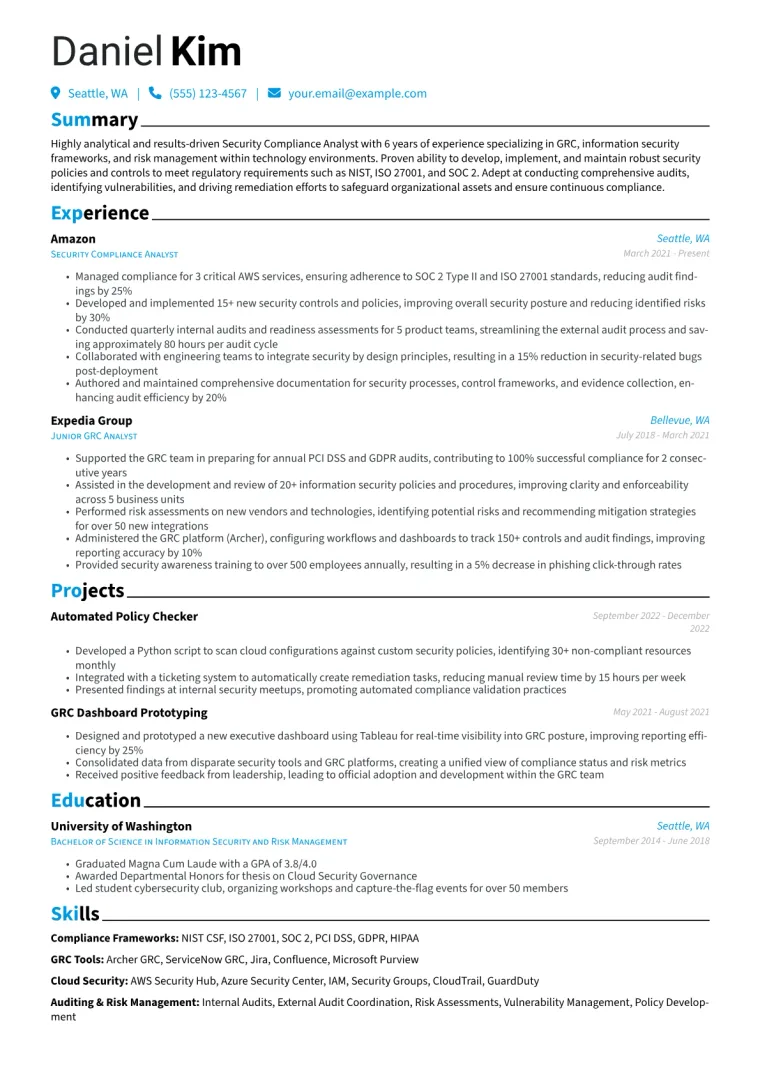
Cyber Threat Hunter resume samples
Three complete resumes, each in a different design.
Free to use. No download fee.
What makes a strong Cyber Threat Hunter resume?
US median salary $149,396 ·
Cyber Threat Hunters require resumes that clearly articulate their ability to proactively identify and neutralize advanced threats, rather than merely responding to incidents. Hiring managers look for concrete achievements demonstrating success in reducing organizational risk, improving detection capabilities, and providing actionable intelligence. Key elements include experience with specific frameworks like MITRE ATT&CK, expertise in developing custom detection rules (e.g., YARA, Sigma), and quantifiable results from uncovering sophisticated campaigns. Certifications from organizations like GIAC and Offensive Security are highly valued, underscoring specialized technical proficiency crucial for this demanding role.
Why this example works
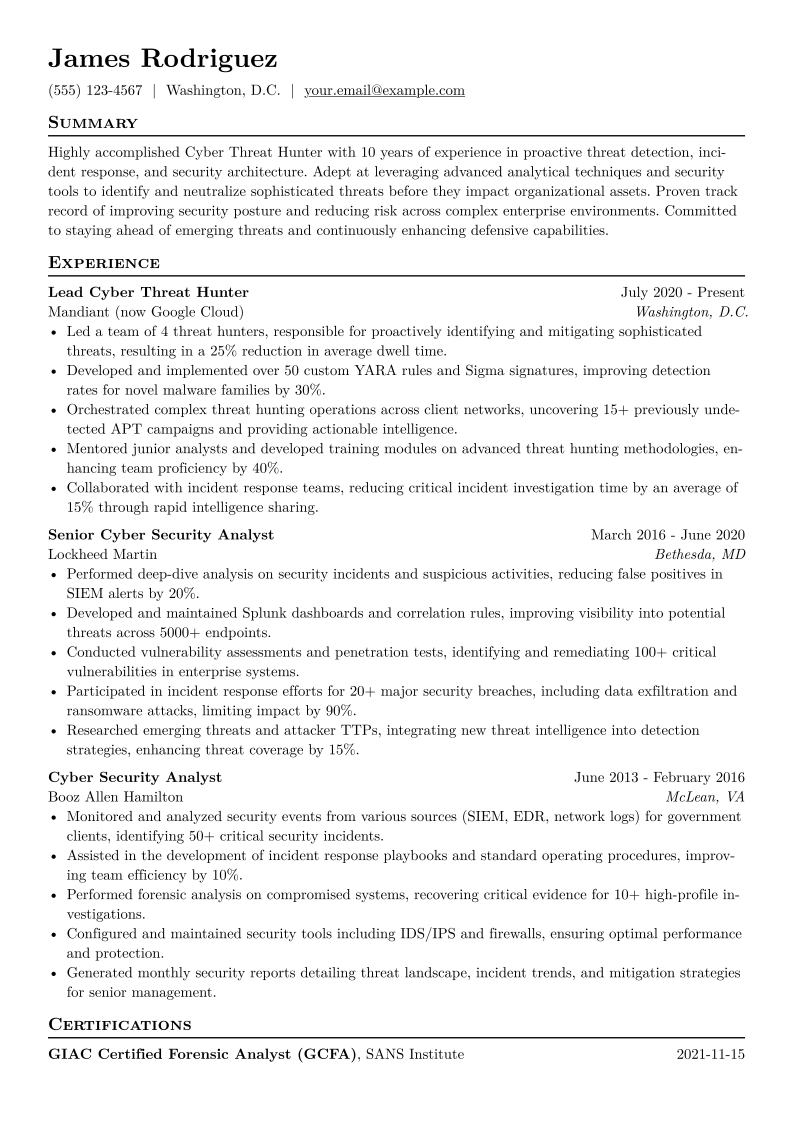
The James Rodriguez example resume on JobSprout effectively showcases these critical qualifications. It highlights quantifiable successes such as leading a team of 4 threat hunters, resulting in a 25% reduction in average dwell time, and improving detection rates for novel malware families by 30% through developing 50+ custom YARA rules and Sigma signatures. The experience section details uncovering 15+ previously undetected APT campaigns and collaborating with incident response teams to reduce critical incident investigation time by 15%. The inclusion of certifications like GIAC Certified Forensic Analyst (GCFA) and Offensive Security Certified Professional (OSCP), alongside detailed skill groups in Threat Hunting & Intelligence and SIEM & EDR Platforms, further substantiates the candidate's expertise.
Cyber Threat Hunter resume example (text version)
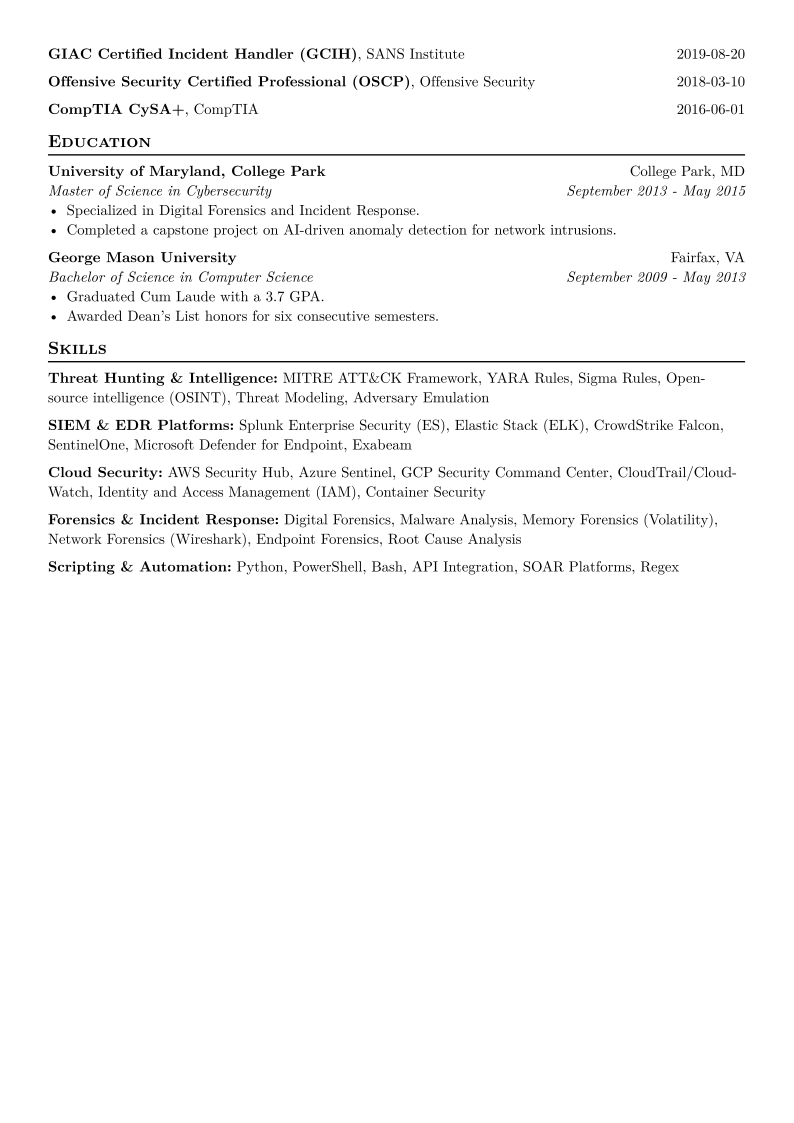
James Rodriguez · Cyber Threat Hunter
Summary
Highly accomplished Cyber Threat Hunter with 10 years of experience in proactive threat detection, incident response, and security architecture. Adept at leveraging advanced analytical techniques and security tools to identify and neutralize sophisticated threats before they impact organizational assets. Proven track record of improving security posture and reducing risk across complex enterprise environments. Committed to staying ahead of emerging threats and continuously enhancing defensive capabilities.
Experience
Lead Cyber Threat Hunter · Mandiant (now Google Cloud)
Washington, D.C. · 2020 - Present
- Led a team of 4 threat hunters, responsible for proactively identifying and mitigating sophisticated threats, resulting in a 25% reduction in average dwell time.
- Developed and implemented over 50 custom YARA rules and Sigma signatures, improving detection rates for novel malware families by 30%.
- Orchestrated complex threat hunting operations across client networks, uncovering 15+ previously undetected APT campaigns and providing actionable intelligence.
- Mentored junior analysts and developed training modules on advanced threat hunting methodologies, enhancing team proficiency by 40%.
- Collaborated with incident response teams, reducing critical incident investigation time by an average of 15% through rapid intelligence sharing.
Senior Cyber Security Analyst · Lockheed Martin
Bethesda, MD · 2016 - 2020
- Performed deep-dive analysis on security incidents and suspicious activities, reducing false positives in SIEM alerts by 20%.
- Developed and maintained Splunk dashboards and correlation rules, improving visibility into potential threats across 5000+ endpoints.
- Conducted vulnerability assessments and penetration tests, identifying and remediating 100+ critical vulnerabilities in enterprise systems.
- Participated in incident response efforts for 20+ major security breaches, including data exfiltration and ransomware attacks, limiting impact by 90%.
- Researched emerging threats and attacker TTPs, integrating new threat intelligence into detection strategies, enhancing threat coverage by 15%.
Cyber Security Analyst · Booz Allen Hamilton
McLean, VA · 2013 - 2016
- Monitored and analyzed security events from various sources (SIEM, EDR, network logs) for government clients, identifying 50+ critical security incidents.
- Assisted in the development of incident response playbooks and standard operating procedures, improving team efficiency by 10%.
- Performed forensic analysis on compromised systems, recovering critical evidence for 10+ high-profile investigations.
- Configured and maintained security tools including IDS/IPS and firewalls, ensuring optimal performance and protection.
- Generated monthly security reports detailing threat landscape, incident trends, and mitigation strategies for senior management.
Education
Master of Science in Cybersecurity · University of Maryland, College Park
College Park, MD · 2013 - 2015
- Specialized in Digital Forensics and Incident Response.
- Completed a capstone project on AI-driven anomaly detection for network intrusions.
Bachelor of Science in Computer Science · George Mason University
Fairfax, VA · 2009 - 2013
- Graduated Cum Laude with a 3.7 GPA.
- Awarded Dean's List honors for six consecutive semesters.
Skills
Cyber Threat Hunter resume example: Cloud & Enterprise
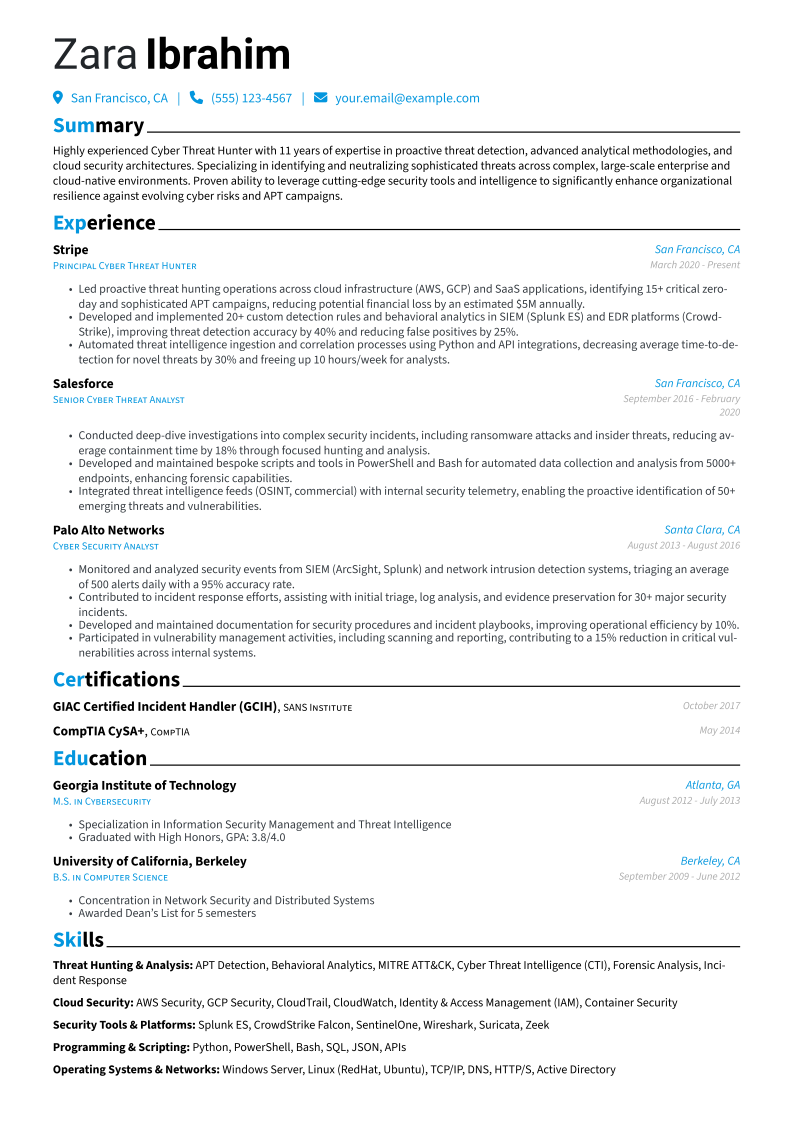
Zara Ibrahim · Cyber Threat Hunter
Summary
Highly experienced Cyber Threat Hunter with 11 years of expertise in proactive threat detection, advanced analytical methodologies, and cloud security architectures. Specializing in identifying and neutralizing sophisticated threats across complex, large-scale enterprise and cloud-native environments. Proven ability to leverage cutting-edge security tools and intelligence to significantly enhance organizational resilience against evolving cyber risks and APT campaigns.
Experience
Principal Cyber Threat Hunter · Stripe
San Francisco, CA · 2020 - Present
- Led proactive threat hunting operations across cloud infrastructure (AWS, GCP) and SaaS applications, identifying 15+ critical zero-day and sophisticated APT campaigns, reducing potential financial loss by an estimated $5M annually.
- Developed and implemented 20+ custom detection rules and behavioral analytics in SIEM (Splunk ES) and EDR platforms (CrowdStrike), improving threat detection accuracy by 40% and reducing false positives by 25%.
- Automated threat intelligence ingestion and correlation processes using Python and API integrations, decreasing average time-to-detection for novel threats by 30% and freeing up 10 hours/week for analysts.
- Mentored junior threat hunters and analysts, establishing best practices for cloud-native threat investigation and contributing to a 15% increase in team's investigative efficiency.
- Collaborated with security engineering to deploy enhanced visibility tools, resulting in a 20% improvement in coverage for critical cloud assets against advanced attacker techniques.
Senior Cyber Threat Analyst · Salesforce
San Francisco, CA · 2016 - 2020
- Conducted deep-dive investigations into complex security incidents, including ransomware attacks and insider threats, reducing average containment time by 18% through focused hunting and analysis.
- Developed and maintained bespoke scripts and tools in PowerShell and Bash for automated data collection and analysis from 5000+ endpoints, enhancing forensic capabilities.
- Integrated threat intelligence feeds (OSINT, commercial) with internal security telemetry, enabling the proactive identification of 50+ emerging threats and vulnerabilities.
- Presented findings and threat landscapes to executive leadership and technical teams, improving organizational understanding of risk and influencing security roadmap priorities.
- Performed regular purple team exercises to validate defensive capabilities, identifying 10+ gaps in detection and response that were subsequently remediated.
Cyber Security Analyst · Palo Alto Networks
Santa Clara, CA · 2013 - 2016
- Monitored and analyzed security events from SIEM (ArcSight, Splunk) and network intrusion detection systems, triaging an average of 500 alerts daily with a 95% accuracy rate.
- Contributed to incident response efforts, assisting with initial triage, log analysis, and evidence preservation for 30+ major security incidents.
- Developed and maintained documentation for security procedures and incident playbooks, improving operational efficiency by 10%.
- Participated in vulnerability management activities, including scanning and reporting, contributing to a 15% reduction in critical vulnerabilities across internal systems.
- Performed basic malware analysis and reverse engineering to understand threat behaviors and inform detection strategies.
Education
M.S. in Cybersecurity · Georgia Institute of Technology
Atlanta, GA · 2012 - 2013
- Specialization in Information Security Management and Threat Intelligence
- Graduated with High Honors, GPA: 3.8/4.0
B.S. in Computer Science · University of California, Berkeley
Berkeley, CA · 2009 - 2012
- Concentration in Network Security and Distributed Systems
- Awarded Dean's List for 5 semesters
Skills
Cyber Threat Hunter resume example: Career Changer
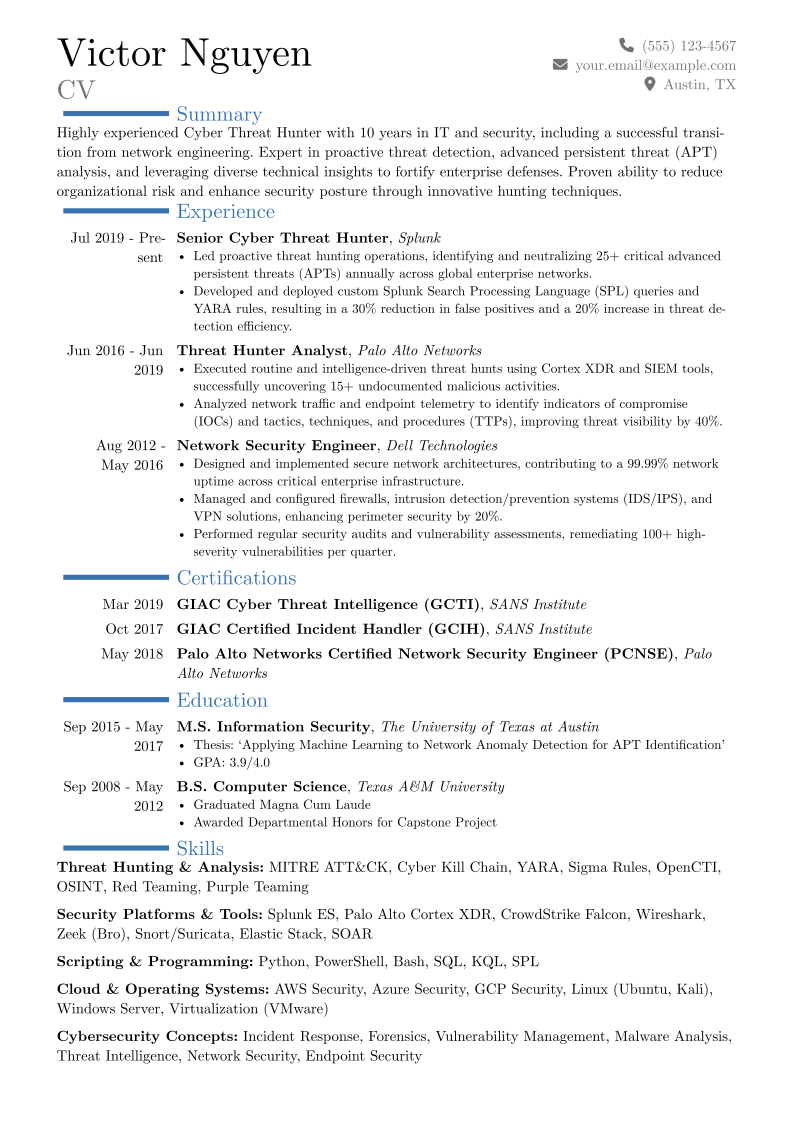
Victor Nguyen · Cyber Threat Hunter
Summary
Highly experienced Cyber Threat Hunter with 10 years in IT and security, including a successful transition from network engineering. Expert in proactive threat detection, advanced persistent threat (APT) analysis, and leveraging diverse technical insights to fortify enterprise defenses. Proven ability to reduce organizational risk and enhance security posture through innovative hunting techniques.
Experience
Senior Cyber Threat Hunter · Splunk
Austin, TX · 2019 - Present
- Led proactive threat hunting operations, identifying and neutralizing 25+ critical advanced persistent threats (APTs) annually across global enterprise networks.
- Developed and deployed custom Splunk Search Processing Language (SPL) queries and YARA rules, resulting in a 30% reduction in false positives and a 20% increase in threat detection efficiency.
- Collaborated with incident response teams, providing critical intelligence that reduced average incident resolution time by 15% for complex security breaches.
- Mentored junior analysts and contributed to the development of purple teaming exercises, enhancing defensive capabilities and security team readiness by 25%.
- Pioneered the integration of new threat intelligence feeds, expanding coverage and enabling detection of novel attack vectors prior to widespread impact.
Threat Hunter Analyst · Palo Alto Networks
Santa Clara, CA · 2016 - 2019
- Executed routine and intelligence-driven threat hunts using Cortex XDR and SIEM tools, successfully uncovering 15+ undocumented malicious activities.
- Analyzed network traffic and endpoint telemetry to identify indicators of compromise (IOCs) and tactics, techniques, and procedures (TTPs), improving threat visibility by 40%.
- Developed and refined security content (rules, dashboards, reports) for enterprise clients, leading to a 10% improvement in client security posture scores.
- Participated in incident response activities, assisting in forensic analysis and containment strategies for 50+ security incidents.
- Researched emerging threats and vulnerabilities, translating findings into actionable intelligence reports for internal and external stakeholders.
Network Security Engineer · Dell Technologies
Round Rock, TX · 2012 - 2016
- Designed and implemented secure network architectures, contributing to a 99.99% network uptime across critical enterprise infrastructure.
- Managed and configured firewalls, intrusion detection/prevention systems (IDS/IPS), and VPN solutions, enhancing perimeter security by 20%.
- Performed regular security audits and vulnerability assessments, remediating 100+ high-severity vulnerabilities per quarter.
- Developed Python scripts to automate network device configuration and log analysis, reducing manual effort by 25 hours per month.
- Responded to and resolved network security incidents, isolating affected systems and restoring services within defined SLAs.
Education
M.S. Information Security · The University of Texas at Austin
Austin, TX · 2015 - 2017
- Thesis: 'Applying Machine Learning to Network Anomaly Detection for APT Identification'
- GPA: 3.9/4.0
B.S. Computer Science · Texas A&M University
College Station, TX · 2008 - 2012
- Graduated Magna Cum Laude
- Awarded Departmental Honors for Capstone Project
Skills
How useful was this template?
Example by JobSprout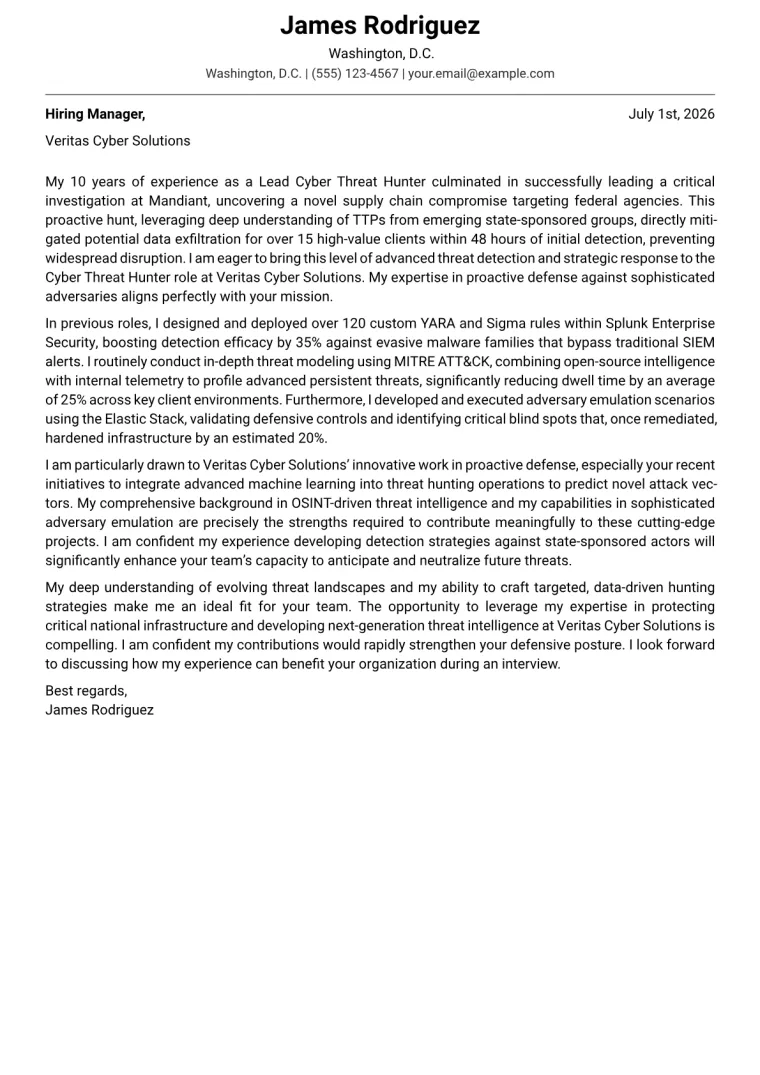
Cyber Threat Hunter Cover Letter Example
Written for the same person as this resume, ready to adapt.
Cyber Threat Hunter resume summary example
Highly accomplished Cyber Threat Hunter with 10 years of experience in proactive threat detection, incident response, and security architecture. Adept at leveraging advanced analytical techniques and security tools to identify and neutralize sophisticated threats before they impact organizational assets. Proven track record of improving security posture and reducing risk across complex enterprise environments. Committed to staying ahead of emerging threats and continuously enhancing defensive capabilities.
Cyber Threat Hunter salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $132,143 | $149,396 | $162,768 |
| UK | £46,059 | £60,012 | £72,658 |
| Canada | C$86,152 | C$113,871 | C$140,800 |
| Australia | A$101,935 | A$126,667 | A$147,857 |
| Germany | €59,500 | €70,570 | €77,887 |
| France | €37,875 | €44,167 | €49,750 |
| Netherlands | €55,000 | €66,667 | €74,250 |
| Italy | €25,000 | €31,250 | €38,750 |
| Austria | €46,250 | €58,750 | €67,500 |
| New Zealand | NZ$102,500 | NZ$120,000 | NZ$162,500 |
| India | ₹570,786 | ₹1,167,051 | ₹1,840,563 |
| Poland | zł186,440 | zł209,338 | zł232,236 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
Cyber Threat Hunter resume skills and keywords
Recruiters and applicant tracking systems scan Cyber Threat Hunter resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
Cyber Threat Hunter
Salary Range
Salary Trend
12-Month Trend
Based on advertised Human Resources roles.
US market data · Source: Adzuna · Updated Mar 2026
Frequently Asked Questions
What's the best resume structure for a senior Cyber Threat Hunter?
Which skills and qualifications should a Cyber Threat Hunter really emphasize?
How do I write strong achievement bullets or a professional summary as a Cyber Threat Hunter?
What optional sections are important for a senior Cyber Threat Hunter's resume?
How can I tailor my Cyber Threat Hunter resume for a specific job posting?
The blank page is the hard part. Skip it.
Free to use. No download fee.