Your Island resume, matched to the job ad
Drop in your resume and it opens next to this job, ready to tailor in one click.
4.8 from 167 in-app reviews
Security Operations Engineer
Island · Dallas
Tailor your resume to this job
No account needed to start.
What Island asks for
From Island's Security Operations Engineer ad, checked 4 Nov 2026.
Vulnerability scanning tools
Operating and maintaining tools for scanning web applications, network infrastructure, and container runtimes, including Burp Suite, Nessus, and Sysdig.
Triage and remediation tracking
Reviewing scan results to filter out false positives, ranking findings by their risk level, and tracking the fix through Jira tickets while working with engineering teams.
Compliance and FedRAMP monitoring
Supporting continuous monitoring for FedRAMP, collecting evidence, and working with frameworks like NIST 800-53 and tools such as eMASS.
AWS and container security
Hands-on understanding of AWS infrastructure and container technologies like Kubernetes and Docker.
Scripting and automation
Using Python or Bash to automate scanning workflows, scheduling, and alerting to improve security operations.
The ad asks for 1 to 3 years of experience in security operations or a related field. You must be a US citizen capable of working in FedRAMP environments. The role is hybrid, four days per week in Coppell, TX.
How the example answers the ad
Four of the five requirements above, each matched to a line in the example.
Vulnerability scanning tools
“Managed vulnerability scanning operations across 500+ AWS accounts using Nessus and Sysdig, reducing mean-time-to-remediate by 40%.”
Operating Nessus and Sysdig for scanning across 500+ AWS accounts shows the vulnerability scanning tools requirement.
Triage and remediation tracking
“Orchestrated remediation workflows in Jira for 200+ container security findings, maintaining 99% compliance with internal SLAs.”
Using Jira to manage remediation workflows for over 200 findings shows the triage and remediation tracking requirement.
Scripting and automation
“Automated report generation for NIST 800-53 audits using Python, saving 15 hours of manual effort per audit cycle.”
Using Python to automate report generation for audit cycles shows the scripting and automation requirement.
Compliance and FedRAMP monitoring
“Supported FedRAMP continuous monitoring efforts by gathering 50+ evidence artifacts within eMASS for annual assessment.”
Gathering over 50 artifacts in eMASS for FedRAMP monitoring shows the compliance and FedRAMP monitoring requirement.
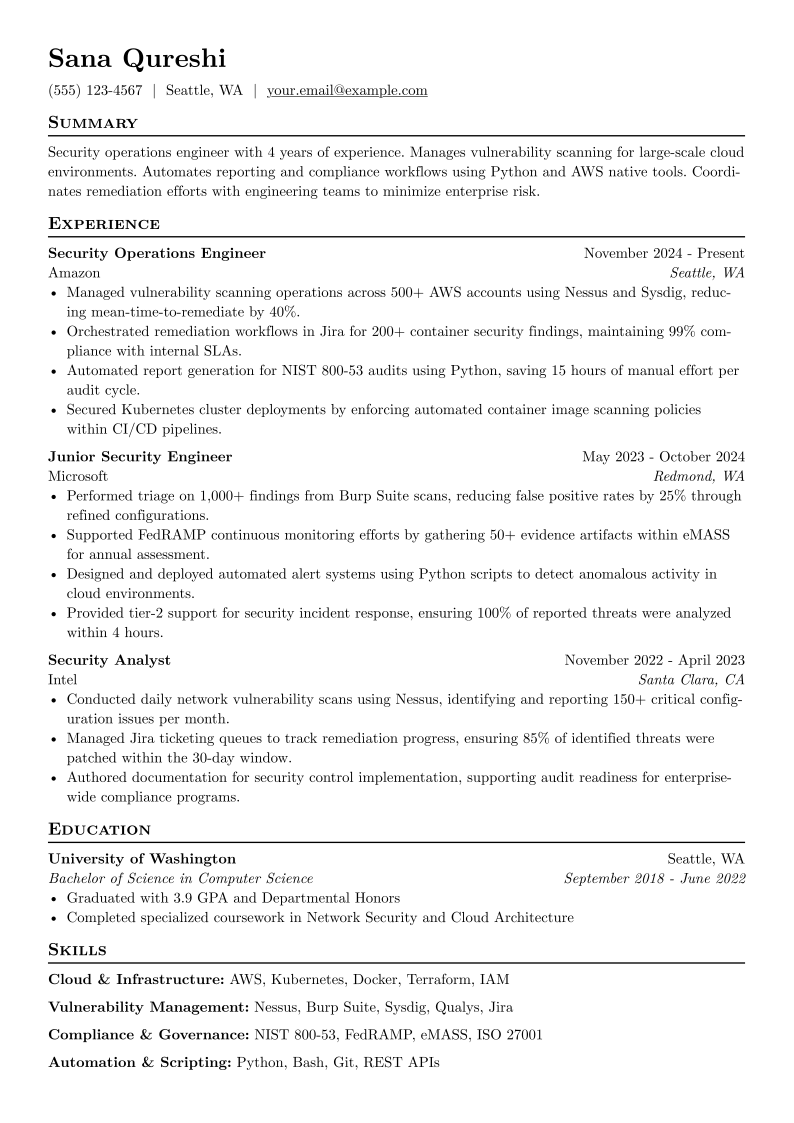
The whole example as text
Sana Qureshi · Security Operations Engineer
Summary
Security operations engineer with 4 years of experience. Manages vulnerability scanning for large-scale cloud environments. Automates reporting and compliance workflows using Python and AWS native tools. Coordinates remediation efforts with engineering teams to minimize enterprise risk.
Experience
Security Operations Engineer · Amazon
Seattle, WA · 2024 - Present
- Managed vulnerability scanning operations across 500+ AWS accounts using Nessus and Sysdig, reducing mean-time-to-remediate by 40%.
- Orchestrated remediation workflows in Jira for 200+ container security findings, maintaining 99% compliance with internal SLAs.
- Automated report generation for NIST 800-53 audits using Python, saving 15 hours of manual effort per audit cycle.
- Secured Kubernetes cluster deployments by enforcing automated container image scanning policies within CI/CD pipelines.
Junior Security Engineer · Microsoft
Redmond, WA · 2023 - 2024
- Performed triage on 1,000+ findings from Burp Suite scans, reducing false positive rates by 25% through refined configurations.
- Supported FedRAMP continuous monitoring efforts by gathering 50+ evidence artifacts within eMASS for annual assessment.
- Designed and deployed automated alert systems using Python scripts to detect anomalous activity in cloud environments.
- Provided tier-2 support for security incident response, ensuring 100% of reported threats were analyzed within 4 hours.
Security Analyst · Intel
Santa Clara, CA · 2022 - 2023
- Conducted daily network vulnerability scans using Nessus, identifying and reporting 150+ critical configuration issues per month.
- Managed Jira ticketing queues to track remediation progress, ensuring 85% of identified threats were patched within the 30-day window.
- Authored documentation for security control implementation, supporting audit readiness for enterprise-wide compliance programs.
Education
Bachelor of Science in Computer Science · University of Washington
Seattle, WA · 2018 - 2022
- Graduated with 3.9 GPA and Departmental Honors
- Completed specialized coursework in Network Security and Cloud Architecture
Skills
Frequently asked questions
Is the example from an employee?
No. It is an AI-written example for this ad, made to show how a resume can answer it.
What is the specific in-office requirement?
The role is based in Coppell, TX, and requires you to be in the office four days every week.
Do I need to be a US citizen?
Yes. The role involves working in FedRAMP-regulated environments which requires US citizenship.
Where do I apply?
On the official Island posting, through the job link on this page.
What happens when I tailor my resume here?
Your resume opens in the editor next to this job. Tailor it in one click, then keep or discard the edits. You only need an account to download.