Your Tanium resume, matched to the job ad
Drop in your resume and it opens next to this job, ready to tailor in one click.
4.8 from 167 in-app reviews
Senior Security Engineer - Vulnerability Research
Tanium · Remote, US
Tailor your resume to this job
No account needed to start.
What Tanium asks for
From Tanium's Senior Security Engineer - Vulnerability Research ad, checked 4 Nov 2026.
Vulnerability research methods
Practical experience in finding vulnerabilities through source code review, manual penetration testing of applications, or fuzzing.
Severity and impact analysis
Determining how exploitable a vulnerability is and calculating its potential impact on the business to prioritize triage.
Remediation and patching
Assisting engineering teams by providing specific patch guidance and pull requests to ensure vulnerabilities are fixed efficiently.
Security tooling and AI workflows
Building tools to support research, such as fuzzing harnesses or static analyzers, and using AI models to build agentic security workflows.
Go, C++, JavaScript or Python
Ability to read and write code in at least one major language, including Go, C++, TypeScript, JavaScript, or Python.
The ad asks for at least 5 years of industry experience and a bachelor's degree in computer science or a related field. The role is remote in the United States.
How the example answers the ad
Four of the five requirements above, each matched to a line in the example.
Vulnerability research methods
“Developed custom Go-based fuzzing harnesses that identified 12 critical memory safety issues in core payment processing services.”
Creating fuzzing harnesses in Go to find 12 memory safety issues shows practical experience in vulnerability research methods.
Severity and impact analysis
“Implemented rigorous severity and impact analysis metrics to prioritize patching for exposed API endpoints.”
Implementing metrics to prioritize patching for API endpoints shows the use of severity and impact analysis for triage.
Remediation and patching
“Provided remediation guidance and verified pull requests that resolved 150+ high-severity findings in under 48 hours.”
Verifying pull requests and providing guidance to resolve 150 findings shows remediation and patching skills.
Security tooling and AI workflows
“Architected an AI-driven triaging pipeline that reduced vulnerability false positives by 60 percent across all engineering teams.”
Architecting an AI triaging pipeline that reduced false positives by 60 percent shows the use of AI models in security workflows.
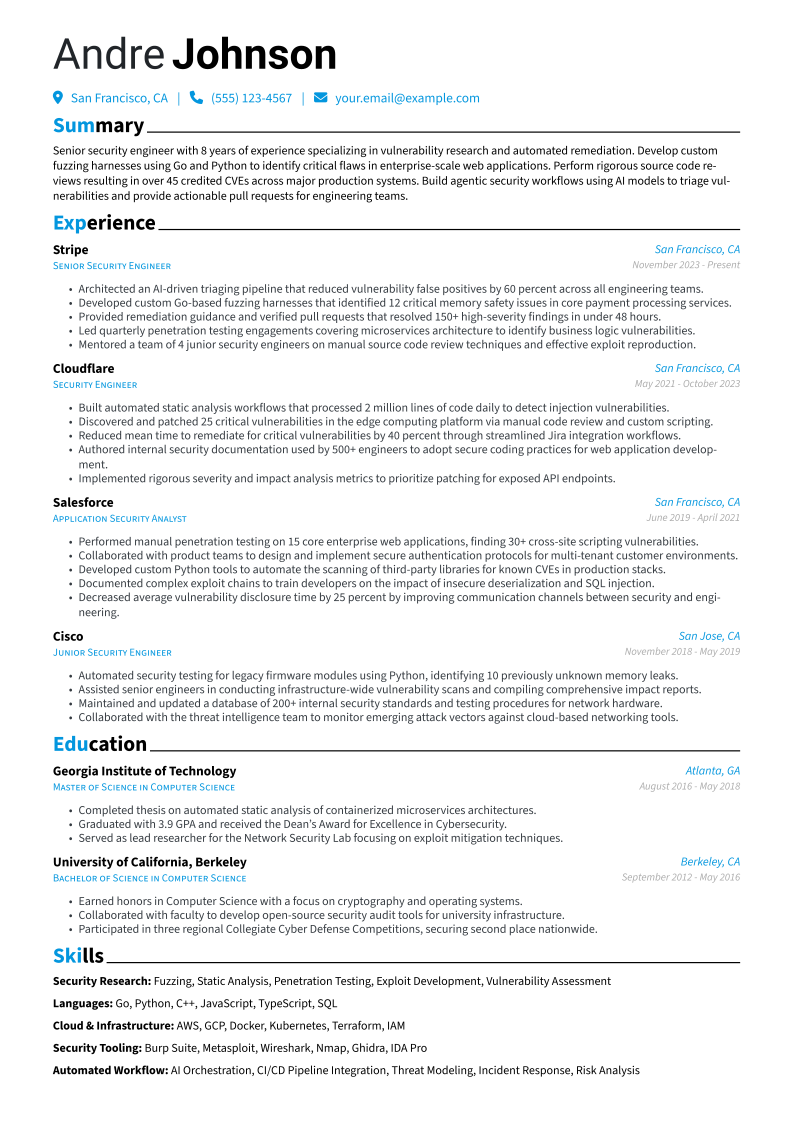
The whole example as text
Andre Johnson · Senior Security Engineer
Summary
Senior security engineer with 8 years of experience specializing in vulnerability research and automated remediation. Develop custom fuzzing harnesses using Go and Python to identify critical flaws in enterprise-scale web applications. Perform rigorous source code reviews resulting in over 45 credited CVEs across major production systems. Build agentic security workflows using AI models to triage vulnerabilities and provide actionable pull requests for engineering teams.
Experience
Senior Security Engineer · Stripe
San Francisco, CA · 2023 - Present
- Architected an AI-driven triaging pipeline that reduced vulnerability false positives by 60 percent across all engineering teams.
- Developed custom Go-based fuzzing harnesses that identified 12 critical memory safety issues in core payment processing services.
- Provided remediation guidance and verified pull requests that resolved 150+ high-severity findings in under 48 hours.
- Led quarterly penetration testing engagements covering microservices architecture to identify business logic vulnerabilities.
- Mentored a team of 4 junior security engineers on manual source code review techniques and effective exploit reproduction.
Security Engineer · Cloudflare
San Francisco, CA · 2021 - 2023
- Built automated static analysis workflows that processed 2 million lines of code daily to detect injection vulnerabilities.
- Discovered and patched 25 critical vulnerabilities in the edge computing platform via manual code review and custom scripting.
- Reduced mean time to remediate for critical vulnerabilities by 40 percent through streamlined Jira integration workflows.
- Authored internal security documentation used by 500+ engineers to adopt secure coding practices for web application development.
- Implemented rigorous severity and impact analysis metrics to prioritize patching for exposed API endpoints.
Application Security Analyst · Salesforce
San Francisco, CA · 2019 - 2021
- Performed manual penetration testing on 15 core enterprise web applications, finding 30+ cross-site scripting vulnerabilities.
- Collaborated with product teams to design and implement secure authentication protocols for multi-tenant customer environments.
- Developed custom Python tools to automate the scanning of third-party libraries for known CVEs in production stacks.
- Documented complex exploit chains to train developers on the impact of insecure deserialization and SQL injection.
- Decreased average vulnerability disclosure time by 25 percent by improving communication channels between security and engineering.
Junior Security Engineer · Cisco
San Jose, CA · 2018 - 2019
- Automated security testing for legacy firmware modules using Python, identifying 10 previously unknown memory leaks.
- Assisted senior engineers in conducting infrastructure-wide vulnerability scans and compiling comprehensive impact reports.
- Maintained and updated a database of 200+ internal security standards and testing procedures for network hardware.
- Collaborated with the threat intelligence team to monitor emerging attack vectors against cloud-based networking tools.
Education
Master of Science in Computer Science · Georgia Institute of Technology
Atlanta, GA · 2016 - 2018
- Completed thesis on automated static analysis of containerized microservices architectures.
- Graduated with 3.9 GPA and received the Dean's Award for Excellence in Cybersecurity.
- Served as lead researcher for the Network Security Lab focusing on exploit mitigation techniques.
Bachelor of Science in Computer Science · University of California, Berkeley
Berkeley, CA · 2012 - 2016
- Earned honors in Computer Science with a focus on cryptography and operating systems.
- Collaborated with faculty to develop open-source security audit tools for university infrastructure.
- Participated in three regional Collegiate Cyber Defense Competitions, securing second place nationwide.
Skills
More Tanium roles like this one
Frequently asked questions
Is the example from an employee?
No. It is an AI-written example for this ad, made to show how a resume can answer it.
Is this role remote?
Yes. The ad lists the position as remote in the United States.
Where do I apply?
On the official Tanium posting, through the job link on this page.
What happens when I tailor my resume here?
Your resume opens in the editor next to this job. Tailor it in one click, then keep or discard the edits. You only need an account to download.