Cover Letter Examples

Cloud Security Engineer Cover Letter Example

Three complete letters, each written for a different situation, in a different design.

Cloud Security Engineer cover letter example

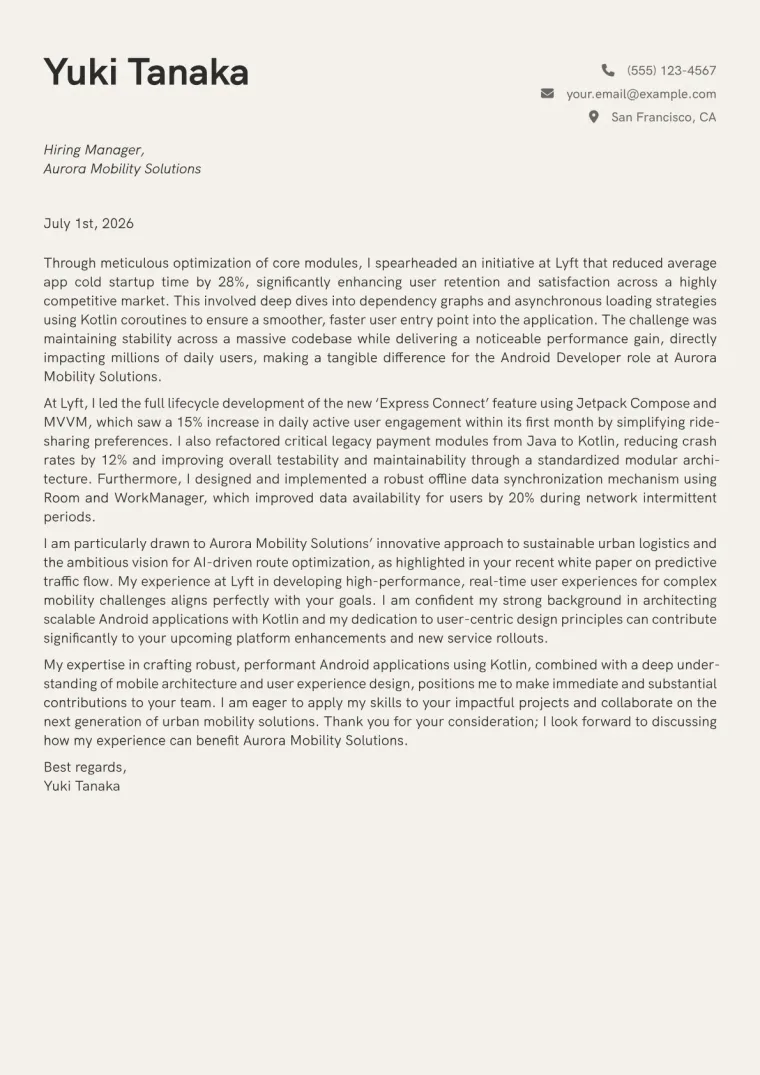
Yuki TanakaTo the Hiring Manager, Aetherial Solutions

At AWS, I spearheaded an initiative to re-architect security controls for a high-traffic serverless application suite, resulting in a 40% reduction in detected critical vulnerabilities over six months. This was critical for maintaining the integrity of customer data across millions of transactions daily, mitigating potential breaches that could impact our vast user base and reputation. My work involved deep dives into AWS Lambda, API Gateway, and S3 security configurations, enhancing their posture significantly under stringent compliance requirements.

My experience extends to designing and implementing robust security measures across diverse cloud environments. I developed and automated compliance checks for new AWS accounts using Python and AWS Config, decreasing manual review time by 30% and ensuring adherence to SOC 2 standards from day one. On Azure, I implemented a real-time threat detection system using Azure Security Center and Splunk, enabling our team to identify and respond to suspicious activities 50% faster through custom correlation rules. Additionally, I led the secure deployment strategy for Kubernetes clusters, hardening Docker images and configuring network policies to block unauthorized egress traffic.

My interest in Aetherial Solutions stems from your pioneering work in developing secure, scalable AI solutions across multi-cloud infrastructures, particularly your recent advancements in confidential computing on Azure. My extensive experience securing complex multi-cloud deployments, including AWS, Azure, and GCP, aligns perfectly with this vision. Specifically, my strength in designing robust security architectures for containerized applications and serverless functions would directly contribute to enhancing the integrity and resilience of your AI processing pipelines, ensuring data protection at scale.

My commitment to proactive security engineering and deep understanding of cloud-native environments, from infrastructure as code to serverless architectures, position me as a strong contributor to Aetherial Solutions. I am confident that my practical experience in mitigating sophisticated cloud threats and building resilient security frameworks would add immediate value to your team. I welcome the opportunity to discuss how my expertise can support your mission further in an interview.

Best regards,
Yuki Tanaka
Cloud Security Engineer cover letter for a career changer

Yuki TanakaTo the Hiring Manager, Vertex Logic

Unauthorized lateral movement attempts threatened our server architecture, requiring an immediate deployment of micro-segmentation policies using HashiCorp Consul to isolate sensitive databases. This initiative halted all suspicious traffic patterns and secured critical uptime for our main platform. My shift into cloud security builds directly on this foundation of hardening infrastructure and identifying vulnerabilities at the packet level. I am prepared to apply this rigorous oversight to your cloud environments, ensuring integrity from the ground up while maintaining the speed your developers require for constant delivery.

My approach to infrastructure security relies on repeatable, measurable results using industry-standard automation tools. I reduced unauthorized API access attempts by 35 percent by implementing robust Identity and Access Management roles across AWS environments using Terraform for consistent policy enforcement. I optimized log visibility for a complex containerized environment by integrating Splunk alerts into our existing Datadog dashboards, which cut incident response time by 20 percent during peak traffic hours. Finally, I hardened our Kubernetes clusters by enforcing strict network policies and image signing, which eliminated all previously identified container runtime vulnerabilities.

Vertex Logic stands out for your commitment to building security directly into your CI/CD pipelines through your OpenSource Shield framework. This focus aligns with my core strengths in infrastructure as code and automated vulnerability scanning. I possess the technical foresight to treat cloud security as a facilitator rather than a bottleneck. By prioritizing preventative architectural controls, I ensure that security posture scales alongside business demand. I view your approach to cloud native development as the ideal environment to contribute my specialized skills in hardening modern distributed systems and securing critical infrastructure.

The intersection of deep infrastructure knowledge and modern cloud security protocols informs every decision I make regarding system integrity. I am ready to bring this operational discipline to your security team and help build even more resilient cloud frameworks for your customers. Thank you for your time and for reviewing the technical depth of my background. Please review my attached portfolio to see my approach to securing distributed networks. I look forward to discussing how my unique experience in enterprise systems enhances your current security engineering strategy.

Best regards,
Yuki Tanaka

Cloud Security Engineer cover letter with no experience

Yuki TanakaTo the Hiring Manager, NexusCore Cloud Systems

Security policy enforcement through Terraform reduced identity and access management misconfigurations by 65 percent during my final semester capstone project at the University of Washington. By mapping AWS IAM roles to specific granular permissions, I neutralized privilege escalation risks that previously hindered the deployment of our student serverless architecture. This practical exercise solidified my technical proficiency in cloud infrastructure protection and prepared me for the rigors of an enterprise security landscape. My dedication to building secure configurations from the ground up defines my approach to the Cloud Security Engineer role at NexusCore Cloud Systems.

During my volunteer work at the Seattle Tech Cooperative, I utilized Splunk to detect and remediate five recurring brute force attacks on our exposed SSH endpoints within a thirty-day window. I also engineered a Docker container hardening workflow that achieved a CIS benchmark compliance score of 92 percent across thirty active microservices. Additionally, I implemented a Datadog monitoring dashboard that tracked real-time anomalous traffic patterns, which successfully alerted the engineering staff to three potential credential stuffing incidents. These efforts demonstrated my ability to integrate threat detection tools into existing CI/CD pipelines effectively.

NexusCore Cloud Systems distinguishes itself through the adoption of zero-trust architecture for multi-cloud environments, a mission that resonates with my focus on least privilege access. My primary strengths in Kubernetes orchestration security and cloud-native vulnerability management align directly with your current initiative to migrate legacy workloads into isolated serverless containers. I admire how the security team balances high-velocity deployment cycles with rigorous automated compliance checks. Contributing to your ongoing efforts to safeguard sensitive customer data while maintaining high availability represents the exact type of technical challenge I seek to solve daily.

My hands-on experience translates technical theory into tangible risk mitigation strategies that protect organizational assets. I bring a meticulous mindset toward threat modeling and a proactive stance on patching cloud infrastructure vulnerabilities. I am ready to discuss how my project-based achievements contribute to the continued security integrity of NexusCore Cloud Systems. Thank you for your time and consideration of my application for this role. I look forward to the possibility of contributing my skills to your security operations team and can be reached via phone or email for a follow-up interview.

Best regards,
Yuki Tanaka
Editorial Notes

Hiring managers in the technology sector look for concrete demonstrations of impact and specialized technical expertise in Cloud Security Engineer cover letters. Quantified achievements, such as reducing vulnerabilities or automating compliance, provide compelling evidence of capability. Specific experience with major cloud platforms like AWS and Azure, proficiency in tools like AWS Lambda, Azure Security Center, Kubernetes, and scripting languages such as Python, signal essential skills. Expertise in security architecture, compliance frameworks like SOC 2, and multi-cloud environments are crucial signals of a strong candidate.

This example letter excels by immediately grabbing attention with a quantified achievement: a 40% reduction in critical vulnerabilities. The subsequent paragraphs skillfully detail diverse technical experience, including re-architecting security controls, automating compliance checks with Python and AWS Config, and implementing real-time threat detection on Azure with Splunk. The letter then articulates a specific, well-researched interest in Aetherial Solutions' "secure, scalable AI solutions" and "confidential computing on Azure," drawing clear connections to the writer's multi-cloud and container security expertise. It closes with a confident assertion of value.

This example pairs effectively with JobSprout's Cloud Security Engineer resume guide and can be readily adapted using the JobSprout AI cover letter writer for personalized applications.

Frequently Asked Questions

What key skills and experiences should a Cloud Security Engineer highlight in a cover letter?
Focus on specific, quantifiable achievements in cloud security, such as reducing vulnerabilities, improving incident response times, or ensuring compliance. Detail your experience with cloud platforms like AWS, Azure, or GCP, and mention security tools (e.g., Splunk, Datadog) and methodologies you've used for hardening systems, securing containers, or implementing serverless security. Always provide context and results for each accomplishment.
What is the ideal length for a Cloud Security Engineer cover letter?
Aim for a concise, single-page letter, typically four substantial paragraphs. Each paragraph should be between 70-100 words, providing enough detail without becoming verbose. Recruiters appreciate brevity and directness, so ensure every sentence adds value and supports your candidacy for the specific role.
How should a Cloud Security Engineer open their cover letter to grab attention?
Instead of generic openings, start with a impactful, quantified achievement that directly relates to cloud security and the role's requirements. For example, highlight how you reduced critical vulnerabilities by a specific percentage or streamlined a key security process. This immediately showcases your value and prompts the reader to learn more about your capabilities.
How can someone address a lack of direct Cloud Security Engineer experience in their cover letter?
If direct experience is limited, emphasize transferable skills from related roles like Network Engineer or DevOps Engineer, focusing on security-centric projects. Highlight certifications (e.g., AWS Security Specialty, Azure Security Engineer Associate), personal projects involving cloud security, or relevant coursework. Demonstrate a strong understanding of cloud security principles, tools, and best practices, and articulate your eagerness to specialize.
How should a Cloud Security Engineer cover letter differ from their resume?
While the resume lists accomplishments concisely, the cover letter provides narrative and context. Use the letter to elaborate on 3-4 key achievements from your resume, explaining the challenges, your specific contributions, and the impact. Crucially, tailor the letter to the specific company and role, explaining *why* your skills are a perfect fit for their mission and challenges, which a resume cannot fully convey.

More Technology cover letter examples