Security Program Manager Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
Security Program Manager
Salary Range
Salary Trend
12-Month Trend
Based on advertised Security & Protection roles.
US market data · Source: Adzuna · Updated Sep 2026
How useful was this template?
Security Program Manager resume samples
Three complete resumes, each in a different design.
Free to use. No download fee.
What makes a strong Security Program Manager resume?
US median salary $135,098 ·
For a senior Security Program Manager role, hiring managers prioritize candidates who demonstrate strategic leadership, quantifiable impact, and comprehensive command of security governance. A resume should clearly articulate success in managing complex security programs, translating technical expertise into tangible business value. Essential elements include achievements related to risk mitigation, compliance adherence, budget management, and leading cross-functional teams. Relevant certifications like CISSP, CISM, and PMP are highly valued, underscoring both technical proficiency and program management acumen.
Why this example works
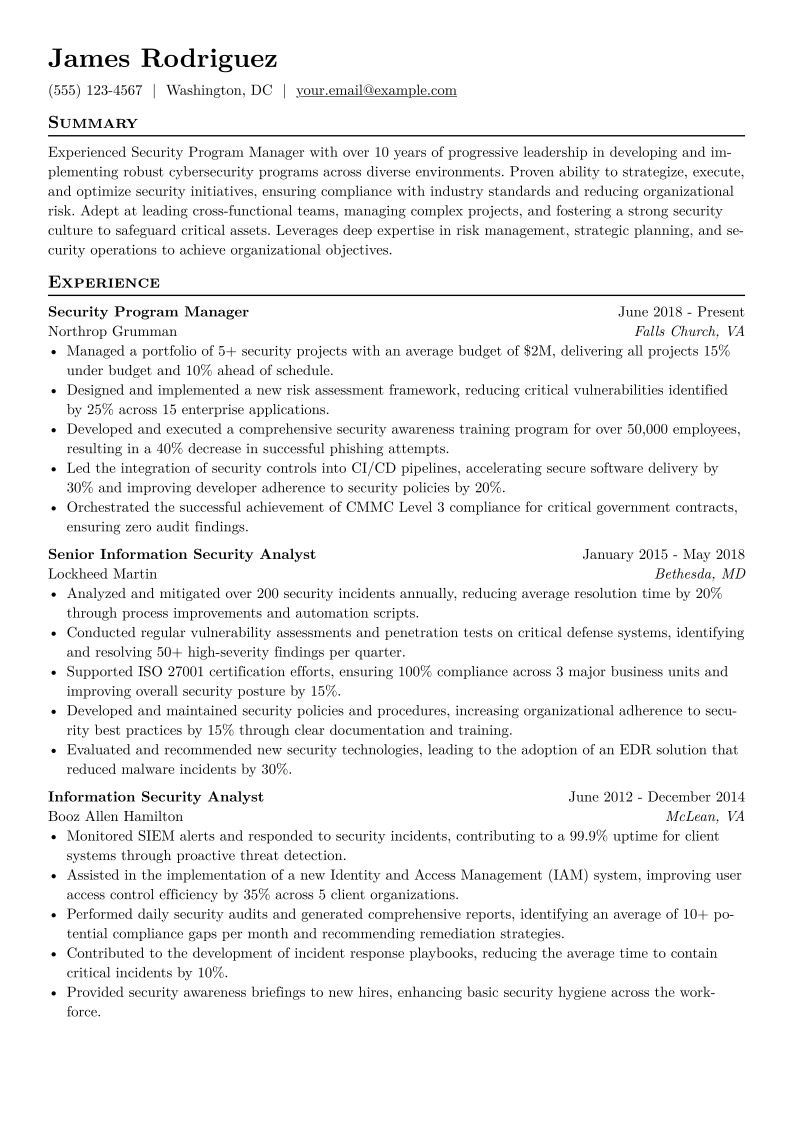
This example resume excels by highlighting James Rodriguez's progressive career and significant accomplishments. The “Experience” section effectively quantifies impact, noting achievements like “delivering all projects 15% under budget and 10% ahead of schedule” and “reducing critical vulnerabilities identified by 25%.” The “Skills” section is comprehensive, categorizing diverse capabilities from “Security Program & Risk Management” to “Compliance & Frameworks.” Furthermore, the inclusion of key certifications such as CISSP, CISM, PMP, and CRISC immediately establishes a strong professional foundation.
Security Program Manager resume example (text version)
James Rodriguez · Security Program Manager
Summary
Experienced Security Program Manager with over 10 years of progressive leadership in developing and implementing robust cybersecurity programs across diverse environments. Proven ability to strategize, execute, and optimize security initiatives, ensuring compliance with industry standards and reducing organizational risk. Adept at leading cross-functional teams, managing complex projects, and fostering a strong security culture to safeguard critical assets. Leverages deep expertise in risk management, strategic planning, and security operations to achieve organizational objectives.
Experience
Security Program Manager · Northrop Grumman
Falls Church, VA · 2018 - Present
- Managed a portfolio of 5+ security projects with an average budget of $2M, delivering all projects 15% under budget and 10% ahead of schedule.
- Designed and implemented a new risk assessment framework, reducing critical vulnerabilities identified by 25% across 15 enterprise applications.
- Developed and executed a comprehensive security awareness training program for over 50,000 employees, resulting in a 40% decrease in successful phishing attempts.
- Led the integration of security controls into CI/CD pipelines, accelerating secure software delivery by 30% and improving developer adherence to security policies by 20%.
- Orchestrated the successful achievement of CMMC Level 3 compliance for critical government contracts, ensuring zero audit findings.
Senior Information Security Analyst · Lockheed Martin
Bethesda, MD · 2015 - 2018
- Analyzed and mitigated over 200 security incidents annually, reducing average resolution time by 20% through process improvements and automation scripts.
- Conducted regular vulnerability assessments and penetration tests on critical defense systems, identifying and resolving 50+ high-severity findings per quarter.
- Supported ISO 27001 certification efforts, ensuring 100% compliance across 3 major business units and improving overall security posture by 15%.
- Developed and maintained security policies and procedures, increasing organizational adherence to security best practices by 15% through clear documentation and training.
- Evaluated and recommended new security technologies, leading to the adoption of an EDR solution that reduced malware incidents by 30%.
Information Security Analyst · Booz Allen Hamilton
McLean, VA · 2012 - 2014
- Monitored SIEM alerts and responded to security incidents, contributing to a 99.9% uptime for client systems through proactive threat detection.
- Assisted in the implementation of a new Identity and Access Management (IAM) system, improving user access control efficiency by 35% across 5 client organizations.
- Performed daily security audits and generated comprehensive reports, identifying an average of 10+ potential compliance gaps per month and recommending remediation strategies.
- Contributed to the development of incident response playbooks, reducing the average time to contain critical incidents by 10%.
- Provided security awareness briefings to new hires, enhancing basic security hygiene across the workforce.
Education
Master of Science in Cybersecurity · George Washington University
Washington, D.C. · 2012 - 2014
- Graduated with a 3.9 GPA, focusing on Advanced Persistent Threat (APT) defense strategies
- Completed capstone project: 'Secure Cloud Migration Framework for Government Agencies'
- Published research paper on 'Zero Trust Architecture Implementation Challenges' in university journal
Bachelor of Science in Computer Science · University of Maryland
College Park, MD · 2008 - 2012
- Achieved Dean's List recognition for six semesters for academic excellence
- Served as Treasurer for the Cyber Defense Club, organizing monthly hackathon events
- Developed a secure file transfer protocol as part of senior design project
Skills
Security Program Manager resume example: Security Program
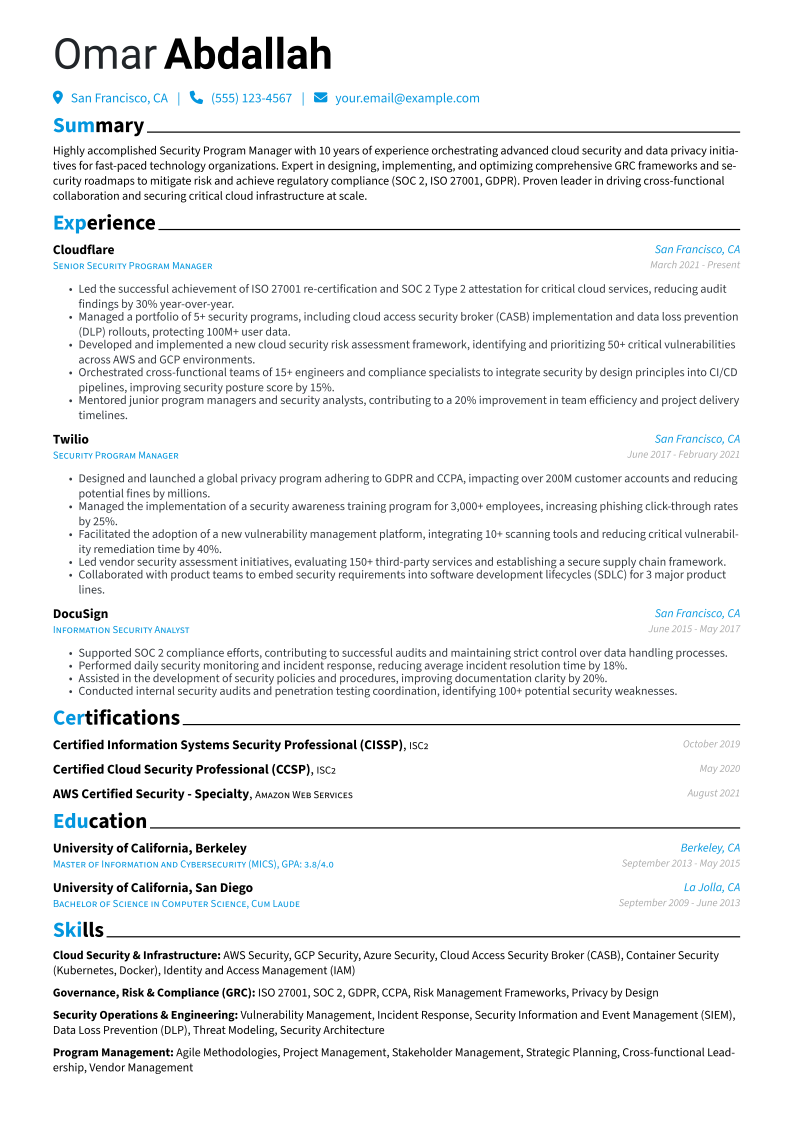
Omar Abdallah · Security Program Manager
Summary
Highly accomplished Security Program Manager with 10 years of experience orchestrating advanced cloud security and data privacy initiatives for fast-paced technology organizations. Expert in designing, implementing, and optimizing comprehensive GRC frameworks and security roadmaps to mitigate risk and achieve regulatory compliance (SOC 2, ISO 27001, GDPR). Proven leader in driving cross-functional collaboration and securing critical cloud infrastructure at scale.
Experience
Senior Security Program Manager · Cloudflare
San Francisco, CA · 2021 - Present
- Led the successful achievement of ISO 27001 re-certification and SOC 2 Type 2 attestation for critical cloud services, reducing audit findings by 30% year-over-year.
- Managed a portfolio of 5+ security programs, including cloud access security broker (CASB) implementation and data loss prevention (DLP) rollouts, protecting 100M+ user data.
- Developed and implemented a new cloud security risk assessment framework, identifying and prioritizing 50+ critical vulnerabilities across AWS and GCP environments.
- Orchestrated cross-functional teams of 15+ engineers and compliance specialists to integrate security by design principles into CI/CD pipelines, improving security posture score by 15%.
- Mentored junior program managers and security analysts, contributing to a 20% improvement in team efficiency and project delivery timelines.
Security Program Manager · Twilio
San Francisco, CA · 2017 - 2021
- Designed and launched a global privacy program adhering to GDPR and CCPA, impacting over 200M customer accounts and reducing potential fines by millions.
- Managed the implementation of a security awareness training program for 3,000+ employees, increasing phishing click-through rates by 25%.
- Facilitated the adoption of a new vulnerability management platform, integrating 10+ scanning tools and reducing critical vulnerability remediation time by 40%.
- Led vendor security assessment initiatives, evaluating 150+ third-party services and establishing a secure supply chain framework.
- Collaborated with product teams to embed security requirements into software development lifecycles (SDLC) for 3 major product lines.
Information Security Analyst · DocuSign
San Francisco, CA · 2015 - 2017
- Supported SOC 2 compliance efforts, contributing to successful audits and maintaining strict control over data handling processes.
- Performed daily security monitoring and incident response, reducing average incident resolution time by 18%.
- Assisted in the development of security policies and procedures, improving documentation clarity by 20%.
- Conducted internal security audits and penetration testing coordination, identifying 100+ potential security weaknesses.
Education
Master of Information and Cybersecurity (MICS), GPA: 3.8/4.0 · University of California, Berkeley
Berkeley, CA · 2013 - 2015
Bachelor of Science in Computer Science, Cum Laude · University of California, San Diego
La Jolla, CA · 2009 - 2013
Skills
Security Program Manager resume example: Career Changer
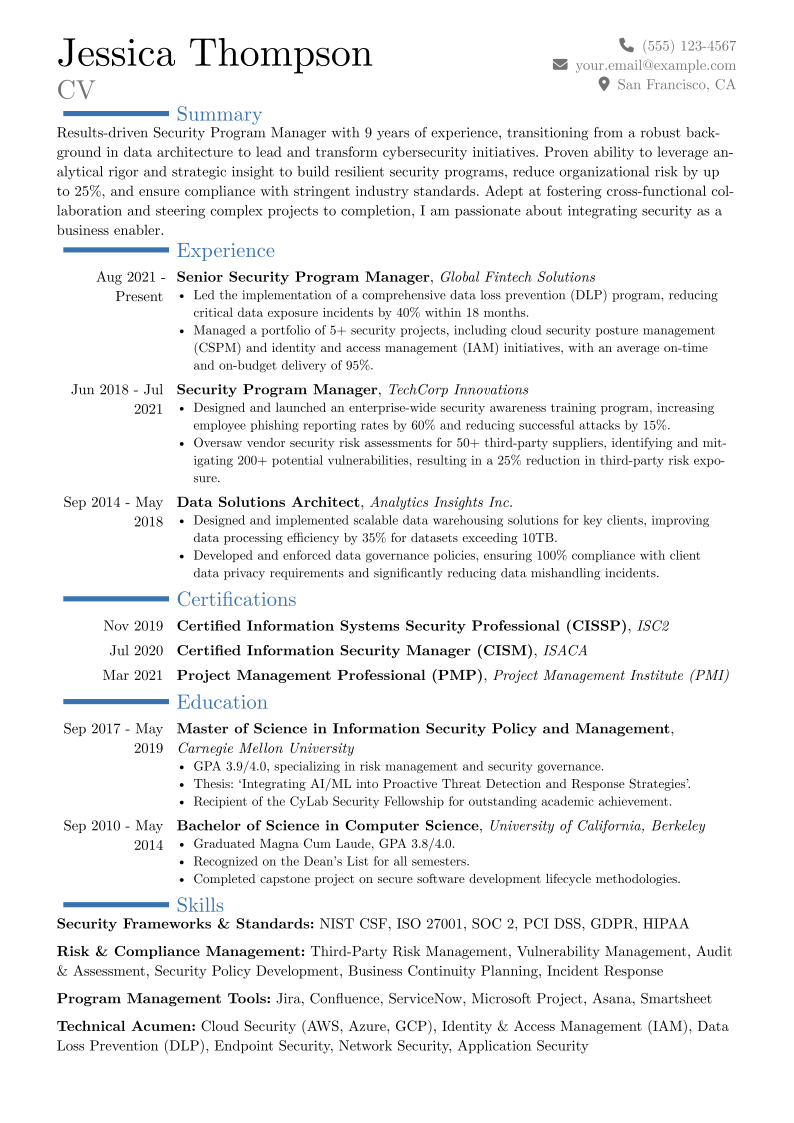
Jessica Thompson · Security Program Manager
Summary
Results-driven Security Program Manager with 9 years of experience, transitioning from a robust background in data architecture to lead and transform cybersecurity initiatives. Proven ability to leverage analytical rigor and strategic insight to build resilient security programs, reduce organizational risk by up to 25%, and ensure compliance with stringent industry standards. Adept at fostering cross-functional collaboration and steering complex projects to completion, I am passionate about integrating security as a business enabler.
Experience
Senior Security Program Manager · Global Fintech Solutions
San Francisco, CA · 2021 - Present
- Led the implementation of a comprehensive data loss prevention (DLP) program, reducing critical data exposure incidents by 40% within 18 months.
- Managed a portfolio of 5+ security projects, including cloud security posture management (CSPM) and identity and access management (IAM) initiatives, with an average on-time and on-budget delivery of 95%.
- Developed and maintained security roadmaps aligned with business objectives, achieving a 20% improvement in security control effectiveness scores in annual audits.
- Facilitated cross-functional teams of up to 15 engineers and analysts, enhancing collaboration and communication across security, engineering, and compliance departments.
Security Program Manager · TechCorp Innovations
San Jose, CA · 2018 - 2021
- Designed and launched an enterprise-wide security awareness training program, increasing employee phishing reporting rates by 60% and reducing successful attacks by 15%.
- Oversaw vendor security risk assessments for 50+ third-party suppliers, identifying and mitigating 200+ potential vulnerabilities, resulting in a 25% reduction in third-party risk exposure.
- Managed the remediation of findings from penetration tests and vulnerability scans, reducing the average time to resolution for critical issues by 30%.
- Successfully guided the company through its first SOC 2 Type 2 audit, achieving compliance within 12 months.
Data Solutions Architect · Analytics Insights Inc.
Palo Alto, CA · 2014 - 2018
- Designed and implemented scalable data warehousing solutions for key clients, improving data processing efficiency by 35% for datasets exceeding 10TB.
- Developed and enforced data governance policies, ensuring 100% compliance with client data privacy requirements and significantly reducing data mishandling incidents.
- Optimized database performance and query execution, resulting in a 20% reduction in reporting generation times for critical business intelligence dashboards.
- Mentored a team of 5 junior data engineers, fostering their growth in secure coding practices and database management.
Education
Master of Science in Information Security Policy and Management · Carnegie Mellon University
Pittsburgh, PA · 2017 - 2019
- GPA 3.9/4.0, specializing in risk management and security governance.
- Thesis: 'Integrating AI/ML into Proactive Threat Detection and Response Strategies'.
- Recipient of the CyLab Security Fellowship for outstanding academic achievement.
Bachelor of Science in Computer Science · University of California, Berkeley
Berkeley, CA · 2010 - 2014
- Graduated Magna Cum Laude, GPA 3.8/4.0.
- Recognized on the Dean's List for all semesters.
- Completed capstone project on secure software development lifecycle methodologies.
Skills
How useful was this template?
Example by JobSproutSecurity Program Manager resume summary example
Experienced Security Program Manager with over 10 years of progressive leadership in developing and implementing robust cybersecurity programs across diverse environments. Proven ability to strategize, execute, and optimize security initiatives, ensuring compliance with industry standards and reducing organizational risk. Adept at leading cross-functional teams, managing complex projects, and fostering a strong security culture to safeguard critical assets. Leverages deep expertise in risk management, strategic planning, and security operations to achieve organizational objectives.
Security Program Manager salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $100,000 | $135,098 | $148,705 |
| UK | £60,000 | £64,667 | £69,333 |
| Canada | C$122,667 | C$130,667 | C$138,667 |
| Australia | A$87,500 | A$95,000 | A$120,300 |
| Germany | €61,700 | €70,336 | €72,998 |
| France | €41,830 | €47,991 | €58,158 |
| Netherlands | €47,841 | €60,081 | €69,292 |
| Italy | €23,689 | €31,923 | €52,750 |
| Austria | €38,750 | €62,500 | €72,246 |
| New Zealand | NZ$85,156 | NZ$111,806 | NZ$133,523 |
| India | ₹1,187,500 | ₹1,625,000 | ₹2,500,000 |
| Poland | zł159,483 | zł201,141 | zł226,462 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
Security Program Manager resume skills and keywords
Recruiters and applicant tracking systems scan Security Program Manager resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
Security Program Manager
Salary Range
Salary Trend
12-Month Trend
Based on advertised Security & Protection roles.
US market data · Source: Adzuna · Updated Sep 2026
Frequently Asked Questions
What's the best resume structure for a senior Security Program Manager?
Which skills and qualifications should I highlight for this role?
How can I write strong achievement bullets or a compelling professional summary?
Which optional resume sections are most important for a Security Program Manager?
How can I tailor my resume for a specific Security Program Manager job posting?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Career moves from Security Program Manager
Usually need less experience or training
Includes information from the O*NET 30.3 Database by the U.S. Department of Labor, Employment and Training Administration (USDOL/ETA), used under the CC BY 4.0 license. We have modified it; USDOL/ETA has not approved, endorsed or tested these modifications. O*NET is a trademark of USDOL/ETA.