CISO Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
CISO
Salary Range
Salary Trend
12-Month Trend
Based on advertised IT & Cybersecurity roles.
US market data · Source: Adzuna · Updated Sep 2026
How useful was this template?
CISO resume samples
Three complete resumes, each in a different design.
Free to use. No download fee.
What makes a strong CISO resume?
US median salary $154,050 ·
A robust CISO resume in Technology must clearly articulate strategic leadership, deep technical understanding, and quantifiable impact in managing complex cyber risks. Hiring managers seek evidence of experience in establishing proactive security postures, navigating stringent regulatory landscapes like SOC 2, ISO 27001, GDPR, PCI DSS, and HIPAA, and leading diverse security teams. Demonstrating achievements through metrics, such as reducing attack surfaces, optimizing budgets, or improving incident resolution times, is crucial. Moreover, familiarity with advanced security architectures like zero-trust, and proficiency with technologies like SIEM, EDR/XDR, and multi-cloud security (AWS, Azure) are vital for this executive-level role.
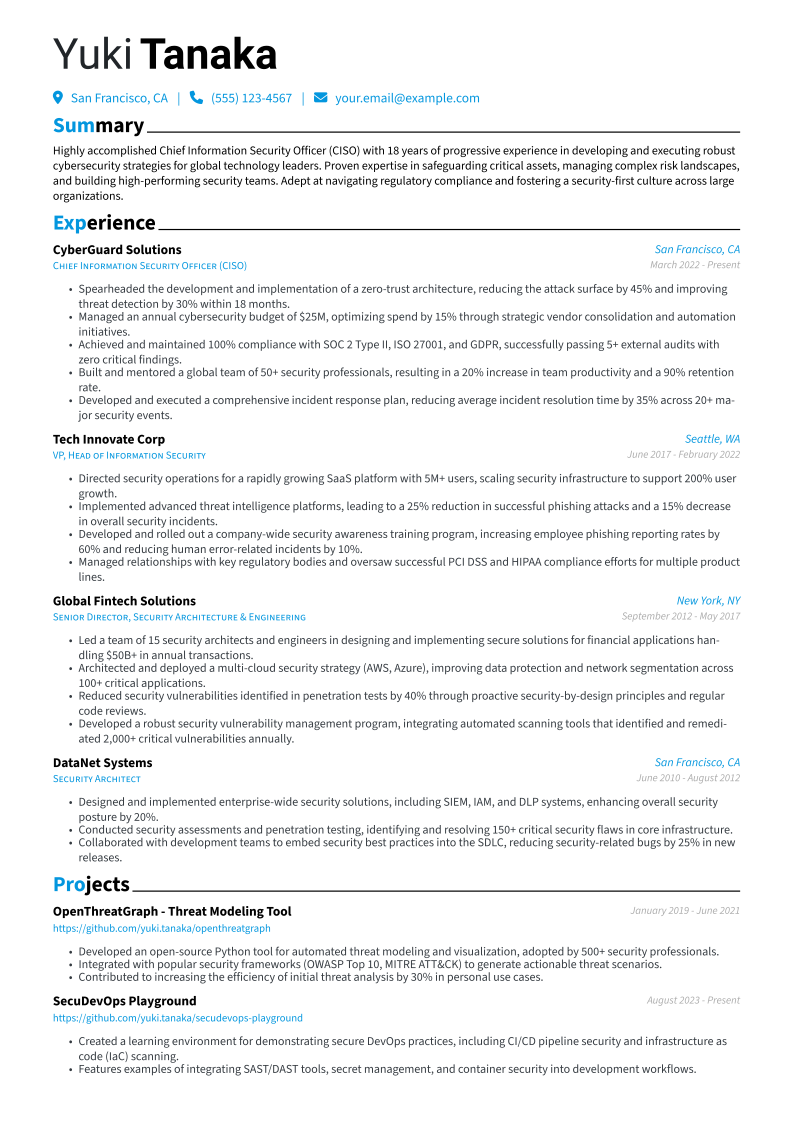
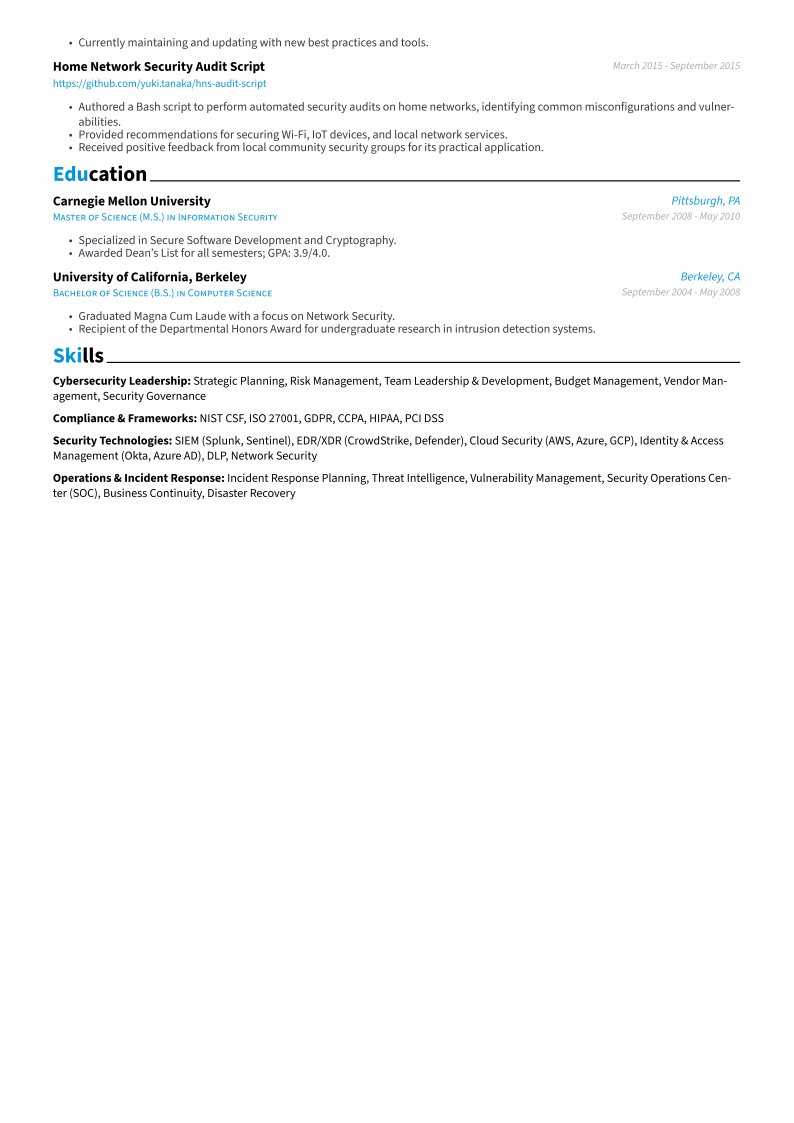
Why this example works
Yuki Tanaka's resume effectively showcases these critical elements, making a compelling case for executive leadership. The “Experience” section highlights significant achievements with precise metrics, such as spearheading a zero-trust architecture that “reduced the attack surface by 45%” and “optimizing spend by 15%” on a $25M budget. Her ability to “Achieved and maintained 100% compliance with SOC 2 Type II, ISO 27001, and GDPR” across multiple audits underscores her governance expertise. Furthermore, the resume details her success in team development, having “Built and mentored a global team of 50+ security professionals,” alongside a dedicated “Projects” section that emphasizes continuous innovation in areas like threat modeling.
CISO resume example (text version)
Yuki Tanaka · CISO
Summary
Highly accomplished Chief Information Security Officer (CISO) with 18 years of progressive experience in developing and executing robust cybersecurity strategies for global technology leaders. Proven expertise in safeguarding critical assets, managing complex risk landscapes, and building high-performing security teams. Adept at navigating regulatory compliance and fostering a security-first culture across large organizations.
Experience
Chief Information Security Officer (CISO) · CyberGuard Solutions
San Francisco, CA · 2022 - Present
- Spearheaded the development and implementation of a zero-trust architecture, reducing the attack surface by 45% and improving threat detection by 30% within 18 months.
- Managed an annual cybersecurity budget of $25M, optimizing spend by 15% through strategic vendor consolidation and automation initiatives.
- Achieved and maintained 100% compliance with SOC 2 Type II, ISO 27001, and GDPR, successfully passing 5+ external audits with zero critical findings.
- Built and mentored a global team of 50+ security professionals, resulting in a 20% increase in team productivity and a 90% retention rate.
- Developed and executed a comprehensive incident response plan, reducing average incident resolution time by 35% across 20+ major security events.
VP, Head of Information Security · Tech Innovate Corp
Seattle, WA · 2017 - 2022
- Directed security operations for a rapidly growing SaaS platform with 5M+ users, scaling security infrastructure to support 200% user growth.
- Implemented advanced threat intelligence platforms, leading to a 25% reduction in successful phishing attacks and a 15% decrease in overall security incidents.
- Developed and rolled out a company-wide security awareness training program, increasing employee phishing reporting rates by 60% and reducing human error-related incidents by 10%.
- Managed relationships with key regulatory bodies and oversaw successful PCI DSS and HIPAA compliance efforts for multiple product lines.
Senior Director, Security Architecture & Engineering · Global Fintech Solutions
New York, NY · 2012 - 2017
- Led a team of 15 security architects and engineers in designing and implementing secure solutions for financial applications handling $50B+ in annual transactions.
- Architected and deployed a multi-cloud security strategy (AWS, Azure), improving data protection and network segmentation across 100+ critical applications.
- Reduced security vulnerabilities identified in penetration tests by 40% through proactive security-by-design principles and regular code reviews.
- Developed a robust security vulnerability management program, integrating automated scanning tools that identified and remediated 2,000+ critical vulnerabilities annually.
Security Architect · DataNet Systems
San Francisco, CA · 2010 - 2012
- Designed and implemented enterprise-wide security solutions, including SIEM, IAM, and DLP systems, enhancing overall security posture by 20%.
- Conducted security assessments and penetration testing, identifying and resolving 150+ critical security flaws in core infrastructure.
- Collaborated with development teams to embed security best practices into the SDLC, reducing security-related bugs by 25% in new releases.
Education
Master of Science (M.S.) in Information Security · Carnegie Mellon University
Pittsburgh, PA · 2008 - 2010
- Specialized in Secure Software Development and Cryptography.
- Awarded Dean's List for all semesters; GPA: 3.9/4.0.
Bachelor of Science (B.S.) in Computer Science · University of California, Berkeley
Berkeley, CA · 2004 - 2008
- Graduated Magna Cum Laude with a focus on Network Security.
- Recipient of the Departmental Honors Award for undergraduate research in intrusion detection systems.
Skills
CISO resume example: Executive CISO
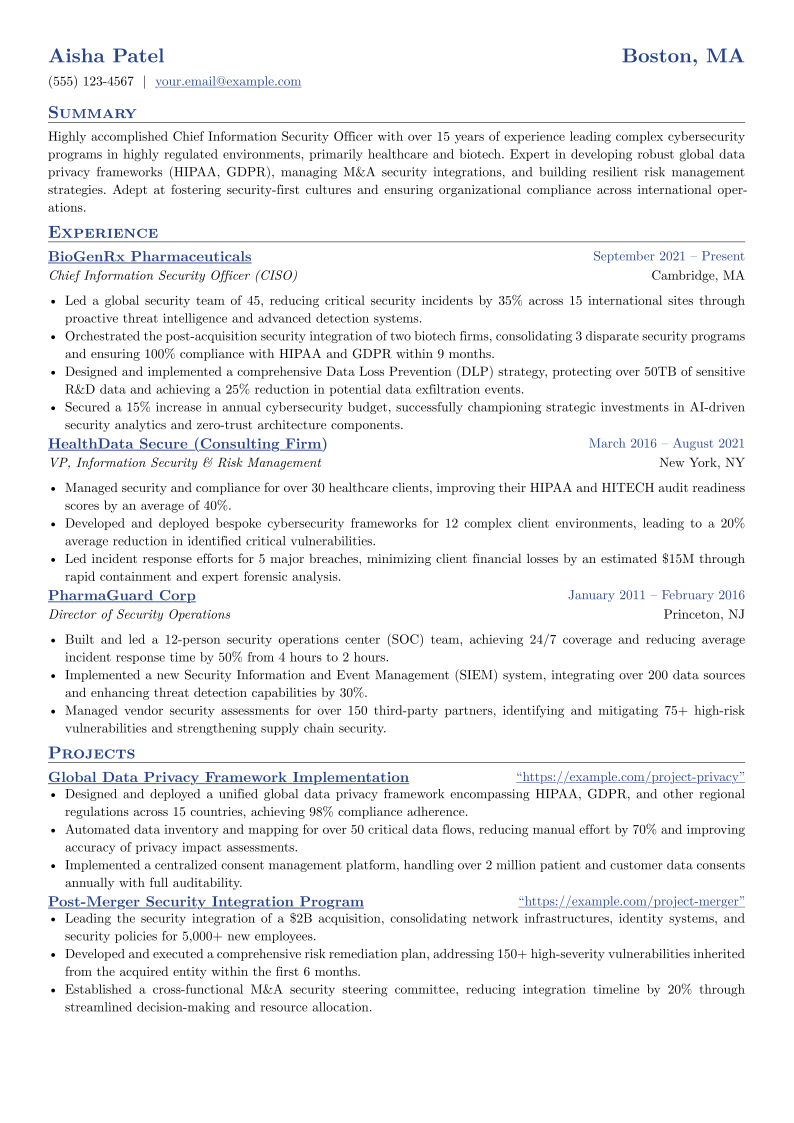
Aisha Patel · CISO
Summary
Highly accomplished Chief Information Security Officer with over 15 years of experience leading complex cybersecurity programs in highly regulated environments, primarily healthcare and biotech. Expert in developing robust global data privacy frameworks (HIPAA, GDPR), managing M&A security integrations, and building resilient risk management strategies. Adept at fostering security-first cultures and ensuring organizational compliance across international operations.
Experience
Chief Information Security Officer (CISO) · BioGenRx Pharmaceuticals
Cambridge, MA · 2021 - Present
- Led a global security team of 45, reducing critical security incidents by 35% across 15 international sites through proactive threat intelligence and advanced detection systems.
- Orchestrated the post-acquisition security integration of two biotech firms, consolidating 3 disparate security programs and ensuring 100% compliance with HIPAA and GDPR within 9 months.
- Designed and implemented a comprehensive Data Loss Prevention (DLP) strategy, protecting over 50TB of sensitive R&D data and achieving a 25% reduction in potential data exfiltration events.
- Secured a 15% increase in annual cybersecurity budget, successfully championing strategic investments in AI-driven security analytics and zero-trust architecture components.
VP, Information Security & Risk Management · HealthData Secure (Consulting Firm)
New York, NY · 2016 - 2021
- Managed security and compliance for over 30 healthcare clients, improving their HIPAA and HITECH audit readiness scores by an average of 40%.
- Developed and deployed bespoke cybersecurity frameworks for 12 complex client environments, leading to a 20% average reduction in identified critical vulnerabilities.
- Led incident response efforts for 5 major breaches, minimizing client financial losses by an estimated $15M through rapid containment and expert forensic analysis.
Director of Security Operations · PharmaGuard Corp
Princeton, NJ · 2011 - 2016
- Built and led a 12-person security operations center (SOC) team, achieving 24/7 coverage and reducing average incident response time by 50% from 4 hours to 2 hours.
- Implemented a new Security Information and Event Management (SIEM) system, integrating over 200 data sources and enhancing threat detection capabilities by 30%.
- Managed vendor security assessments for over 150 third-party partners, identifying and mitigating 75+ high-risk vulnerabilities and strengthening supply chain security.
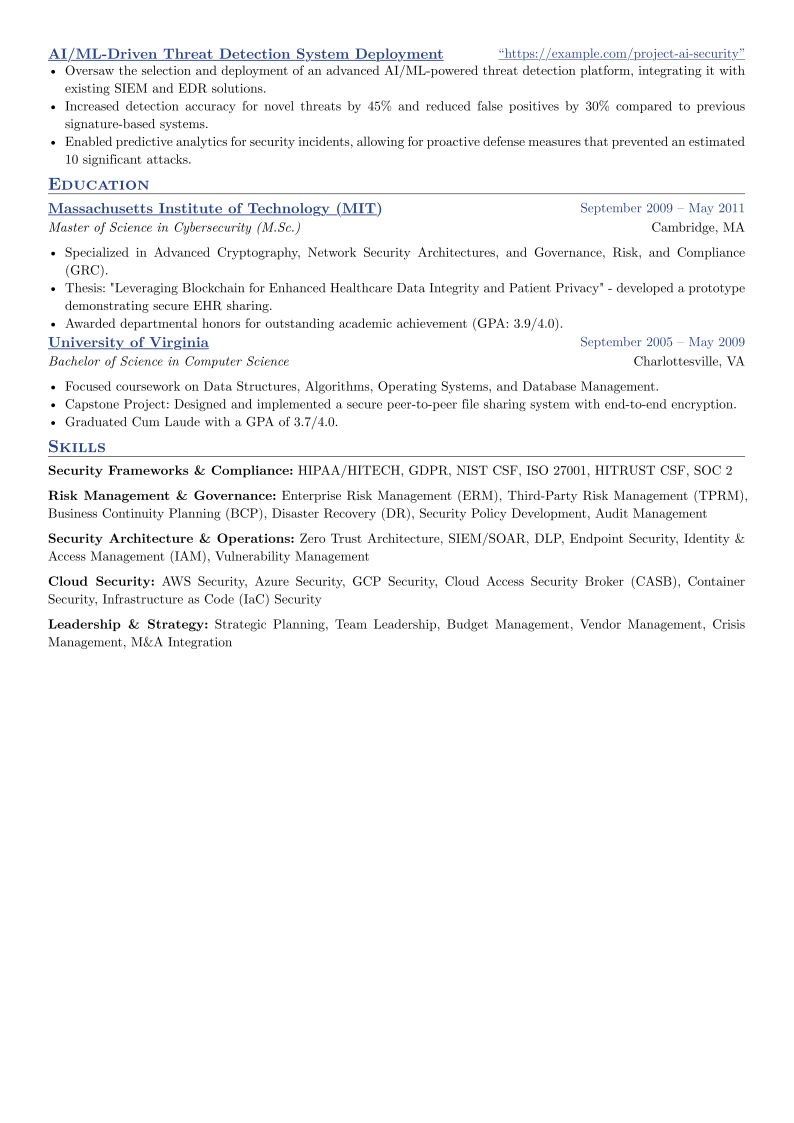
Education
Master of Science in Cybersecurity (M.Sc.) · Massachusetts Institute of Technology (MIT)
Cambridge, MA · 2009 - 2011
- Specialized in Advanced Cryptography, Network Security Architectures, and Governance, Risk, and Compliance (GRC).
- Thesis: "Leveraging Blockchain for Enhanced Healthcare Data Integrity and Patient Privacy" - developed a prototype demonstrating secure EHR sharing.
- Awarded departmental honors for outstanding academic achievement (GPA: 3.9/4.0).
Bachelor of Science in Computer Science · University of Virginia
Charlottesville, VA · 2005 - 2009
- Focused coursework on Data Structures, Algorithms, Operating Systems, and Database Management.
- Capstone Project: Designed and implemented a secure peer-to-peer file sharing system with end-to-end encryption.
- Graduated Cum Laude with a GPA of 3.7/4.0.
Skills
CISO resume example: Career Changer
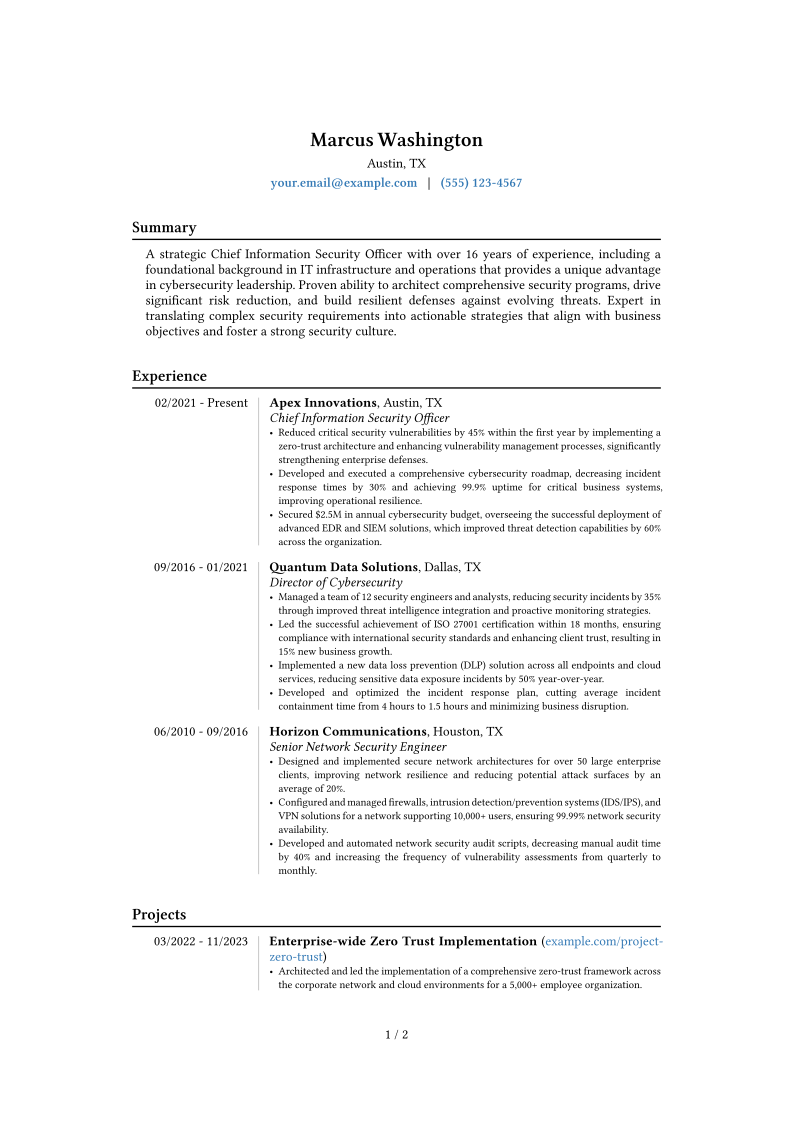
Marcus Washington · CISO
Summary
A strategic Chief Information Security Officer with over 16 years of experience, including a foundational background in IT infrastructure and operations that provides a unique advantage in cybersecurity leadership. Proven ability to architect comprehensive security programs, drive significant risk reduction, and build resilient defenses against evolving threats. Expert in translating complex security requirements into actionable strategies that align with business objectives and foster a strong security culture.
Experience
Chief Information Security Officer · Apex Innovations
Austin, TX · 2021 - Present
- Reduced critical security vulnerabilities by 45% within the first year by implementing a zero-trust architecture and enhancing vulnerability management processes, significantly strengthening enterprise defenses.
- Developed and executed a comprehensive cybersecurity roadmap, decreasing incident response times by 30% and achieving 99.9% uptime for critical business systems, improving operational resilience.
- Secured $2.5M in annual cybersecurity budget, overseeing the successful deployment of advanced EDR and SIEM solutions, which improved threat detection capabilities by 60% across the organization.
- Cultivated a security-aware culture through mandatory annual training, increasing employee phishing reporting rates by 70% and reducing successful phishing attacks by 25%.
Director of Cybersecurity · Quantum Data Solutions
Dallas, TX · 2016 - 2021
- Managed a team of 12 security engineers and analysts, reducing security incidents by 35% through improved threat intelligence integration and proactive monitoring strategies.
- Led the successful achievement of ISO 27001 certification within 18 months, ensuring compliance with international security standards and enhancing client trust, resulting in 15% new business growth.
- Implemented a new data loss prevention (DLP) solution across all endpoints and cloud services, reducing sensitive data exposure incidents by 50% year-over-year.
- Developed and optimized the incident response plan, cutting average incident containment time from 4 hours to 1.5 hours and minimizing business disruption.
Senior Network Security Engineer · Horizon Communications
Houston, TX · 2010 - 2016
- Designed and implemented secure network architectures for over 50 large enterprise clients, improving network resilience and reducing potential attack surfaces by an average of 20%.
- Configured and managed firewalls, intrusion detection/prevention systems (IDS/IPS), and VPN solutions for a network supporting 10,000+ users, ensuring 99.99% network security availability.
- Developed and automated network security audit scripts, decreasing manual audit time by 40% and increasing the frequency of vulnerability assessments from quarterly to monthly.
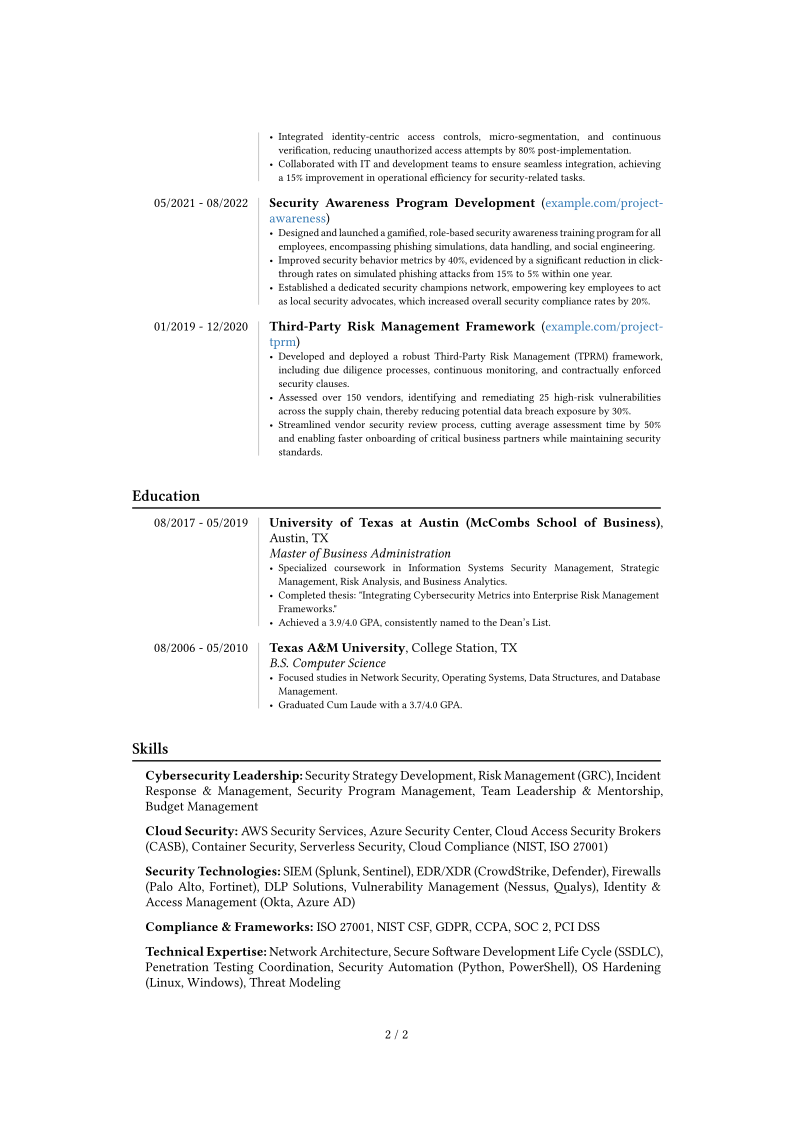
Education
Master of Business Administration · University of Texas at Austin (McCombs School of Business)
Austin, TX · 2017 - 2019
- Specialized coursework in Information Systems Security Management, Strategic Management, Risk Analysis, and Business Analytics.
- Completed thesis: "Integrating Cybersecurity Metrics into Enterprise Risk Management Frameworks."
- Achieved a 3.9/4.0 GPA, consistently named to the Dean's List.
B.S. Computer Science · Texas A&M University
College Station, TX · 2006 - 2010
- Focused studies in Network Security, Operating Systems, Data Structures, and Database Management.
- Graduated Cum Laude with a 3.7/4.0 GPA.
Skills
How useful was this template?
Example by JobSproutCISO resume summary example
Highly accomplished Chief Information Security Officer (CISO) with 18 years of progressive experience in developing and executing robust cybersecurity strategies for global technology leaders. Proven expertise in safeguarding critical assets, managing complex risk landscapes, and building high-performing security teams. Adept at navigating regulatory compliance and fostering a security-first culture across large organizations.
CISO salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $120,500 | $154,050 | $175,927 |
| Canada | C$130,000 | C$140,000 | C$150,000 |
| Australia | A$89,250 | A$98,500 | A$107,750 |
| India | ₹333,333 | ₹666,667 | ₹1,000,000 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
CISO resume skills and keywords
Recruiters and applicant tracking systems scan CISO resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
CISO
Salary Range
Salary Trend
12-Month Trend
Based on advertised IT & Cybersecurity roles.
US market data · Source: Adzuna · Updated Sep 2026
Frequently Asked Questions
What is the ideal resume layout for an executive Chief Information Security Officer?
What leadership and strategic skills must be highlighted on a CISO resume?
How do I frame CISO achievements to demonstrate business value?
What optional sections should appear on an executive CISO resume?
How do I adapt my executive CISO resume for different tech companies using JobSprout?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Related Articles
Cybersecurity Analyst Resume: Examples & Skills to Include (2026)
Write a cybersecurity resume that lands interviews. Resume examples, technical skills tables, certification guidance, and bullet point formulas for SOC analysts, pen testers, security engineers, and GRC roles.

How to Write a CV for Tech Applications [2026 Guide]
Learn how to write a software engineering CV that gets interviews. Real template analysis, what hiring managers look for, and common mistakes to avoid.

How to Write a CV That Shows Startup Experience [2026 Guide]
Learn how to write a CV that showcases founding engineer and startup experience. Real example from JobSprout's creator, what hiring managers look for, and how to position breadth as a strength.