Privacy Officer Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
Privacy Officer
Salary Range
Salary Trend
12-Month Trend
Based on advertised Legal roles.
US market data · Source: Adzuna · Updated Mar 2026
How useful was this template?
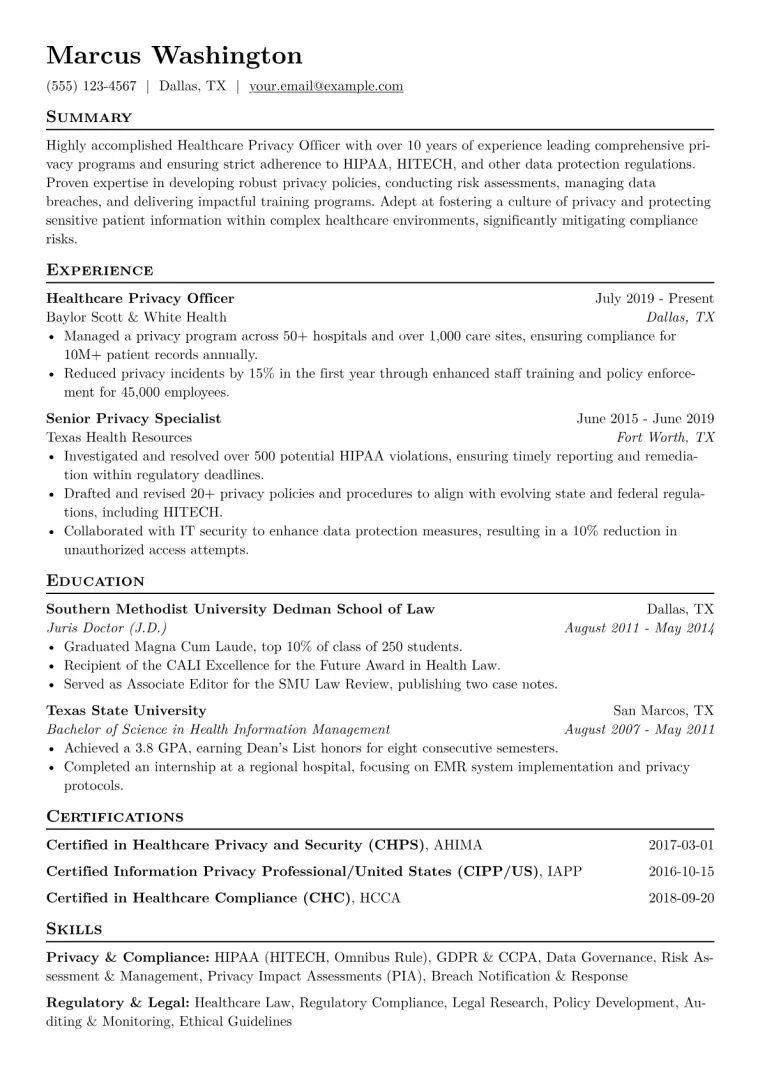
Privacy Officer resume samples
Three complete resumes, each in a different design.
Free to use. No download fee.
What makes a strong Privacy Officer resume?
US median salary $99,500 ·
Crafting a compelling Privacy Officer resume for the legal industry requires showcasing a robust understanding of compliance frameworks, data governance, and risk management. Hiring managers in Legal prioritize candidates who can translate intricate regulations into actionable policies and effectively manage sensitive information, often looking for specific jurisdictional expertise and a proactive approach to evolving privacy landscapes.
Why this example works
This JobSprout example effectively highlights those critical aspects by featuring quantified achievements that demonstrate impact on legal compliance and data security. Its clear skills grouping separates technical expertise from legal and regulatory knowledge, while prominently displaying relevant certifications like CIPP/US or CIPM. This structure allows recruiters to quickly assess a candidate's readiness for a mid-level legal privacy role.
Privacy Officer resume example (text version)
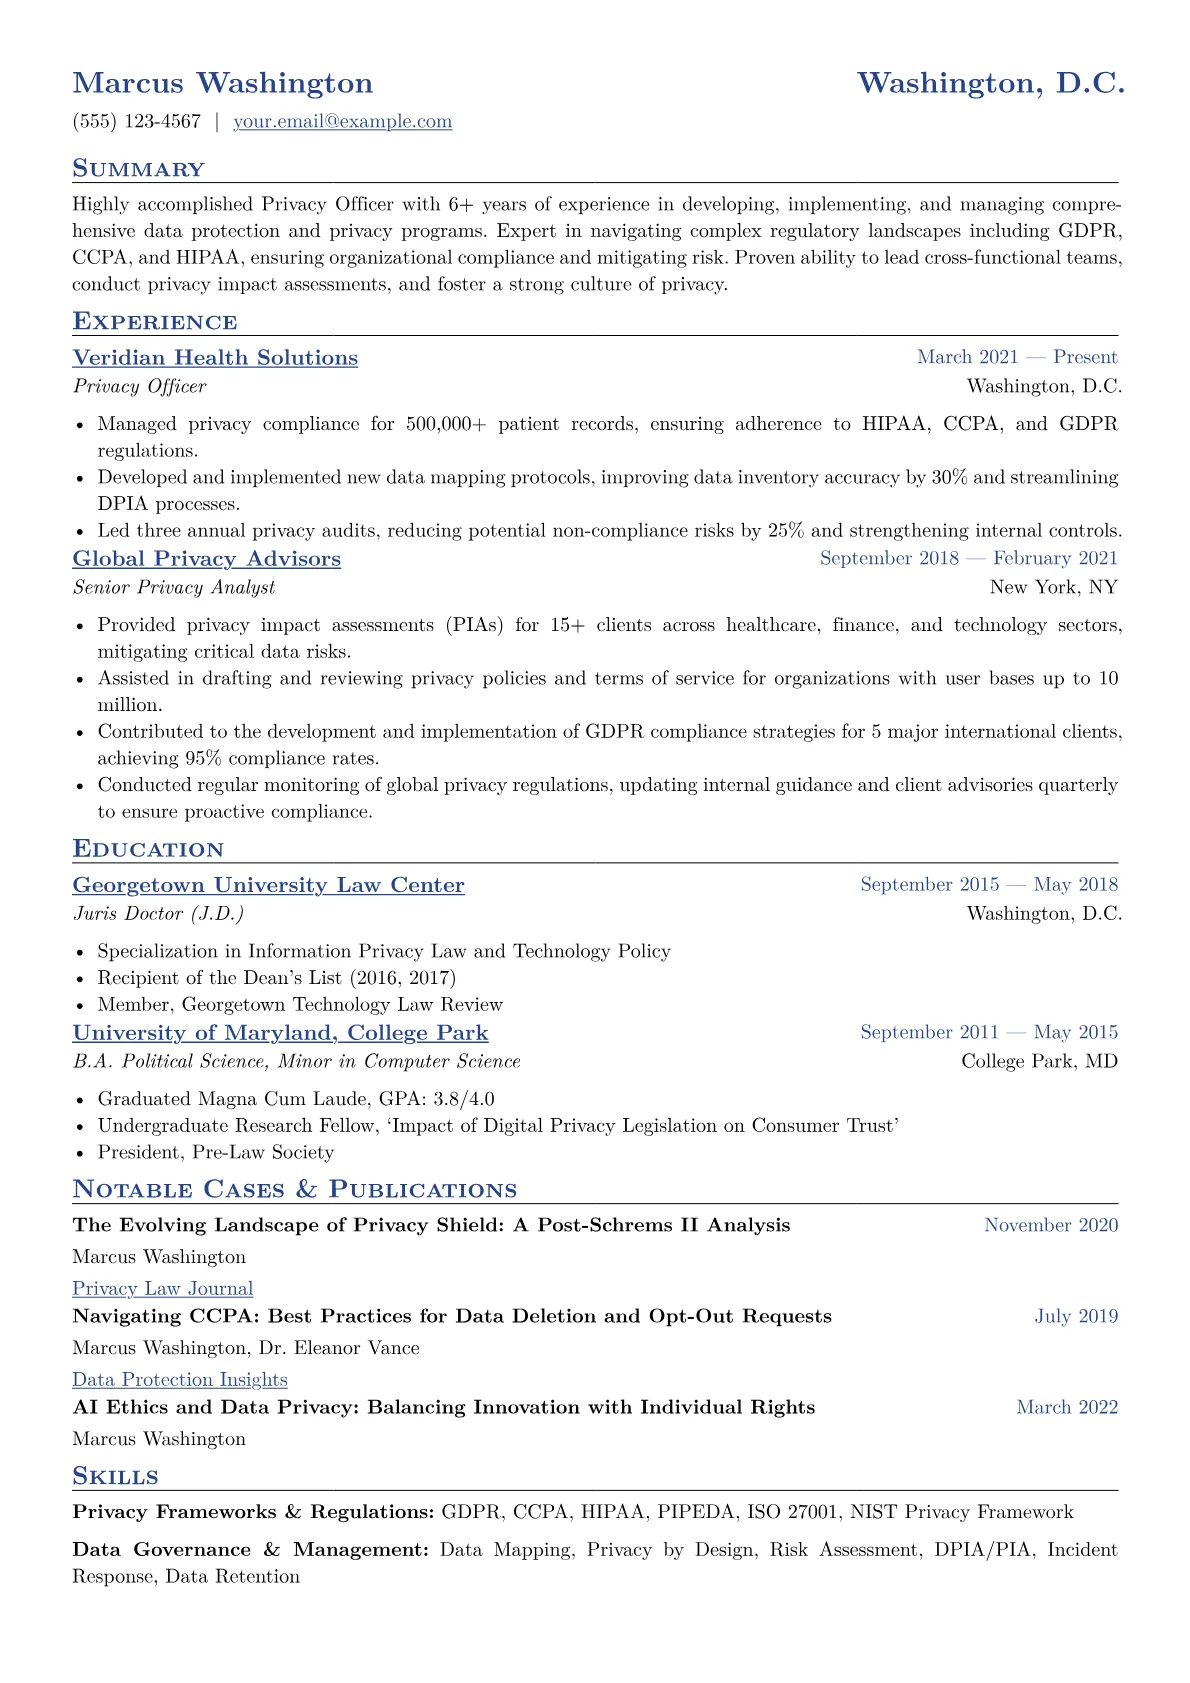
Marcus Washington · Privacy Officer
Summary
Highly accomplished Privacy Officer with 6+ years of experience in developing, implementing, and managing comprehensive data protection and privacy programs. Expert in navigating complex regulatory landscapes including GDPR, CCPA, and HIPAA, ensuring organizational compliance and mitigating risk. Proven ability to lead cross-functional teams, conduct privacy impact assessments, and foster a strong culture of privacy.
Experience
Privacy Officer · Veridian Health Solutions
Washington, D.C. · 2021 - Present
- Managed privacy compliance for 500,000+ patient records, ensuring adherence to HIPAA, CCPA, and GDPR regulations.
- Developed and implemented new data mapping protocols, improving data inventory accuracy by 30% and streamlining DPIA processes.
- Led three annual privacy audits, reducing potential non-compliance risks by 25% and strengthening internal controls.
- Trained over 2,000 employees annually on privacy best practices, resulting in a 15% decrease in reported privacy incidents.
- Collaborated with product and engineering teams to embed 'privacy by design' principles, reducing post-launch compliance issues by 20%.
Senior Privacy Analyst · Global Privacy Advisors
New York, NY · 2018 - 2021
- Provided privacy impact assessments (PIAs) for 15+ clients across healthcare, finance, and technology sectors, mitigating critical data risks.
- Assisted in drafting and reviewing privacy policies and terms of service for organizations with user bases up to 10 million.
- Contributed to the development and implementation of GDPR compliance strategies for 5 major international clients, achieving 95% compliance rates.
- Conducted regular monitoring of global privacy regulations, updating internal guidance and client advisories quarterly to ensure proactive compliance.
- Spearheaded a project to automate data subject access request (DSAR) workflows, reducing response times by 40%.
Education
Juris Doctor (J.D.) · Georgetown University Law Center
Washington, D.C. · 2015 - 2018
- Specialization in Information Privacy Law and Technology Policy
- Recipient of the Dean's List (2016, 2017)
- Member, Georgetown Technology Law Review
B.A. Political Science, Minor in Computer Science · University of Maryland, College Park
College Park, MD · 2011 - 2015
- Graduated Magna Cum Laude, GPA: 3.8/4.0
- Undergraduate Research Fellow, 'Impact of Digital Privacy Legislation on Consumer Trust'
- President, Pre-Law Society
Skills
Privacy Officer resume example: Privacy Officer - Tech
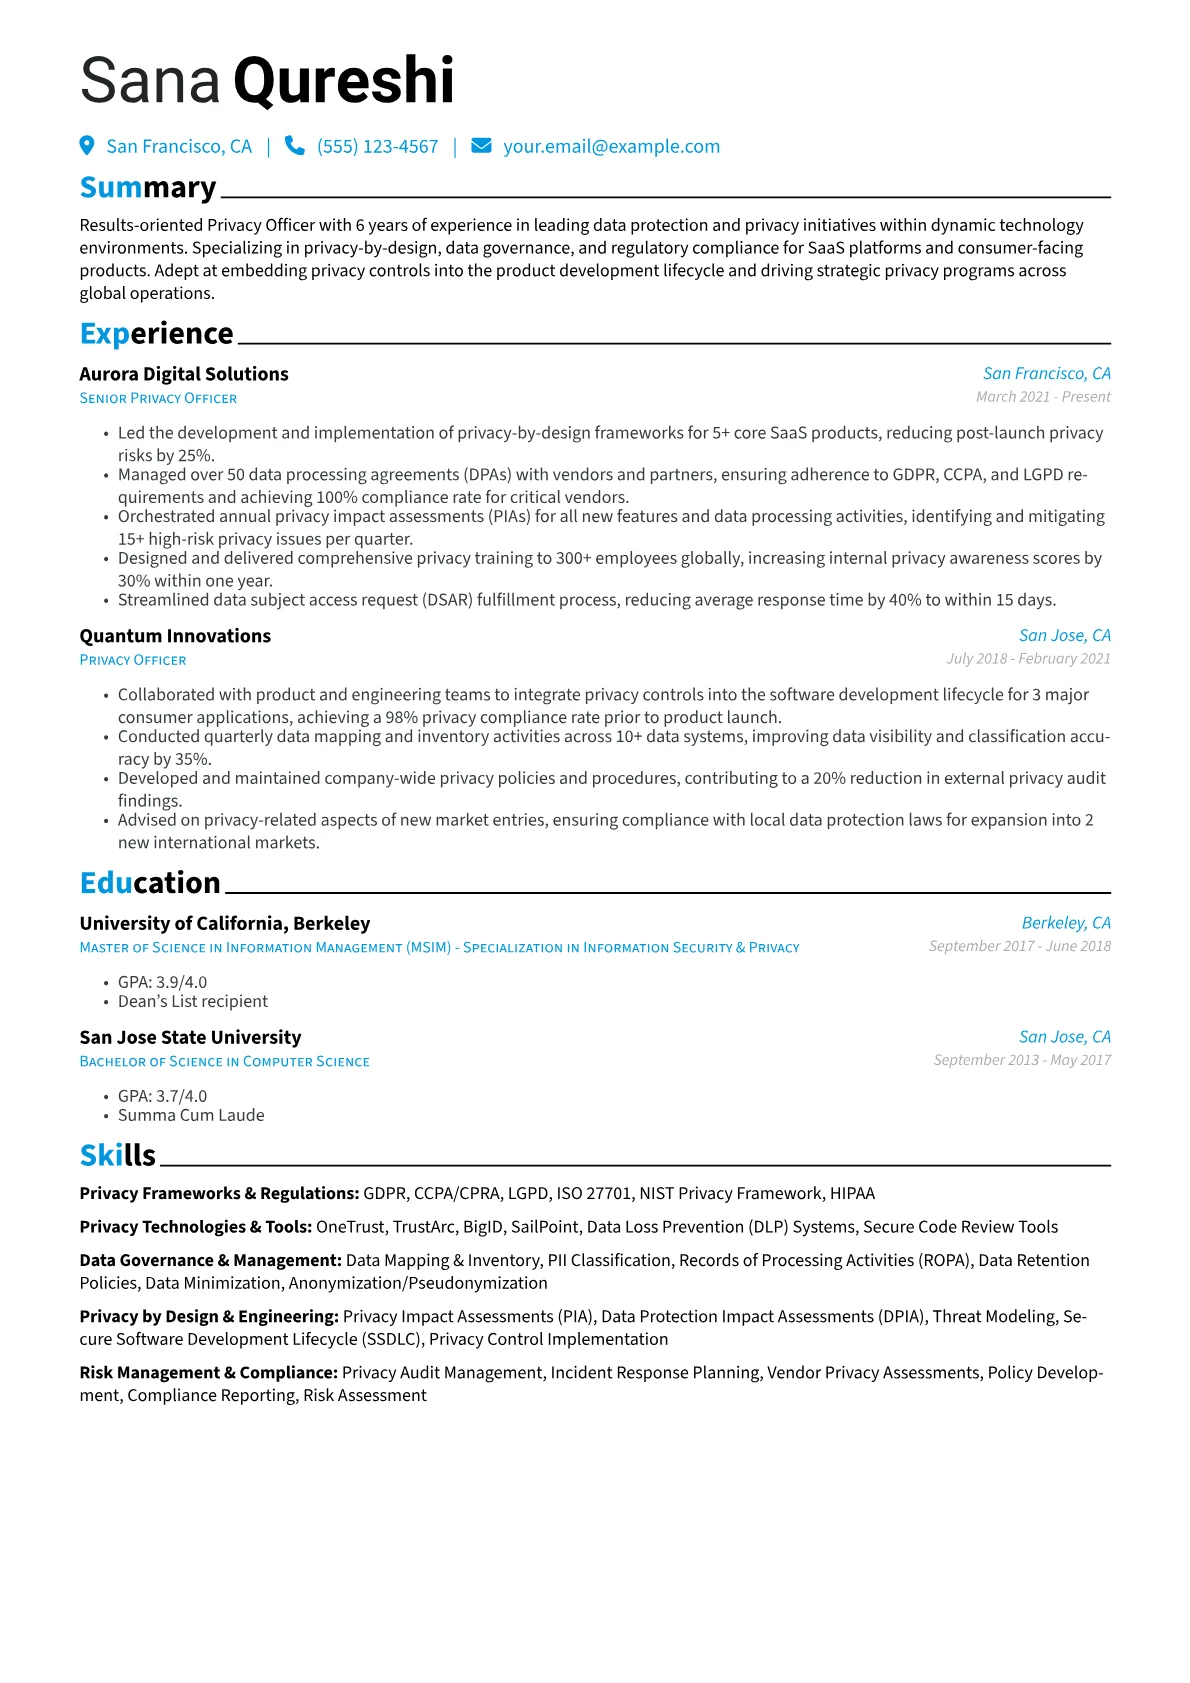
Sana Qureshi · Privacy Officer
Summary
Results-oriented Privacy Officer with 6 years of experience in leading data protection and privacy initiatives within dynamic technology environments. Specializing in privacy-by-design, data governance, and regulatory compliance for SaaS platforms and consumer-facing products. Adept at embedding privacy controls into the product development lifecycle and driving strategic privacy programs across global operations.
Experience
Senior Privacy Officer · Aurora Digital Solutions
San Francisco, CA · 2021 - Present
- Led the development and implementation of privacy-by-design frameworks for 5+ core SaaS products, reducing post-launch privacy risks by 25%.
- Managed over 50 data processing agreements (DPAs) with vendors and partners, ensuring adherence to GDPR, CCPA, and LGPD requirements and achieving 100% compliance rate for critical vendors.
- Orchestrated annual privacy impact assessments (PIAs) for all new features and data processing activities, identifying and mitigating 15+ high-risk privacy issues per quarter.
- Designed and delivered comprehensive privacy training to 300+ employees globally, increasing internal privacy awareness scores by 30% within one year.
- Streamlined data subject access request (DSAR) fulfillment process, reducing average response time by 40% to within 15 days.
Privacy Officer · Quantum Innovations
San Jose, CA · 2018 - 2021
- Collaborated with product and engineering teams to integrate privacy controls into the software development lifecycle for 3 major consumer applications, achieving a 98% privacy compliance rate prior to product launch.
- Conducted quarterly data mapping and inventory activities across 10+ data systems, improving data visibility and classification accuracy by 35%.
- Developed and maintained company-wide privacy policies and procedures, contributing to a 20% reduction in external privacy audit findings.
- Advised on privacy-related aspects of new market entries, ensuring compliance with local data protection laws for expansion into 2 new international markets.
Education
Master of Science in Information Management (MSIM) - Specialization in Information Security & Privacy · University of California, Berkeley
Berkeley, CA · 2017 - 2018
- GPA: 3.9/4.0
- Dean's List recipient
Bachelor of Science in Computer Science · San Jose State University
San Jose, CA · 2013 - 2017
- GPA: 3.7/4.0
- Summa Cum Laude
Skills
Privacy Officer resume example: Career Changer
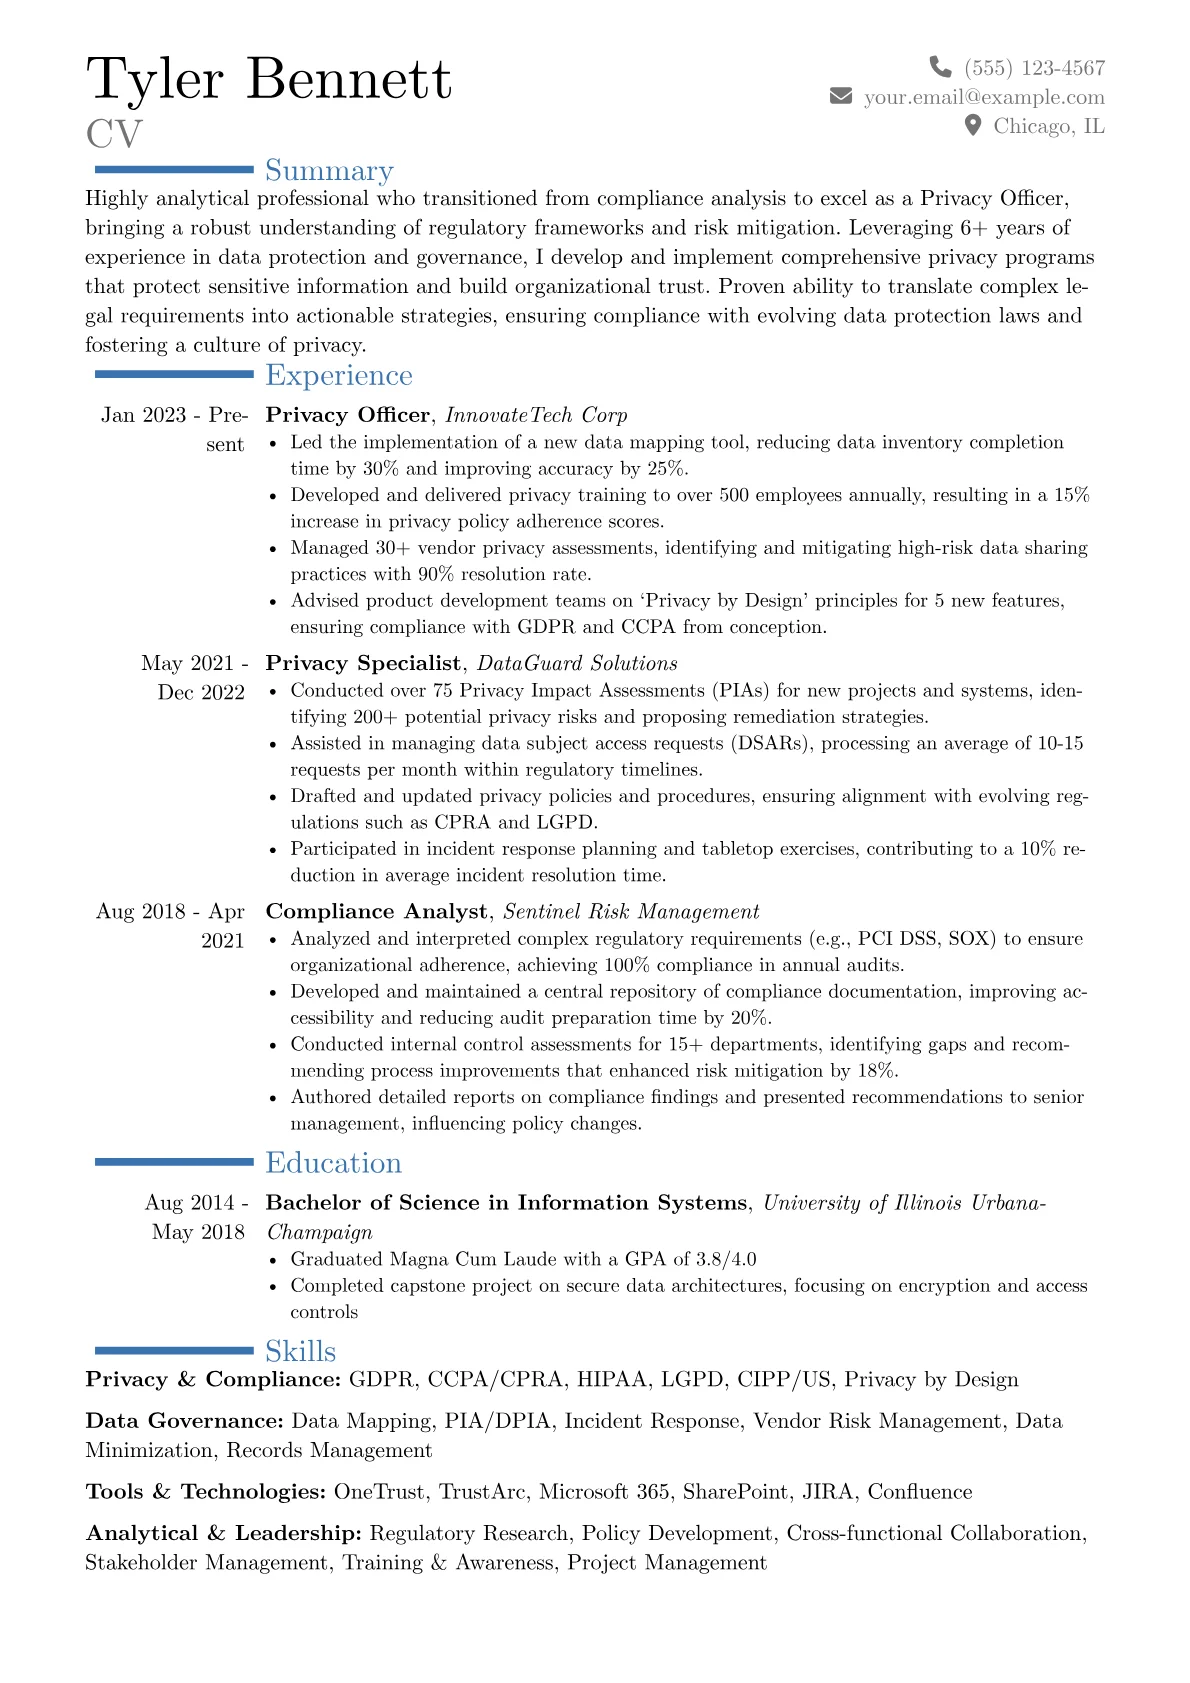
Tyler Bennett · Privacy Officer
Summary
Highly analytical professional who transitioned from compliance analysis to excel as a Privacy Officer, bringing a robust understanding of regulatory frameworks and risk mitigation. Leveraging 6+ years of experience in data protection and governance, I develop and implement comprehensive privacy programs that protect sensitive information and build organizational trust. Proven ability to translate complex legal requirements into actionable strategies, ensuring compliance with evolving data protection laws and fostering a culture of privacy.
Experience
Privacy Officer · InnovateTech Corp
Chicago, IL · 2023 - Present
- Led the implementation of a new data mapping tool, reducing data inventory completion time by 30% and improving accuracy by 25%.
- Developed and delivered privacy training to over 500 employees annually, resulting in a 15% increase in privacy policy adherence scores.
- Managed 30+ vendor privacy assessments, identifying and mitigating high-risk data sharing practices with 90% resolution rate.
- Advised product development teams on 'Privacy by Design' principles for 5 new features, ensuring compliance with GDPR and CCPA from conception.
Privacy Specialist · DataGuard Solutions
Chicago, IL · 2021 - 2022
- Conducted over 75 Privacy Impact Assessments (PIAs) for new projects and systems, identifying 200+ potential privacy risks and proposing remediation strategies.
- Assisted in managing data subject access requests (DSARs), processing an average of 10-15 requests per month within regulatory timelines.
- Drafted and updated privacy policies and procedures, ensuring alignment with evolving regulations such as CPRA and LGPD.
- Participated in incident response planning and tabletop exercises, contributing to a 10% reduction in average incident resolution time.
Compliance Analyst · Sentinel Risk Management
Chicago, IL · 2018 - 2021
- Analyzed and interpreted complex regulatory requirements (e.g., PCI DSS, SOX) to ensure organizational adherence, achieving 100% compliance in annual audits.
- Developed and maintained a central repository of compliance documentation, improving accessibility and reducing audit preparation time by 20%.
- Conducted internal control assessments for 15+ departments, identifying gaps and recommending process improvements that enhanced risk mitigation by 18%.
- Authored detailed reports on compliance findings and presented recommendations to senior management, influencing policy changes.
Education
Bachelor of Science in Information Systems · University of Illinois Urbana-Champaign
Urbana, IL · 2014 - 2018
- Graduated Magna Cum Laude with a GPA of 3.8/4.0
- Completed capstone project on secure data architectures, focusing on encryption and access controls
Skills
How useful was this template?
Example by JobSproutPrivacy Officer resume summary example
Highly accomplished Privacy Officer with 6+ years of experience in developing, implementing, and managing comprehensive data protection and privacy programs. Expert in navigating complex regulatory landscapes including GDPR, CCPA, and HIPAA, ensuring organizational compliance and mitigating risk. Proven ability to lead cross-functional teams, conduct privacy impact assessments, and foster a strong culture of privacy.
Privacy Officer salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $51,667 | $99,500 | $146,605 |
| UK | £25,500 | £35,000 | £58,333 |
| Canada | C$63,235 | C$82,727 | C$109,615 |
| Australia | A$101,122 | A$135,441 | A$149,148 |
| Germany | €54,375 | €58,750 | €71,250 |
| France | €56,250 | €67,500 | €92,944 |
| Netherlands | €62,500 | €70,233 | €71,512 |
| Italy | €30,000 | €50,000 | €55,000 |
| Austria | €63,763 | €67,525 | €71,288 |
| New Zealand | NZ$110,156 | NZ$123,438 | NZ$184,375 |
| India | ₹381,579 | ₹763,158 | ₹1,458,333 |
| Poland | zł172,500 | zł211,886 | zł249,086 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
Privacy Officer resume skills and keywords
Recruiters and applicant tracking systems scan Privacy Officer resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
Privacy Officer
Salary Range
Salary Trend
12-Month Trend
Based on advertised Legal roles.
US market data · Source: Adzuna · Updated Mar 2026
Frequently Asked Questions
What's the best resume structure for a mid-level Privacy Officer?
What key skills and qualifications should I highlight as a Privacy Officer?
How can I write strong achievement bullets or a professional summary for a Privacy Officer?
Which optional sections matter most for a Privacy Officer's resume?
How do I tailor this template for a specific Privacy Officer job posting?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Career moves from Privacy Officer
Usually need more experience or training
Usually need less experience or training
Includes information from the O*NET 30.3 Database by the U.S. Department of Labor, Employment and Training Administration (USDOL/ETA), used under the CC BY 4.0 license. We have modified it; USDOL/ETA has not approved, endorsed or tested these modifications. O*NET is a trademark of USDOL/ETA.