VP of Security Resume Examples
 Example by JobSprout
Free to use. No download fee.
Use the Modern template
Your resume in this design, ready to edit.
Free, and no account needed to start.
Market Insights
VP of Security
Salary Range
Salary Trend
Mar 2025 – Feb 2026
12-Month Trend
Based on advertised Software Engineering roles.
US market data · Source: Adzuna · Updated Mar 2026
How useful was this template?
VP of Security resume samples
Three complete resumes, each in a different design.



Free to use. No download fee.
What makes a strong VP of Security resume?
US median salary $103,333 ·
For a Vice President of Security in Technology, a resume must transcend mere technical listings to showcase strategic leadership and quantifiable impact. Hiring managers seek executives who can articulate how they’ve built resilient security postures, managed enterprise risk effectively, and ensured compliance with frameworks like NIST CSF or ISO 27001. Concrete achievements should detail leading secure SDLC initiatives, defending against advanced persistent threats, or securing extensive cloud infrastructure (AWS, Azure, GCP). Emphasizing a deep understanding of threat intelligence, incident response, and the direct business value derived from security investments is paramount, with certifications like CISSP or CISM bolstering credibility.
Why this example works
The provided JobSprout example effectively illustrates these executive-level expectations. Its structural choices clearly delineate leadership contributions, with achievements consistently quantified to demonstrate tangible results, such as “reduced critical vulnerabilities by 35% across product lines.” The skills section is intelligently categorized, separating high-level strategic capabilities like “Enterprise Risk Management” from specific technical proficiencies in SIEM or EDR platforms. Certifications and key security tools are prominently featured, allowing for quick assessment of the candidate's operational and strategic toolkit.
VP of Security resume example (text version)
Zara Ibrahim · VP of Security
Summary
Accomplished VP of Security with over 18 years of progressive experience leading global cybersecurity programs and teams in fast-paced technology environments. Proven expertise in developing and implementing comprehensive security strategies, risk management frameworks, and incident response protocols. Adept at building strong, security-conscious cultures and driving significant improvements in organizational security posture while fostering collaboration across engineering and product teams. Seeking to leverage deep technical acumen and strategic leadership to protect critical assets and enable business growth.
Experience
VP of Security · Apex Innovations
San Francisco, CA · 2018 - Present
- Orchestrated a 35% reduction in critical security vulnerabilities year-over-year by implementing a new DevSecOps pipeline and automated scanning tools.
- Developed and managed a $10M annual security budget, optimizing resource allocation to achieve 99.9% uptime for critical security infrastructure.
- Led a team of 30+ security professionals, increasing team efficiency by 20% through targeted training and process improvements.
- Successfully achieved ISO 27001 and SOC 2 Type II compliance within 18 months, enhancing customer trust and securing $50M in new enterprise contracts.
- Reduced average incident response time by 40% through the implementation of playbooks and a centralized SIEM platform.
Director of Security Engineering · Quantum Labs
San Jose, CA · 2013 - 2018
- Built and scaled the security engineering team from 5 to 15 engineers, supporting a 300% increase in product offerings.
- Designed and deployed a new security architecture that prevented over 500 potential cyberattacks annually, significantly reducing breach risk.
- Automated 70% of routine security tasks, freeing up engineers to focus on strategic initiatives and advanced threat analysis.
- Managed vendor relationships for security tools, negotiating contracts that saved the company 15% on annual licensing costs.
- Spearheaded the migration of on-premise security systems to AWS, improving scalability and reducing operational costs by 25%.
Senior Security Engineer · Innovatech Solutions
Seattle, WA · 2008 - 2013
- Developed and maintained intrusion detection systems, decreasing false positives by 10% and improving threat detection accuracy.
- Performed regular penetration testing and vulnerability assessments, identifying and remediating over 200 critical security flaws.
- Contributed to the development of secure coding guidelines, reducing application-layer vulnerabilities by 30% across product lines.
- Provided technical mentorship to junior security analysts, improving team's skill competency by 25% within one year.
Education
M.S. in Cybersecurity · Carnegie Mellon University
Pittsburgh, PA · 2005 - 2007
- Thesis on AI-driven threat detection systems
- Awarded Dean's Fellowship for academic excellence
B.S. in Computer Science · University of California, Berkeley
Berkeley, CA · 1999 - 2003
- Graduated Magna Cum Laude with a 3.8 GPA
- Developed secure network protocols for senior project
Skills
VP of Security resume example: Alternate Version
James Rodriguez · VP of Security
Summary
Accomplished Vice President of Security with over 16 years of progressive experience leading robust cybersecurity programs within highly regulated financial services environments. Expert in developing and executing comprehensive security strategies, fostering strong governance, risk, and compliance frameworks, and ensuring resilient business operations. Proven track record of safeguarding critical assets, driving secure digital transformation, and building high-performing global security teams.
Experience
VP, Enterprise Security & Compliance · Fortress Financial Group
New York, NY · 2018 - Present
- Led a team of 30+ security professionals across GRC, Security Engineering, and Operations, reducing critical audit findings by 45% in 2 years.
- Orchestrated the implementation of an integrated GRC platform, automating 70% of compliance reporting and reducing manual effort by over 1,500 hours annually.
- Developed and enforced a Zero Trust security architecture roadmap, reducing the attack surface by 30% for critical financial applications.
- Managed a $15M annual cybersecurity budget, achieving 98% on-budget project delivery while enhancing security posture.
- Spearheaded regulatory compliance efforts for Dodd-Frank, SOX, and NYDFS Cybersecurity Regulation (23 NYCRR 500), achieving 100% adherence in annual assessments.
Director of Information Security · Ascendant Payments
Boston, MA · 2012 - 2018
- Built and led a security team of 12, overseeing security operations, incident response, and vulnerability management for a rapidly growing FinTech platform.
- Achieved PCI DSS Level 1 certification within 18 months, enabling expansion into new payment processing markets and increasing revenue by 20%.
- Implemented a new SIEM solution (Splunk ES) that reduced average threat detection time by 60% and false positives by 40%.
- Developed and managed a comprehensive vendor risk management program, assessing over 100 third-party vendors annually and mitigating 25+ high-risk vulnerabilities.
- Designed and executed a company-wide security awareness training program, increasing employee phishing reporting rates by 75%.
Lead Security Architect · GlobalBank Securities
London, UK · 2007 - 2012
- Designed and implemented secure architecture for high-value trading platforms, improving system resilience and reducing downtime by 15%.
- Conducted comprehensive security assessments and penetration tests, identifying and remediating 50+ critical vulnerabilities across global infrastructure.
- Developed security standards and guidelines for application development teams, resulting in a 20% reduction in security defects in production code.
- Provided architectural guidance for data encryption and data loss prevention (DLP) initiatives, protecting sensitive customer and financial data.
- Authored technical specifications for secure network segmentation projects, isolating critical systems and reducing lateral movement risk by 35%.
Education
Master of Science in Cybersecurity · New York University
New York, NY · 2008 - 2010
- Specialized in Enterprise Security Architecture and Risk Management.
- Graduated with a GPA of 3.9/4.0.
Bachelor of Science in Computer Science · Carnegie Mellon University
Pittsburgh, PA · 2003 - 2007
- Focus on network security and distributed systems.
- Graduated Magna Cum Laude with a GPA of 3.7/4.0.
Skills
VP of Security resume example: Career Changer
Ethan Park · VP of Security
Summary
Leveraging a robust foundation in complex system architecture and over 16 years of progressive experience, Ethan Park is a proven VP of Security dedicated to building resilient and proactive security programs. Expertly translates business objectives into comprehensive cybersecurity strategies, fostering innovation while rigorously mitigating risk across enterprise environments. A strategic leader known for empowering high-performing teams, enhancing organizational security posture, and navigating evolving threat landscapes with precision and foresight.
Experience
VP of Security · Horizon Cybernetics
Austin, TX · 2023 - Present
- Orchestrated the implementation of a zero trust architecture across 50+ enterprise applications, reducing potential breach impact by an estimated 40%.
- Developed and executed a comprehensive cloud security strategy for AWS and Azure environments, improving security posture by 35% as measured by cloud security benchmarks.
- Led a team of 15 security professionals, improving incident response times by 25% through advanced automation and training programs.
- Established a new GRC framework, achieving SOC 2 Type II compliance 3 months ahead of schedule and reducing audit findings by 60% year over year.
VP, Head of Cybersecurity · Aegis Global
Austin, TX · 2019 - 2023
- Directed global cybersecurity strategy for a 10,000+ employee organization, reducing critical security incidents by 30% over three years.
- Managed an annual security budget of $5M, optimizing spend by 15% through strategic vendor consolidation and open source tool adoption.
- Presented quarterly security posture and risk reports to the Board of Directors, influencing a 20% increase in security investment for strategic initiatives.
- Successfully guided the company through GDPR and CCPA compliance audits with zero major findings, protecting customer data for over 50 million users.
Director of Security Architecture · Veridian Data Security
Austin, TX · 2015 - 2019
- Built and led a team of 8 security architects, defining security standards and best practices for product development and infrastructure.
- Designed and implemented secure software development lifecycle (SSDLC) processes, reducing security vulnerabilities in new code releases by 50%.
- Developed the company's first formal cloud security strategy, enabling secure migration of 70% of on-premise applications to AWS and Azure.
- Introduced advanced threat modeling techniques, identifying and mitigating 15+ high-risk design flaws before production deployment.
Principal Systems Architect · OmniTech Solutions
Dallas, TX · 2008 - 2015
- Led architecture and design for high-performance distributed systems supporting 10M+ daily transactions, ensuring 99.99% uptime.
- Integrated security-by-design principles into core system architecture, reducing post-release security patches by 25%.
- Mentored junior architects and engineers, fostering a culture of technical excellence and secure coding practices across a team of 50+.
- Optimized system performance, decreasing latency by 15% and reducing infrastructure costs by $1.2M annually through efficient resource utilization.
Education
Master of Science in Computer Science · University of Texas at Austin
Austin, TX · 2008 - 2010
- GPA: 3.9/4.0
- Thesis: 'Secure Microservice Architectures and Their Vulnerabilities'
Bachelor of Science in Computer Engineering · Texas A&M University
College Station, TX · 2004 - 2008
- Magna Cum Laude
- Senior Design Project: Automated Network Intrusion Detection System
Skills
How useful was this template?
Example by JobSprout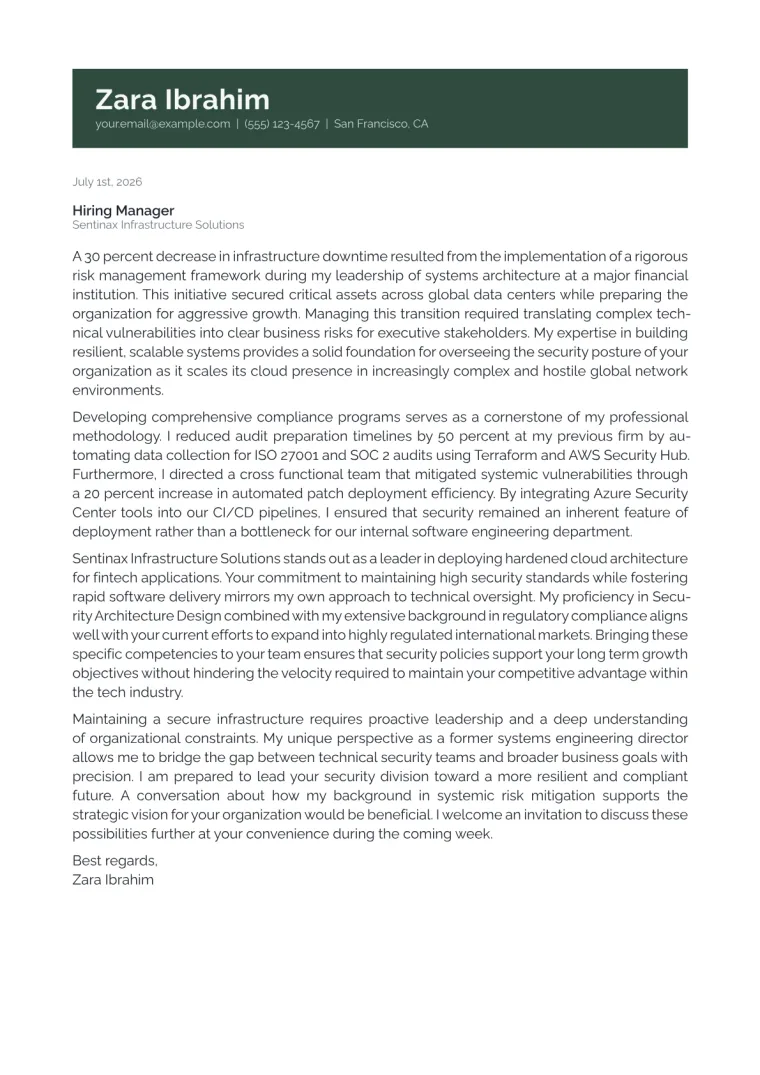
VP of Security cover letter for a career changer
Written for the same situation as this resume.
VP of Security resume summary example
Accomplished VP of Security with over 18 years of progressive experience leading global cybersecurity programs and teams in fast-paced technology environments. Proven expertise in developing and implementing comprehensive security strategies, risk management frameworks, and incident response protocols. Adept at building strong, security-conscious cultures and driving significant improvements in organizational security posture while fostering collaboration across engineering and product teams. Seeking to leverage deep technical acumen and strategic leadership to protect critical assets and enable business growth.
VP of Security salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $57,682 | $103,333 | $146,138 |
| UK | £60,000 | £70,000 | £83,663 |
| Canada | C$85,000 | C$121,667 | C$140,833 |
| Australia | A$120,000 | A$150,864 | A$167,160 |
| Germany | €52,727 | €64,167 | €76,316 |
| France | €47,500 | €57,500 | €65,833 |
| Netherlands | €56,786 | €65,000 | €72,813 |
| New Zealand | NZ$75,000 | NZ$100,000 | NZ$125,000 |
| India | ₹4,125,000 | ₹4,250,000 | ₹4,375,000 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
VP of Security resume skills and keywords
Recruiters and applicant tracking systems scan VP of Security resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
VP of Security
Salary Range
Salary Trend
Mar 2025 – Feb 2026
12-Month Trend
Based on advertised Software Engineering roles.
US market data · Source: Adzuna · Updated Mar 2026
Frequently Asked Questions
What's the best resume structure for a Security executive with over 15 years of experience?
What key skills and qualifications should a Security executive highlight?
How can I write strong achievement bullets and an executive summary for Security roles?
Which optional sections are important for a Security executive's resume, like certifications?
How do I tailor my Security executive resume for different job opportunities?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Related Articles

How to Write a CV for Tech Applications [2026 Guide]
Learn how to write a software engineering CV that gets interviews. Real template analysis, what hiring managers look for, and common mistakes to avoid.

How to Write a CV That Shows Startup Experience [2026 Guide]
Learn how to write a CV that showcases founding engineer and startup experience. Real example from JobSprout's creator, what hiring managers look for, and how to position breadth as a strength.