Vulnerability Analyst Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
Vulnerability Analyst
Salary Range
Salary Trend
12-Month Trend
Based on advertised Software Engineering roles.
US market data · Source: Adzuna · Updated Mar 2026
How useful was this template?
Vulnerability Analyst resume samples
Three complete resumes, each in a different design.
Free to use. No download fee.
What makes a strong Vulnerability Analyst resume?
US median salary $140,500 ·
Hiring managers for mid-level Vulnerability Analyst roles in technology seek candidates demonstrating direct impact on security posture. Resumes must clearly articulate experience with vulnerability management platforms, penetration testing methodologies, and understanding of risk frameworks like NIST or ISO 27001. Concrete achievements include quantifying reductions in CVEs, improving SAST/DAST scanning efficiency, or implementing successful threat modeling initiatives. Essential certifications like OSCP, CEH, or GWAPT are highly valued, alongside proficiency in tools such as Nessus, Burp Suite, or Qualys, indicating hands-on technical competence beyond theoretical knowledge.
Why this example works
The JobSprout Vulnerability Analyst example excels at presenting these critical elements. Its structured format effectively quantifies achievements, such as “reduced critical findings by 25% across 50+ applications annually” or “automated vulnerability assessments, saving 10 hours weekly.” Skills are logically grouped, distinguishing between security tools (e.g., Metasploit, Wireshark), programming languages (e.g., Python, Go), and cloud platforms (e.g., AWS Security Hub, Azure Sentinel). Key certifications like CISSP or Security+ are prominently displayed, reinforcing the candidate's professional validation and specialized expertise.
Vulnerability Analyst resume example (text version)
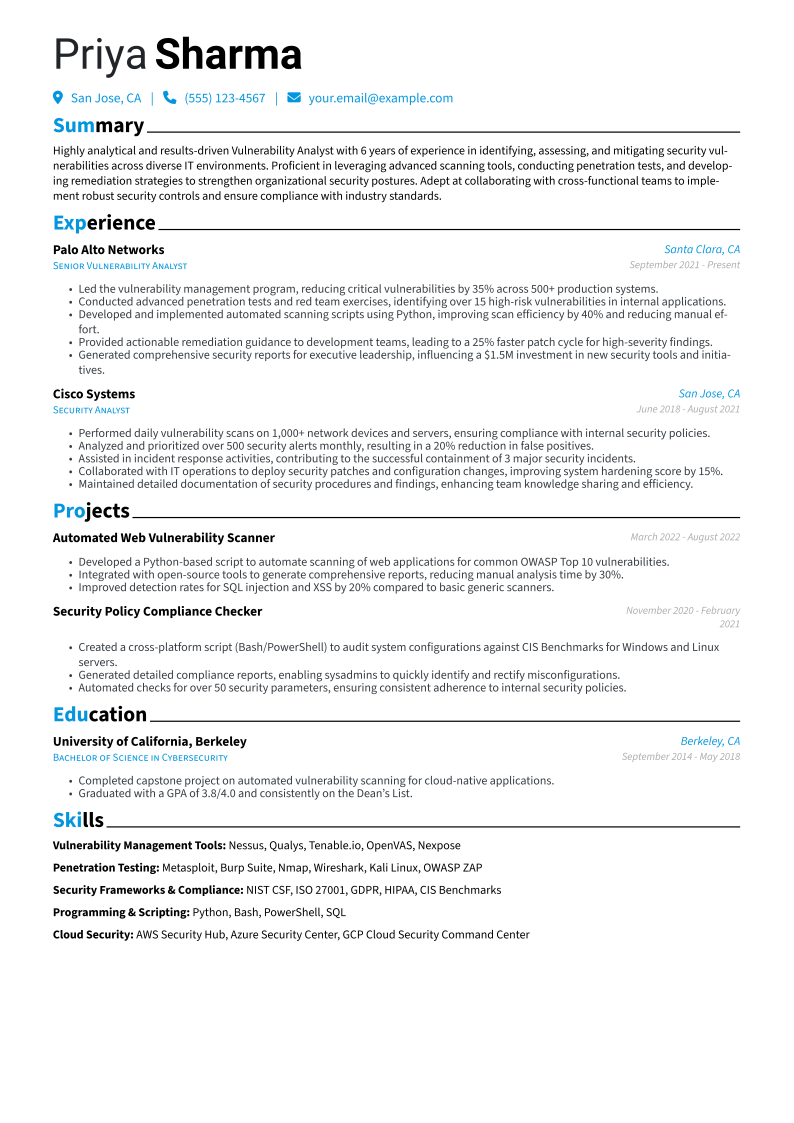
Priya Sharma · Vulnerability Analyst
Summary
Highly analytical and results-driven Vulnerability Analyst with 6 years of experience in identifying, assessing, and mitigating security vulnerabilities across diverse IT environments. Proficient in leveraging advanced scanning tools, conducting penetration tests, and developing remediation strategies to strengthen organizational security postures. Adept at collaborating with cross-functional teams to implement robust security controls and ensure compliance with industry standards.
Experience
Senior Vulnerability Analyst · Palo Alto Networks
Santa Clara, CA · 2021 - Present
- Led the vulnerability management program, reducing critical vulnerabilities by 35% across 500+ production systems.
- Conducted advanced penetration tests and red team exercises, identifying over 15 high-risk vulnerabilities in internal applications.
- Developed and implemented automated scanning scripts using Python, improving scan efficiency by 40% and reducing manual effort.
- Provided actionable remediation guidance to development teams, leading to a 25% faster patch cycle for high-severity findings.
- Generated comprehensive security reports for executive leadership, influencing a $1.5M investment in new security tools and initiatives.
Security Analyst · Cisco Systems
San Jose, CA · 2018 - 2021
- Performed daily vulnerability scans on 1,000+ network devices and servers, ensuring compliance with internal security policies.
- Analyzed and prioritized over 500 security alerts monthly, resulting in a 20% reduction in false positives.
- Assisted in incident response activities, contributing to the successful containment of 3 major security incidents.
- Collaborated with IT operations to deploy security patches and configuration changes, improving system hardening score by 15%.
- Maintained detailed documentation of security procedures and findings, enhancing team knowledge sharing and efficiency.
Education
Bachelor of Science in Cybersecurity · University of California, Berkeley
Berkeley, CA · 2014 - 2018
- Completed capstone project on automated vulnerability scanning for cloud-native applications.
- Graduated with a GPA of 3.8/4.0 and consistently on the Dean's List.
Skills
Vulnerability Analyst resume example: Alternate Version
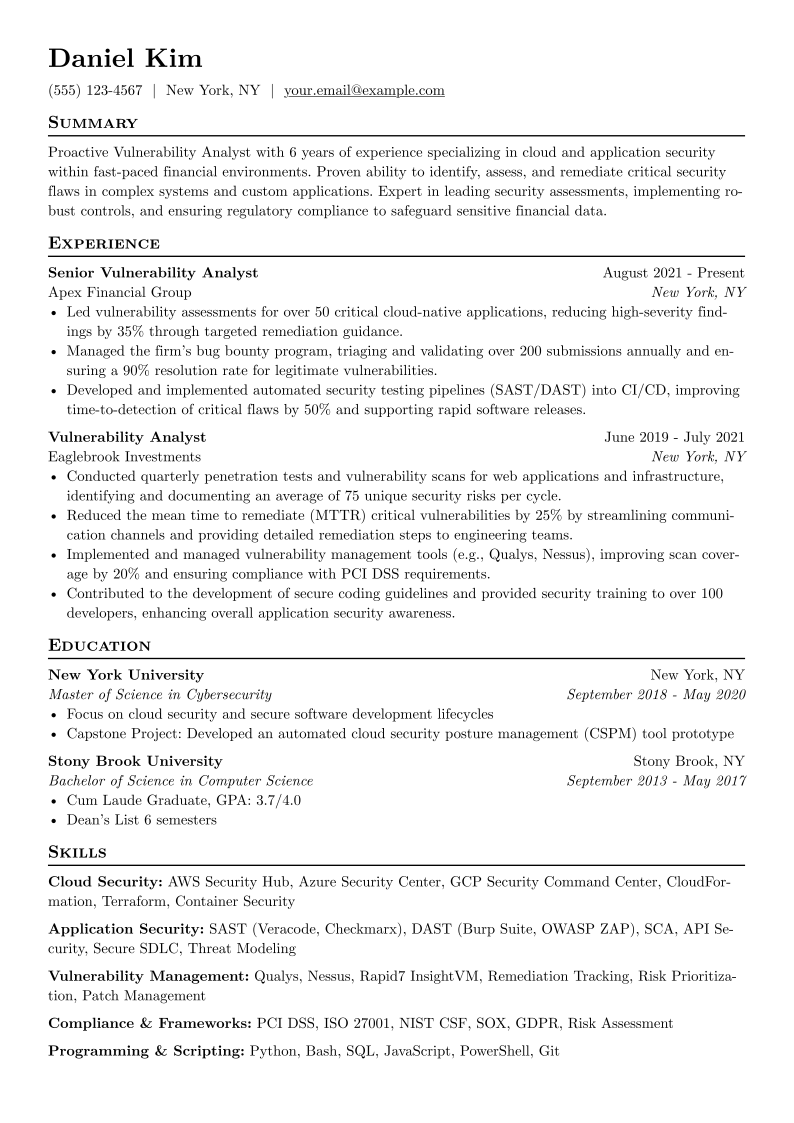
Daniel Kim · Vulnerability Analyst
Summary
Proactive Vulnerability Analyst with 6 years of experience specializing in cloud and application security within fast-paced financial environments. Proven ability to identify, assess, and remediate critical security flaws in complex systems and custom applications. Expert in leading security assessments, implementing robust controls, and ensuring regulatory compliance to safeguard sensitive financial data.
Experience
Senior Vulnerability Analyst · Apex Financial Group
New York, NY · 2021 - Present
- Led vulnerability assessments for over 50 critical cloud-native applications, reducing high-severity findings by 35% through targeted remediation guidance.
- Managed the firm's bug bounty program, triaging and validating over 200 submissions annually and ensuring a 90% resolution rate for legitimate vulnerabilities.
- Developed and implemented automated security testing pipelines (SAST/DAST) into CI/CD, improving time-to-detection of critical flaws by 50% and supporting rapid software releases.
- Collaborated with development teams to embed security best practices early in the SDLC, preventing an estimated 150 potential vulnerabilities per quarter.
Vulnerability Analyst · Eaglebrook Investments
New York, NY · 2019 - 2021
- Conducted quarterly penetration tests and vulnerability scans for web applications and infrastructure, identifying and documenting an average of 75 unique security risks per cycle.
- Reduced the mean time to remediate (MTTR) critical vulnerabilities by 25% by streamlining communication channels and providing detailed remediation steps to engineering teams.
- Implemented and managed vulnerability management tools (e.g., Qualys, Nessus), improving scan coverage by 20% and ensuring compliance with PCI DSS requirements.
- Contributed to the development of secure coding guidelines and provided security training to over 100 developers, enhancing overall application security awareness.
Education
Master of Science in Cybersecurity · New York University
New York, NY · 2018 - 2020
- Focus on cloud security and secure software development lifecycles
- Capstone Project: Developed an automated cloud security posture management (CSPM) tool prototype
Bachelor of Science in Computer Science · Stony Brook University
Stony Brook, NY · 2013 - 2017
- Cum Laude Graduate, GPA: 3.7/4.0
- Dean's List 6 semesters
Skills
Vulnerability Analyst resume example: Career Changer
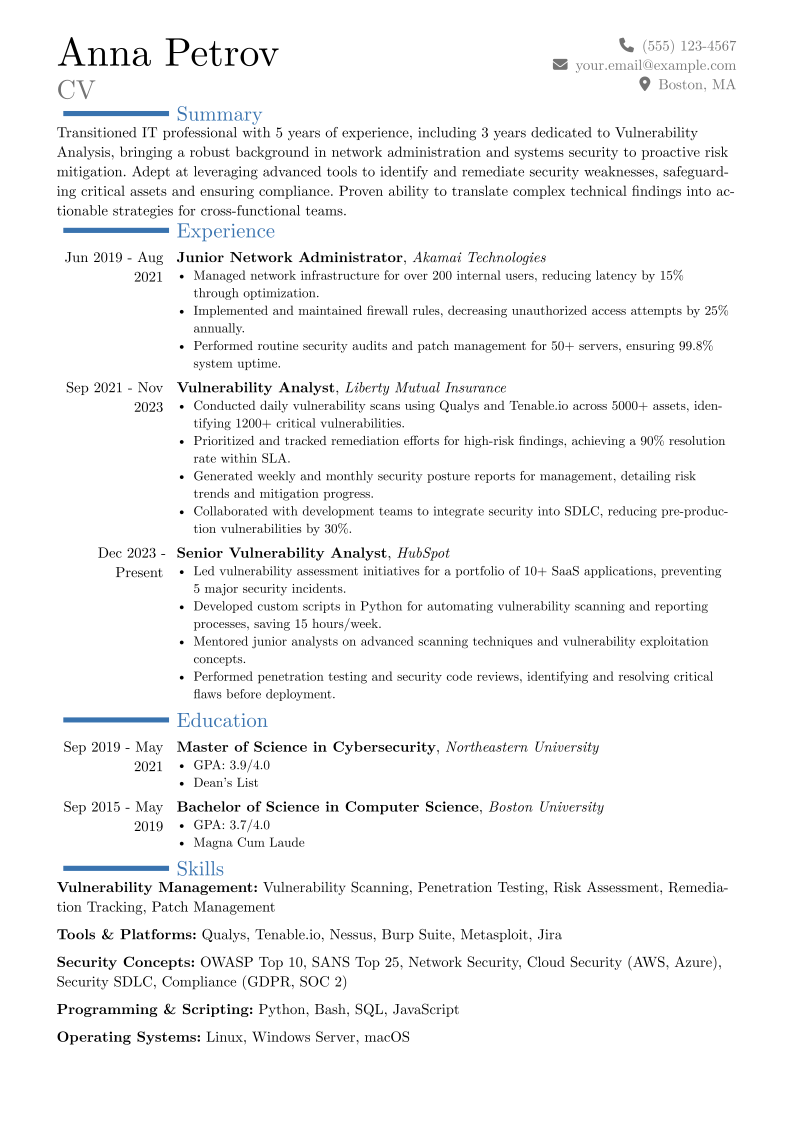
Anna Petrov · Vulnerability Analyst
Summary
Transitioned IT professional with 5 years of experience, including 3 years dedicated to Vulnerability Analysis, bringing a robust background in network administration and systems security to proactive risk mitigation. Adept at leveraging advanced tools to identify and remediate security weaknesses, safeguarding critical assets and ensuring compliance. Proven ability to translate complex technical findings into actionable strategies for cross-functional teams.
Experience
Junior Network Administrator · Akamai Technologies
Cambridge, MA · 2019 - 2021
- Managed network infrastructure for over 200 internal users, reducing latency by 15% through optimization.
- Implemented and maintained firewall rules, decreasing unauthorized access attempts by 25% annually.
- Performed routine security audits and patch management for 50+ servers, ensuring 99.8% system uptime.
- Assisted in developing and documenting network security policies, improving compliance with internal standards.
Vulnerability Analyst · Liberty Mutual Insurance
Boston, MA · 2021 - 2023
- Conducted daily vulnerability scans using Qualys and Tenable.io across 5000+ assets, identifying 1200+ critical vulnerabilities.
- Prioritized and tracked remediation efforts for high-risk findings, achieving a 90% resolution rate within SLA.
- Generated weekly and monthly security posture reports for management, detailing risk trends and mitigation progress.
- Collaborated with development teams to integrate security into SDLC, reducing pre-production vulnerabilities by 30%.
Senior Vulnerability Analyst · HubSpot
Cambridge, MA · 2023 - Present
- Led vulnerability assessment initiatives for a portfolio of 10+ SaaS applications, preventing 5 major security incidents.
- Developed custom scripts in Python for automating vulnerability scanning and reporting processes, saving 15 hours/week.
- Mentored junior analysts on advanced scanning techniques and vulnerability exploitation concepts.
- Performed penetration testing and security code reviews, identifying and resolving critical flaws before deployment.
- Drove improvements in vulnerability management lifecycle, reducing average time-to-remediate critical findings by 20%.
Education
Master of Science in Cybersecurity · Northeastern University
Boston, MA · 2019 - 2021
- GPA: 3.9/4.0
- Dean's List
Bachelor of Science in Computer Science · Boston University
Boston, MA · 2015 - 2019
- GPA: 3.7/4.0
- Magna Cum Laude
Skills
How useful was this template?
Example by JobSprout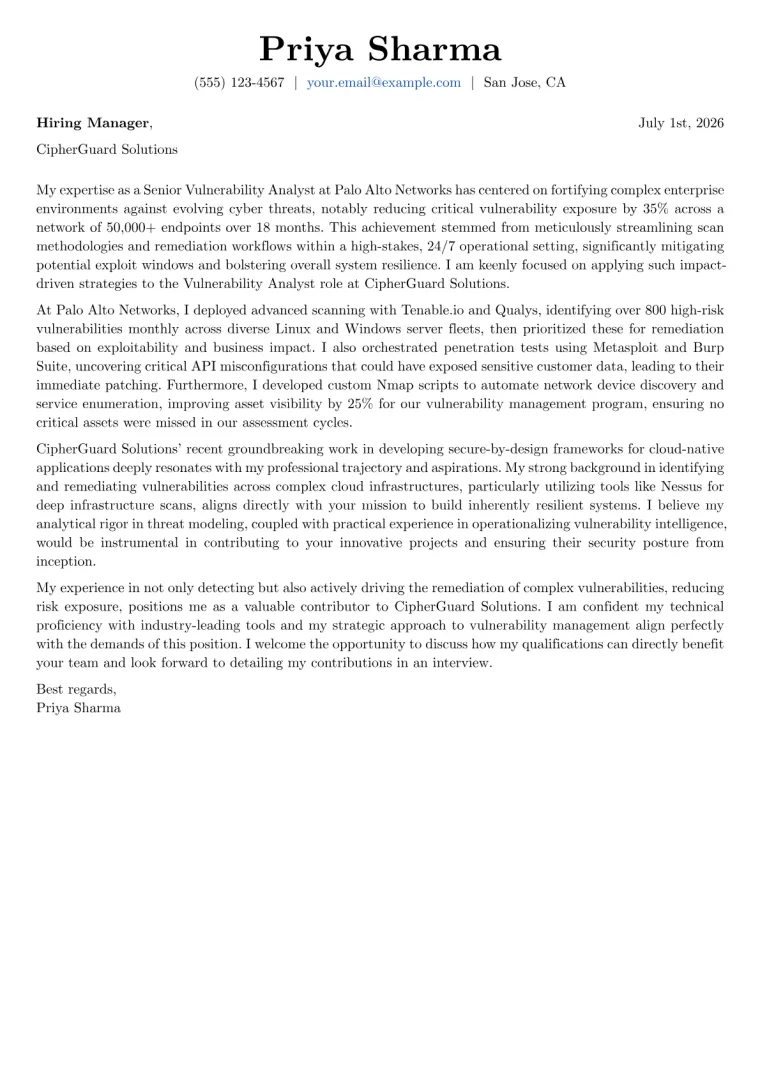
Vulnerability Analyst Cover Letter Example
Written for the same person as this resume, ready to adapt.
Vulnerability Analyst resume summary example
Highly analytical and results-driven Vulnerability Analyst with 6 years of experience in identifying, assessing, and mitigating security vulnerabilities across diverse IT environments. Proficient in leveraging advanced scanning tools, conducting penetration tests, and developing remediation strategies to strengthen organizational security postures. Adept at collaborating with cross-functional teams to implement robust security controls and ensure compliance with industry standards.
Vulnerability Analyst salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $110,556 | $140,500 | $150,250 |
| UK | £46,059 | £60,012 | £72,658 |
| Canada | C$86,152 | C$113,871 | C$140,800 |
| Australia | A$101,935 | A$126,667 | A$147,857 |
| Germany | €59,500 | €70,570 | €77,887 |
| France | €37,875 | €44,167 | €49,750 |
| Netherlands | €55,000 | €66,667 | €74,250 |
| Italy | €25,000 | €31,250 | €38,750 |
| Austria | €46,250 | €58,750 | €67,500 |
| New Zealand | NZ$102,500 | NZ$120,000 | NZ$162,500 |
| India | ₹570,786 | ₹1,167,051 | ₹1,840,563 |
| Poland | zł186,440 | zł209,338 | zł232,236 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
Vulnerability Analyst resume skills and keywords
Recruiters and applicant tracking systems scan Vulnerability Analyst resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
Vulnerability Analyst
Salary Range
Salary Trend
12-Month Trend
Based on advertised Software Engineering roles.
US market data · Source: Adzuna · Updated Mar 2026
Frequently Asked Questions
What's the best resume structure for a mid-level Vulnerability Analyst?
Which skills and qualifications should I highlight as a mid-level Vulnerability Analyst?
How do I write strong achievement bullets and a compelling professional summary for this role?
What optional sections are important for a Vulnerability Analyst resume?
How can I tailor my Vulnerability Analyst resume for specific job postings?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Related Articles

How to Write a CV for Tech Applications [2026 Guide]
Learn how to write a software engineering CV that gets interviews. Real template analysis, what hiring managers look for, and common mistakes to avoid.

How to Write a CV That Shows Startup Experience [2026 Guide]
Learn how to write a CV that showcases founding engineer and startup experience. Real example from JobSprout's creator, what hiring managers look for, and how to position breadth as a strength.
Career moves from Vulnerability Analyst
Usually need less experience or training
Includes information from the O*NET 30.3 Database by the U.S. Department of Labor, Employment and Training Administration (USDOL/ETA), used under the CC BY 4.0 license. We have modified it; USDOL/ETA has not approved, endorsed or tested these modifications. O*NET is a trademark of USDOL/ETA.