Penetration Tester Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
Penetration Tester
Salary Range
Salary Trend
Sep 2025 – Aug 2026
12-Month Trend
Based on advertised IT & Cybersecurity roles.
US market data · Source: Adzuna · Updated Sep 2026
How useful was this template?
Penetration Tester resume samples
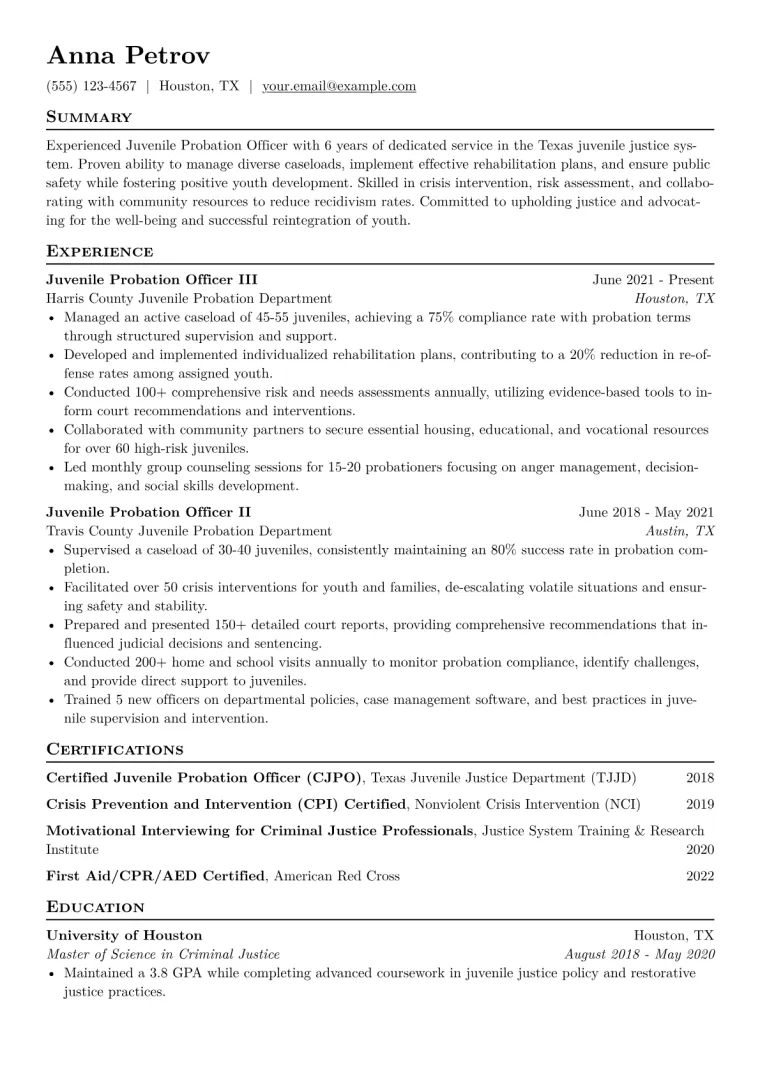
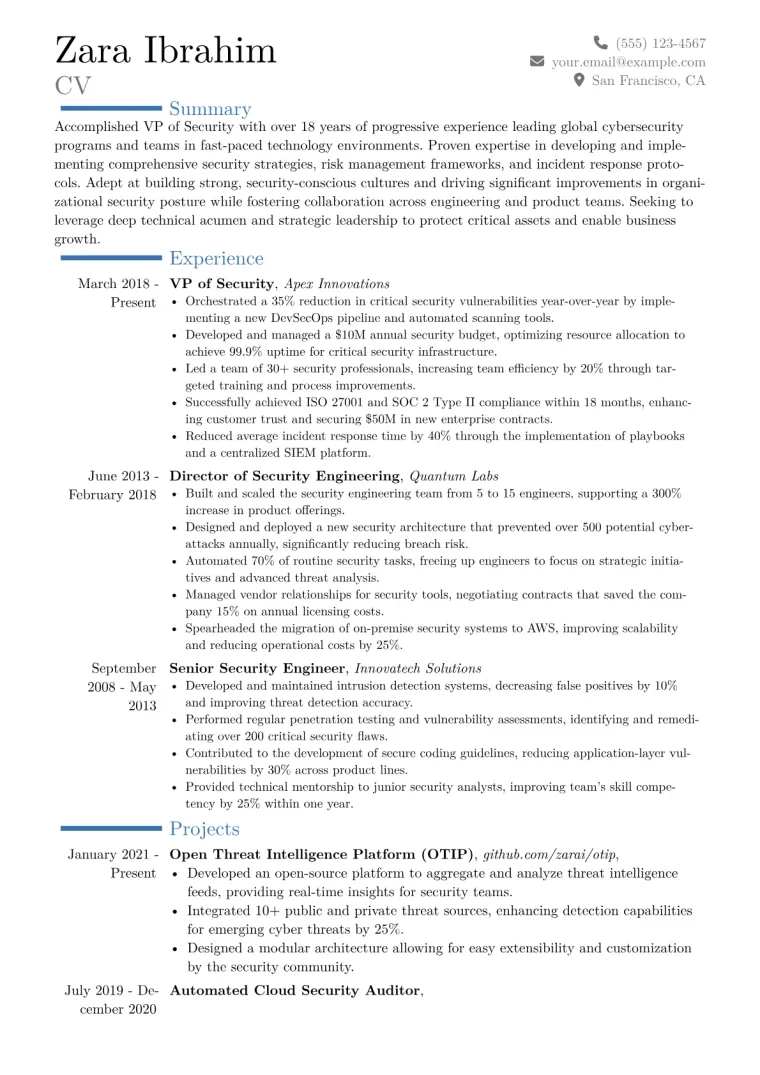
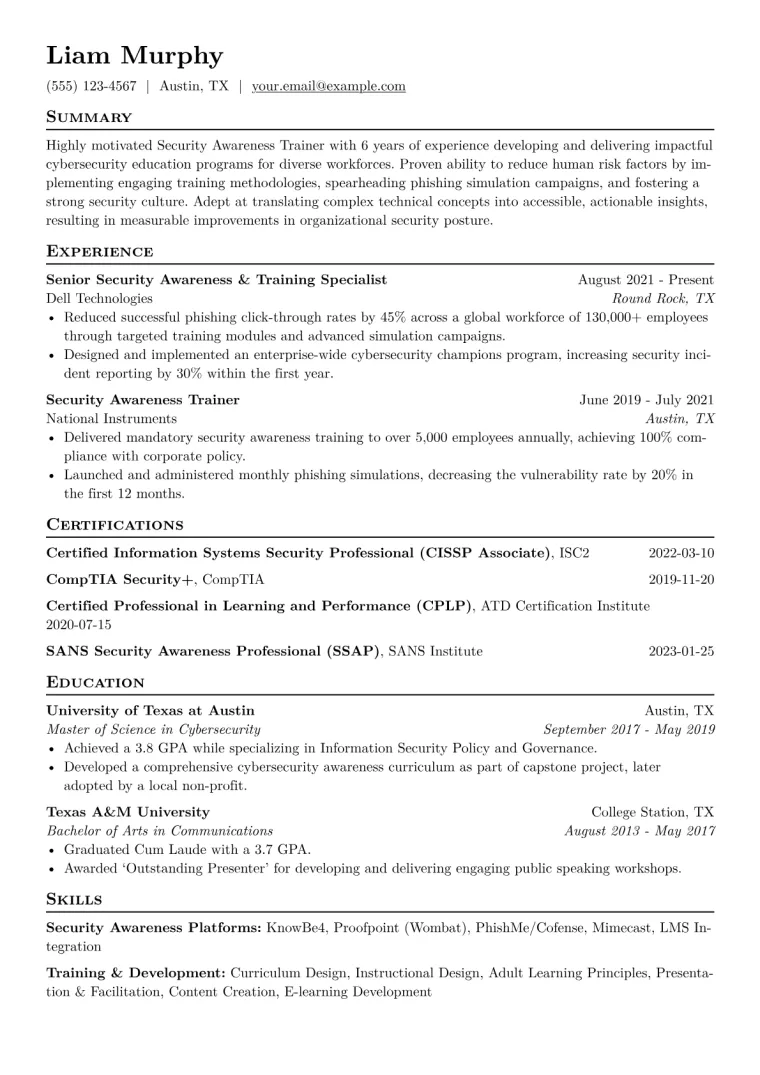
Three complete resumes, each in a different design.


Free to use. No download fee.
Editorial Notes
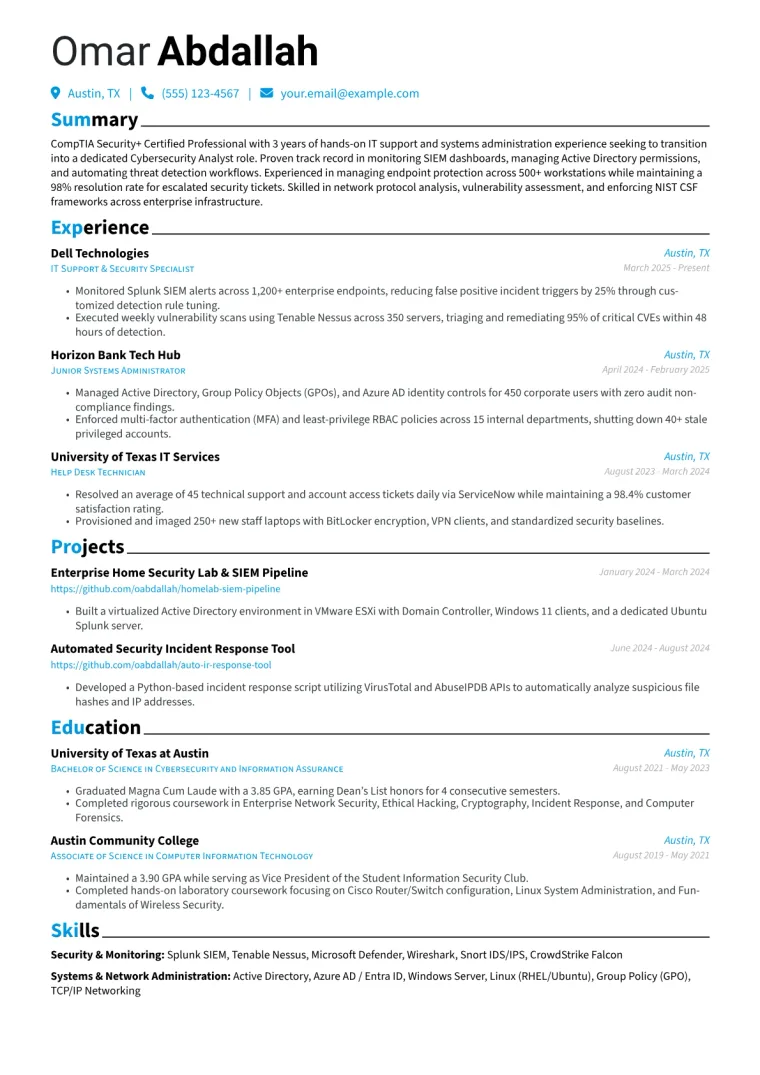
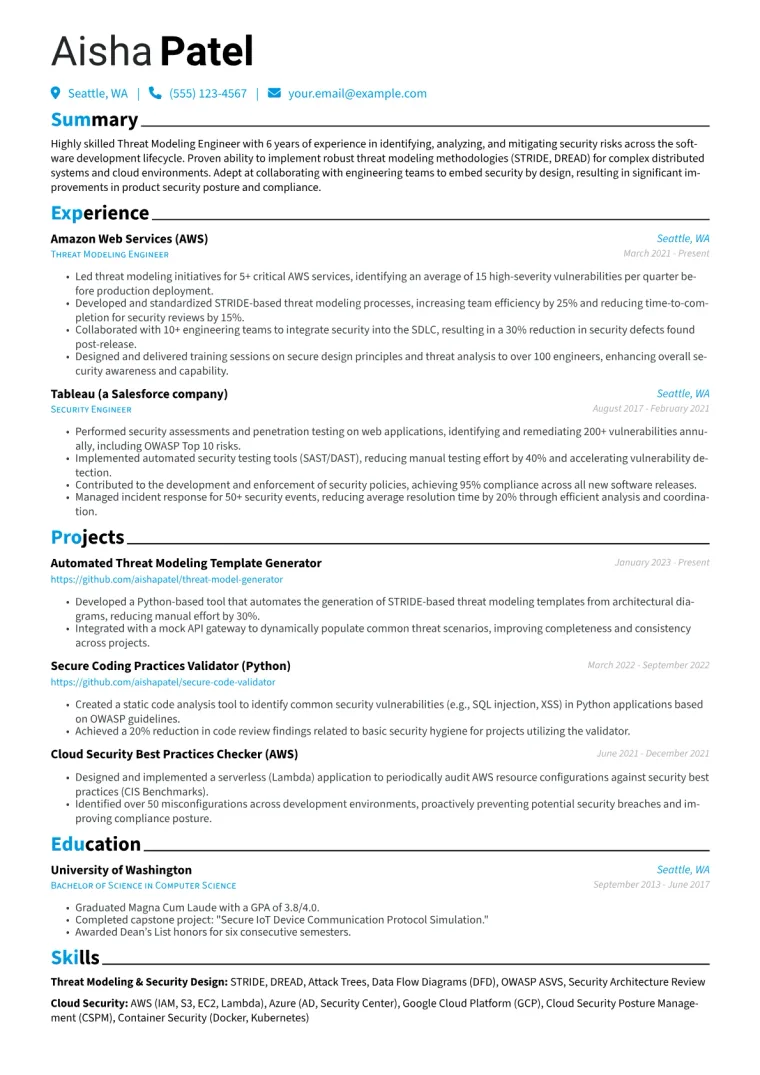
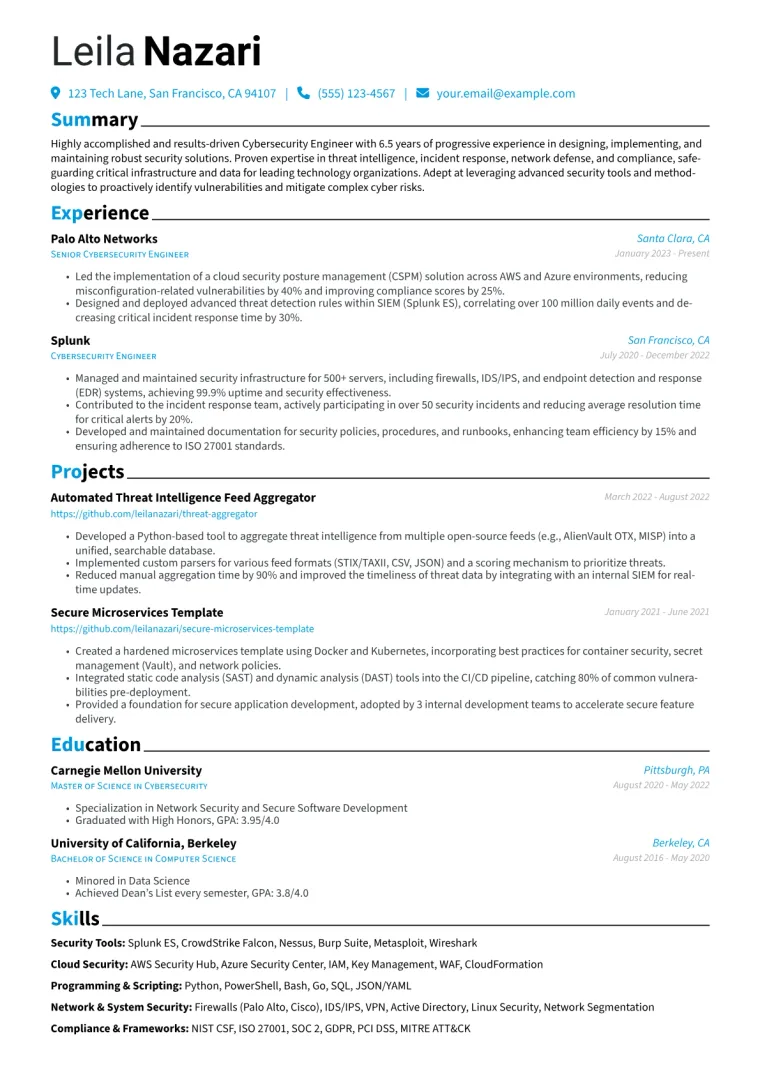
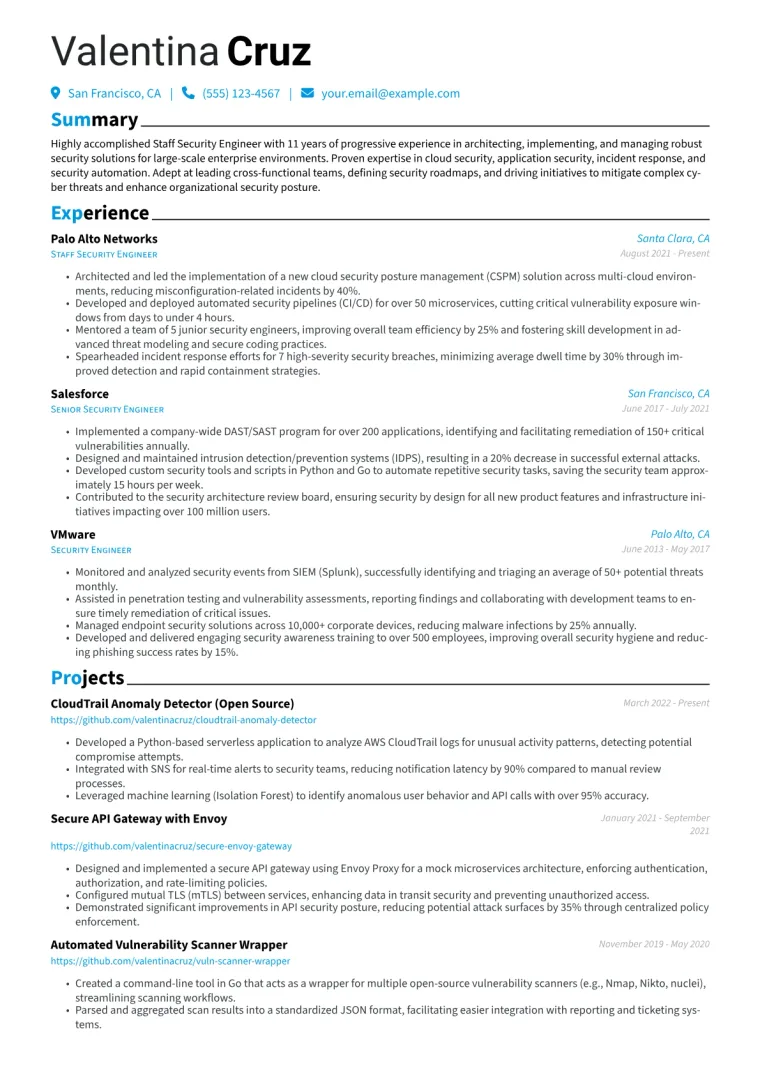
For a penetration tester, a compelling resume highlights practical, hands-on experience and demonstrable impact. Hiring managers seek concrete achievements, such as successful identification and exploitation of critical vulnerabilities, measurable improvements in security posture, or contributions to red team operations. Essential certifications like OSCP, GPEN, or CEH are highly valued, alongside technical skills in web application testing, network exploitation, and scripting with languages like Python. Familiarity with industry-standard tools, from Metasploit to Burp Suite, and a solid grasp of methodologies like OWASP Top 10 are also key indicators of a strong candidate.
This example effectively structures the candidate’s experience, providing a clear sample of how to quantify accomplishments; for instance, detailing specific numbers of vulnerabilities identified or the scope of security assessments conducted. The skills section is logically grouped, making it easy for recruiters to quickly assess proficiency in tools, methodologies, and programming languages. Furthermore, the professional summary effectively encapsulates the candidate’s core expertise and career goals, setting the stage for the detailed experience that follows and demonstrating a clear understanding of the role's demands.
This template was built using JobSprout’s professional CV builder. It can be easily remixed to create your own tailored penetration tester resume, ensuring it aligns perfectly with your unique background and aspirations.
How useful was this template?
Example by JobSprout
Penetration Tester Cover Letter Example
Written for the same person as this resume, ready to adapt.
Penetration Tester resume summary example
Highly skilled Penetration Tester with 6 years of experience in identifying, exploiting, and reporting security vulnerabilities across diverse enterprise environments. Proven expertise in ethical hacking, vulnerability assessment, and security architecture review, leveraging industry-standard tools and methodologies. Adept at collaborating with development and operations teams to implement robust security controls and enhance overall organizational resilience. Committed to staying current with emerging threats and cutting-edge defensive strategies.
Penetration Tester salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $115,455 | $138,750 | $141,037 |
| UK | £43,611 | £60,400 | £72,209 |
| Canada | C$111,429 | C$132,308 | C$147,059 |
| Australia | A$120,000 | A$141,032 | A$143,097 |
| Germany | €78,563 | €87,125 | €95,688 |
| France | €51,563 | €56,875 | €65,833 |
| Netherlands | €55,000 | €66,667 | €74,250 |
| Italy | €25,000 | €31,250 | €38,750 |
| Austria | €46,250 | €58,750 | €67,500 |
| New Zealand | NZ$102,500 | NZ$120,000 | NZ$162,500 |
| India | ₹642,857 | ₹1,303,030 | ₹1,984,848 |
| Poland | zł226,512 | zł273,024 | zł319,536 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
Penetration Tester resume skills and keywords
Recruiters and applicant tracking systems scan Penetration Tester resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
Penetration Tester
Salary Range
Salary Trend
Sep 2025 – Aug 2026
12-Month Trend
Based on advertised IT & Cybersecurity roles.
US market data · Source: Adzuna · Updated Sep 2026
Frequently Asked Questions
What's a good structure for a penetration tester resume sample?
What technical skills and tools should I list on a penetration tester resume?
How do I write a compelling penetration tester resume summary that highlights my experience?
Should a penetration tester resume include a portfolio of findings or certifications?
How can JobSprout help me customize my penetration tester resume for different security firms?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Related Articles

How to Write a CV for Tech Applications [2026 Guide]
Learn how to write a software engineering CV that gets interviews. Real template analysis, what hiring managers look for, and common mistakes to avoid.

How to Write a CV That Shows Startup Experience [2026 Guide]
Learn how to write a CV that showcases founding engineer and startup experience. Real example from JobSprout's creator, what hiring managers look for, and how to position breadth as a strength.