Ethical Hacker Resume Example

TechnologySoftware EngineeringMid Level (3-5 years)SoftwareEngineering

Free to use. No download fee.

Ethical Hacker resume samples

Three complete resumes, each in a different design.

Ethical Hacker resume example, page 1Ethical Hacker resume example, page 2
1 / 2
Ethical Hacker resume example, Ethical Hacker - Red, page 1
Ethical Hacker resume example, Career changer, page 1Ethical Hacker resume example, Career changer, page 2
1 / 2

Free to use. No download fee.

What makes a strong Ethical Hacker resume?

US median salary $140,204 ·

Hiring managers evaluating Ethical Hacker resumes prioritize demonstrated technical proficiency and a clear impact on security posture. They seek candidates who can articulate the scope of penetration tests, the types of vulnerabilities discovered, and the tangible outcomes of their remediation efforts. Key achievements often include quantifying reduced risk, successful exploit development, or significant contributions to bug bounty programs. Certifications like OSCP, CEH, or eJPT, coupled with expertise in tools such as Nmap, Metasploit, Burp Suite, and scripting languages like Python or PowerShell, are essential indicators of practical skill.

Why this example works

The JobSprout example excels by precisely highlighting these critical aspects. It quantifies achievements with percentages, detailing, for instance, a 25% reduction in high-severity findings or the successful exploitation of specific infrastructure weaknesses. Skills are strategically grouped under distinct categories like “Penetration Testing Tools,” “Cloud Security,” and “Scripting & Automation,” providing immediate clarity. Crucially, certifications such as OSCP and CEH are prominently displayed, reinforcing the candidate’s specialized qualifications.

Ethical Hacker resume example: Career Changer

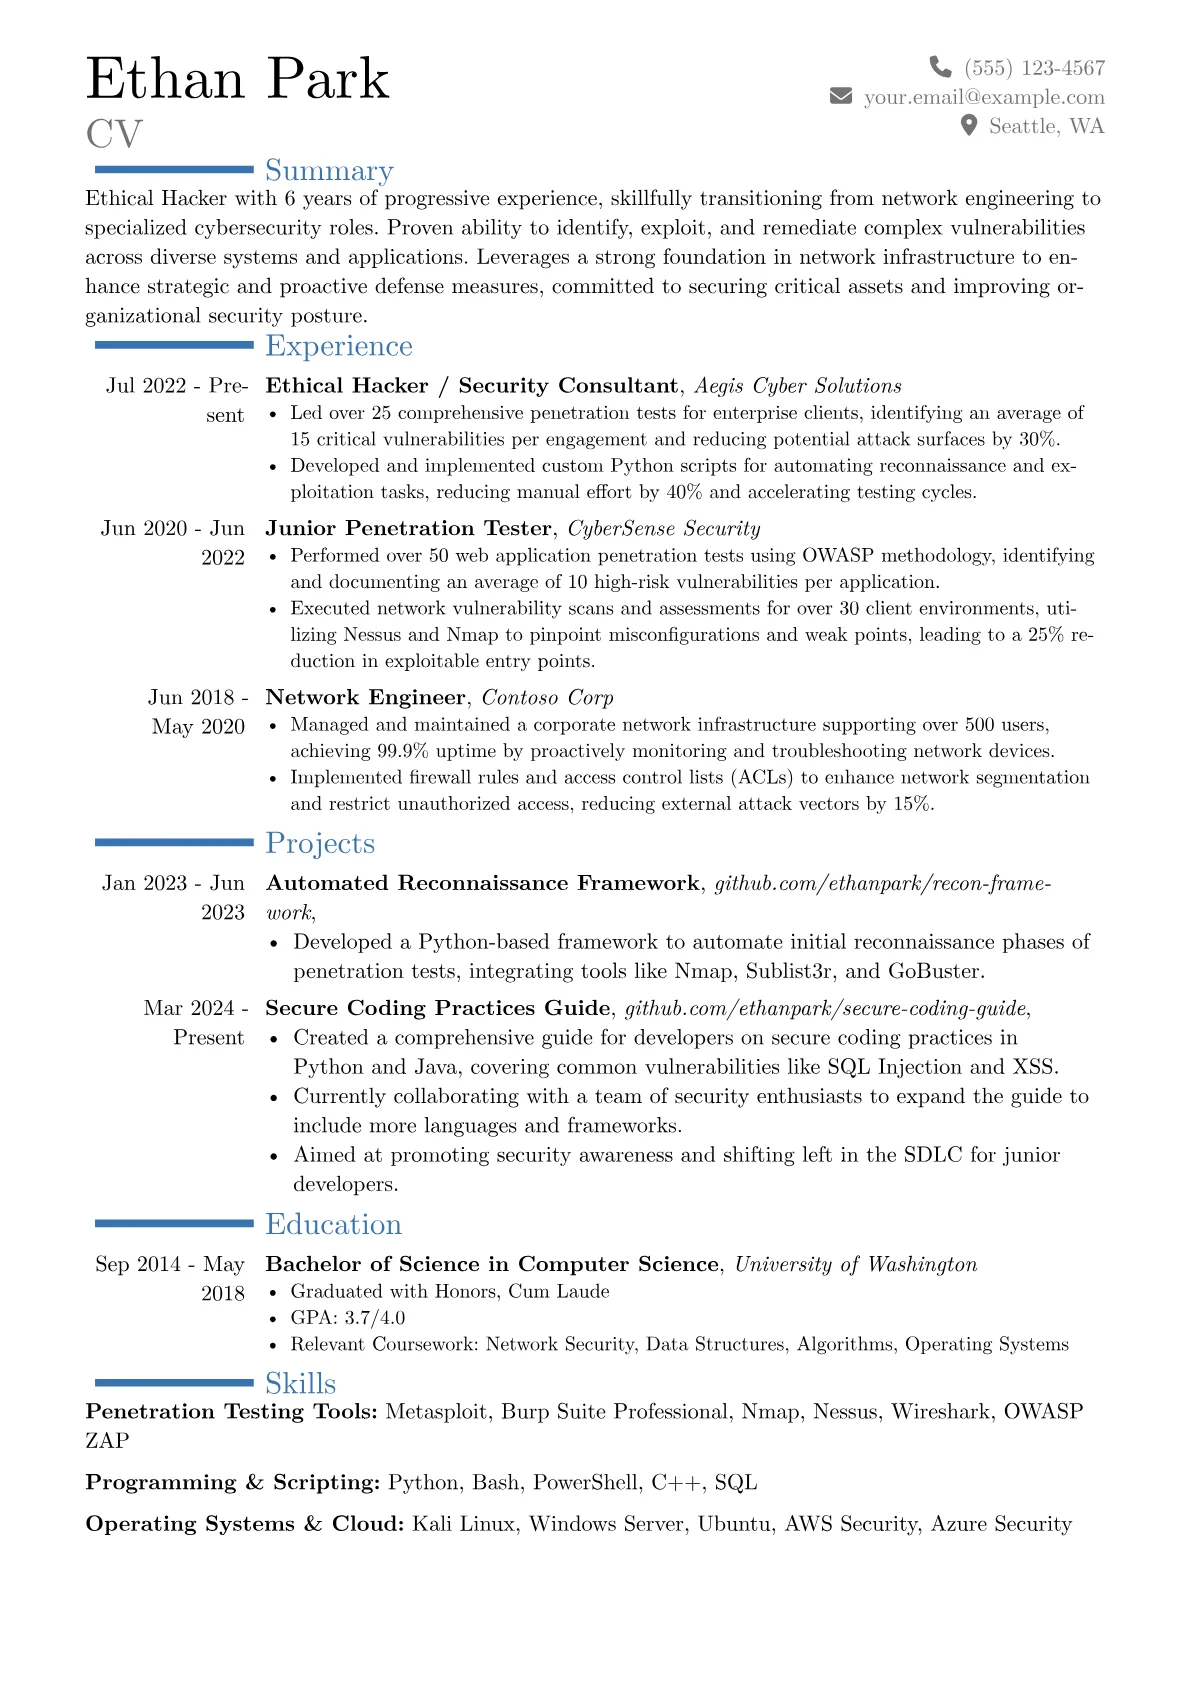
Ethan Park · Ethical Hacker

Summary

Ethical Hacker with 6 years of progressive experience, skillfully transitioning from network engineering to specialized cybersecurity roles. Proven ability to identify, exploit, and remediate complex vulnerabilities across diverse systems and applications. Leverages a strong foundation in network infrastructure to enhance strategic and proactive defense measures, committed to securing critical assets and improving organizational security posture.

Experience

Ethical Hacker / Security Consultant · Aegis Cyber Solutions

Seattle, WA · 2022 - Present

  • Led over 25 comprehensive penetration tests for enterprise clients, identifying an average of 15 critical vulnerabilities per engagement and reducing potential attack surfaces by 30%.
  • Developed and implemented custom Python scripts for automating reconnaissance and exploitation tasks, reducing manual effort by 40% and accelerating testing cycles.
  • Conducted red team exercises simulating advanced persistent threats, uncovering 5 previously unknown blind spots in client security operations and improving incident response times by 20%.
  • Provided expert security advisories and remediation strategies to C-level executives, influencing a 15% increase in client cybersecurity budget allocation.

Junior Penetration Tester · CyberSense Security

Seattle, WA · 2020 - 2022

  • Performed over 50 web application penetration tests using OWASP methodology, identifying and documenting an average of 10 high-risk vulnerabilities per application.
  • Executed network vulnerability scans and assessments for over 30 client environments, utilizing Nessus and Nmap to pinpoint misconfigurations and weak points, leading to a 25% reduction in exploitable entry points.
  • Collaborated with development teams to remediate identified flaws, achieving a 90% fix rate for critical issues within specified timelines.
  • Authored detailed technical reports outlining findings, exploitation steps, and recommended mitigations for both technical and non-technical stakeholders.

Network Engineer · Contoso Corp

Seattle, WA · 2018 - 2020

  • Managed and maintained a corporate network infrastructure supporting over 500 users, achieving 99.9% uptime by proactively monitoring and troubleshooting network devices.
  • Implemented firewall rules and access control lists (ACLs) to enhance network segmentation and restrict unauthorized access, reducing external attack vectors by 15%.
  • Responded to and resolved over 200 network-related security incidents, including malware outbreaks and unauthorized access attempts, within established SLAs.
  • Configured and optimized network devices (routers, switches, firewalls) from Cisco and Juniper, improving network performance by 10% through efficient traffic management.

Education

Bachelor of Science in Computer Science · University of Washington

Seattle, WA · 2014 - 2018

  • Graduated with Honors, Cum Laude
  • GPA: 3.7/4.0
  • Relevant Coursework: Network Security, Data Structures, Algorithms, Operating Systems

Skills

Penetration Testing Tools:MetasploitBurp Suite ProfessionalNmapNessusWiresharkOWASP ZAP
Programming & Scripting:PythonBashPowerShellC++SQL
Operating Systems & Cloud:Kali LinuxWindows ServerUbuntuAWS SecurityAzure Security
Security Concepts & Methodologies:Vulnerability AssessmentRisk ManagementRed TeamingIncident ResponseSocial EngineeringWeb Application Security

How useful was this template?

4.9 (17 votes)
JobSprout logoExample by JobSprout

See this resume as a website

The same content, live on your own jobsprout.me page. Share a link instead of a PDF.

View live example
Ethical Hacker cover letter for a career changer
Matching cover letter

Ethical Hacker cover letter for a career changer

Written for the same situation as this resume.

See the cover letter

Ethical Hacker resume summary example

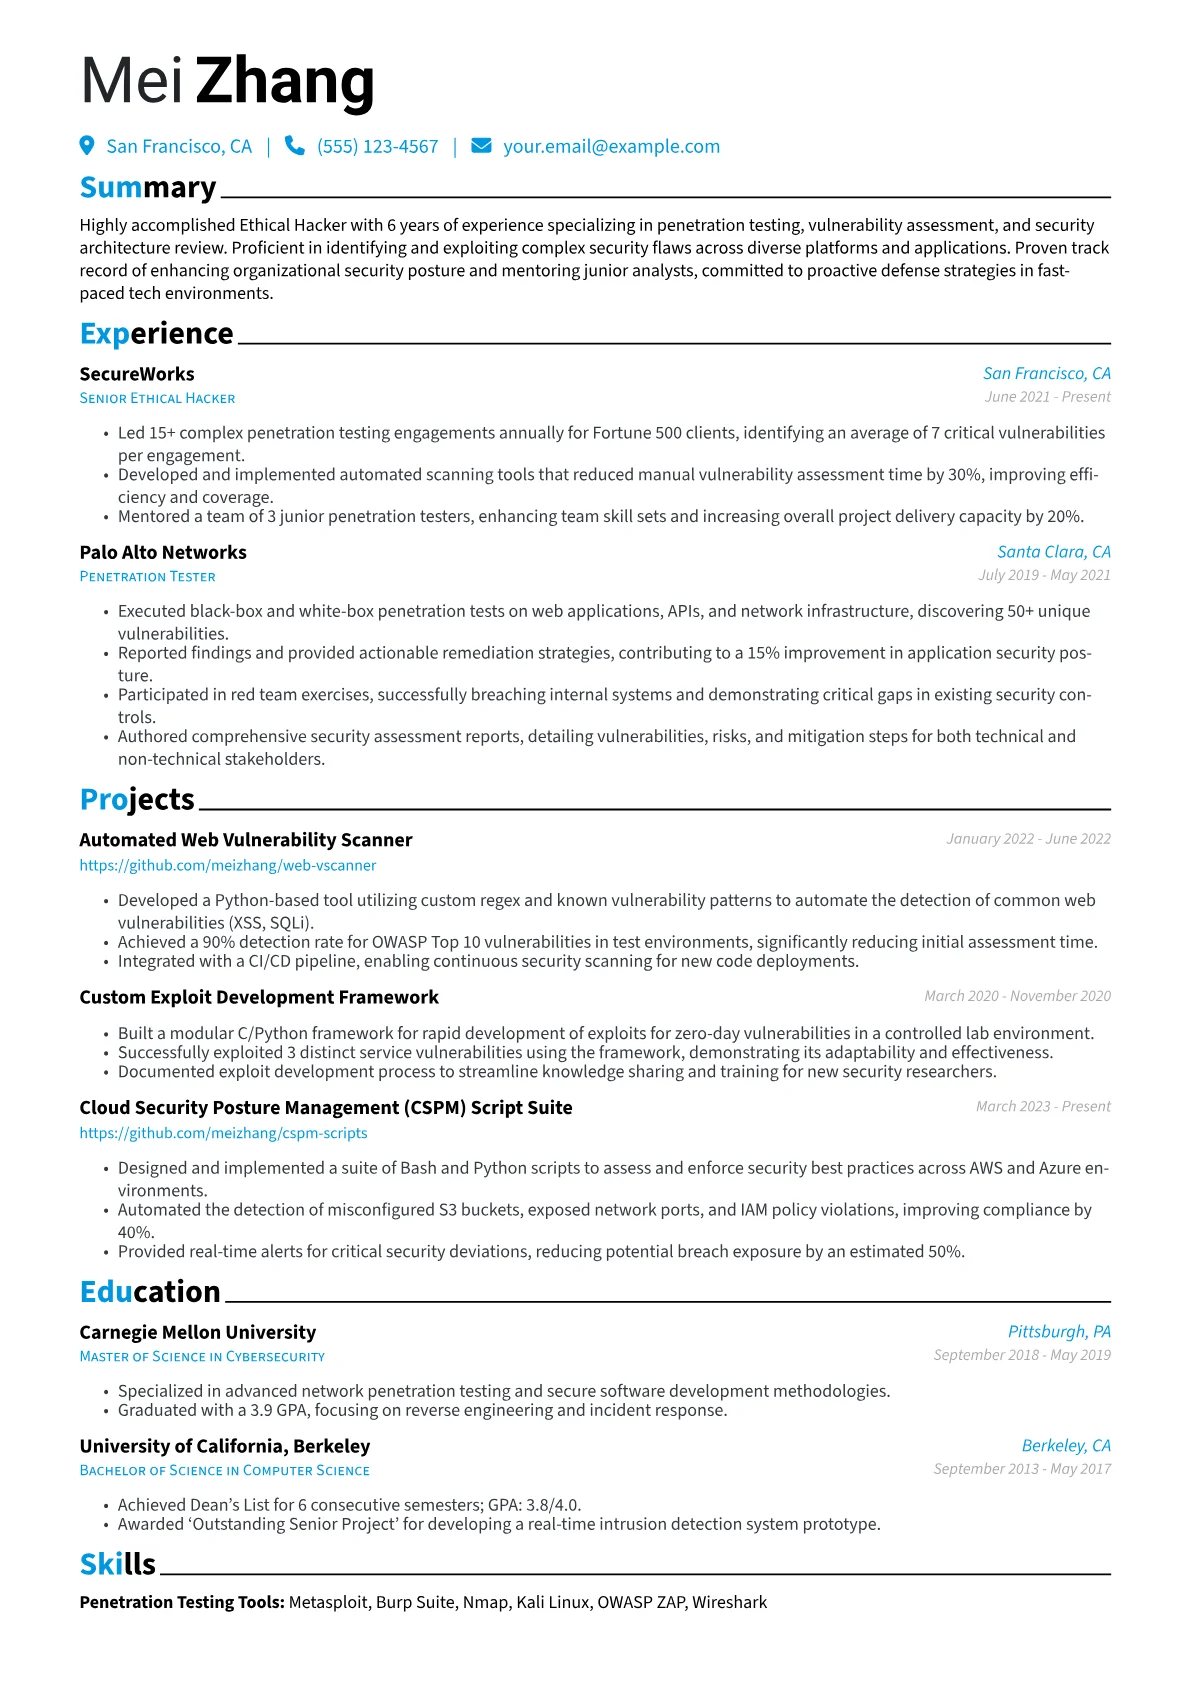
Highly accomplished Ethical Hacker with 6 years of experience specializing in penetration testing, vulnerability assessment, and security architecture review. Proficient in identifying and exploiting complex security flaws across diverse platforms and applications. Proven track record of enhancing organizational security posture and mentoring junior analysts, committed to proactive defense strategies in fast-paced tech environments.

Ethical Hacker salary by country

Country25th percentileMedian75th percentile
US$113,214$140,204$150,102
UK£35,357£40,714£46,071
CanadaC$86,152C$113,871C$140,800
AustraliaA$101,935A$126,667A$147,857
Germany€59,500€70,570€77,887
France€37,875€44,167€49,750
Netherlands€55,000€66,667€74,250
Italy€25,000€31,250€38,750
Austria€46,250€58,750€67,500
New ZealandNZ$102,500NZ$120,000NZ$162,500
India₹1,142,857₹1,571,429₹2,000,000
Polandzł186,440zł209,338zł232,236

Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.

Ethical Hacker resume skills and keywords

Recruiters and applicant tracking systems scan Ethical Hacker resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.

Hard skills

Penetration TestingVulnerability AssessmentWeb Application SecurityNetwork SecurityCloud SecuritySecurity Architecture ReviewIncident ResponseCryptographyExploit DevelopmentThreat ModelingSecure Code ReviewRisk Management

Tools & software

Kali LinuxMetasploitBurp SuiteNmapWiresharkNessusOWASP ZAP

Certifications

CEHOSCPCISSPCompTIA Security+

Soft skills

Problem SolvingAttention to DetailCritical ThinkingCommunication SkillsEthical Judgment

Market Insights

Ethical Hacker

Salary Range

$140,204median annual
$20k$150k

Salary Trend

Mar 2025 – Feb 2026

12-Month Trend

Stable
+2.4% YoY

Based on advertised Software Engineering roles.

US market data · Source: Adzuna · Updated Mar 2026

Frequently Asked Questions

What's the best resume structure for a mid-level Ethical Hacker?
For a mid-level Ethical Hacker with 3-7 years of experience, a one-page resume is generally most appropriate. Lead with a strong professional summary highlighting your cybersecurity expertise, ethical hacking skills, and commitment to proactive security. Follow with your technical experience, emphasizing specific penetration testing projects and security assessments. Ensure you include dedicated sections for education, certifications, and a detailed list of your technical skills.
Which key skills and qualifications should an Ethical Hacker highlight?
You should emphasize skills such as penetration testing, vulnerability assessment, web application security, network security, and incident response. Highlight proficiency with industry-standard tools like Metasploit, Nmap, Burp Suite, Wireshark, and various scripting languages (e.g., Python, Bash). Showcase your understanding of security frameworks, compliance standards (e.g., ISO 27001, NIST), and your ability to exploit and remediate security flaws effectively.
How can I write strong achievement bullets and a compelling professional summary for this role?
Your professional summary should immediately convey your proven ability to identify and mitigate security vulnerabilities proactively, showcasing your expertise in ethical hacking methodologies. Achievement bullets should be technical and results-oriented. For example, "Conducted comprehensive penetration tests on critical web applications, identifying 15+ high-severity vulnerabilities and improving overall security posture by 30% through detailed remediation recommendations." Detail the specific impact of your findings and solutions.
What optional resume sections matter most for an Ethical Hacker?
A "Certifications" section for CEH (Certified Ethical Hacker), OSCP (Offensive Security Certified Professional), CompTIA Security+, or CISSP is highly valuable and often a requirement. A "Technical Skills" section listing operating systems, programming languages, security tools, and cloud platforms is essential. A "Projects" section showcasing personal security research, participation in Capture The Flag (CTF) competitions, or contributions to open-source security tools would be a significant advantage.
How do I tailor my Ethical Hacker resume for a specific job posting?
Review the job description for specific technologies, systems, or types of penetration tests mentioned, such as cloud security, IoT, or SCADA systems. Highlight your direct experience with these areas and relevant security tools, customizing your language to match the job's requirements. JobSprout's "Remix with AI" feature can help you by taking the job description and adapting your resume content to best match the specific technical challenges and security demands of the role.

The blank page is the hard part. Skip it.

Free to use. No download fee.