SOC Analyst Resume Example
 Example by JobSprout
Free to use. No download fee.
Market Insights
SOC Analyst
Salary Range
Salary Trend
12-Month Trend
Based on advertised IT & Cybersecurity roles.
US market data · Source: Adzuna · Updated Sep 2026
How useful was this template?
SOC Analyst resume samples
Three complete resumes, each in a different design.
Free to use. No download fee.
What makes a strong SOC Analyst resume?
US median salary $134,074 ·
A strong Soc Analyst resume highlights direct contributions to an organization's security posture. Hiring managers look for concrete achievements in areas like incident response, threat detection, and vulnerability management. Crucial certifications such as CompTIA Security+ or GIAC GSEC are often expected, alongside proficiency with SIEM platforms (e.g., Splunk, QRadar), EDR solutions, and scripting for automation. Familiarity with frameworks like MITRE ATT&CK or NIST also signals a candidate's comprehensive understanding of security operations.
Why this example works
This sample effectively demonstrates how to articulate these essential qualifications. It excels by quantifying achievements, such as reducing false positives by a specific percentage or managing a certain volume of security incidents monthly, providing clear evidence of impact. Skills are logically grouped, distinguishing between tools, methodologies, and programming languages, which aids readability for recruiters. The summary concisely highlights relevant experience and key expertise, making it an excellent guide for anyone crafting their own resume for this role.
SOC Analyst resume example (text version)
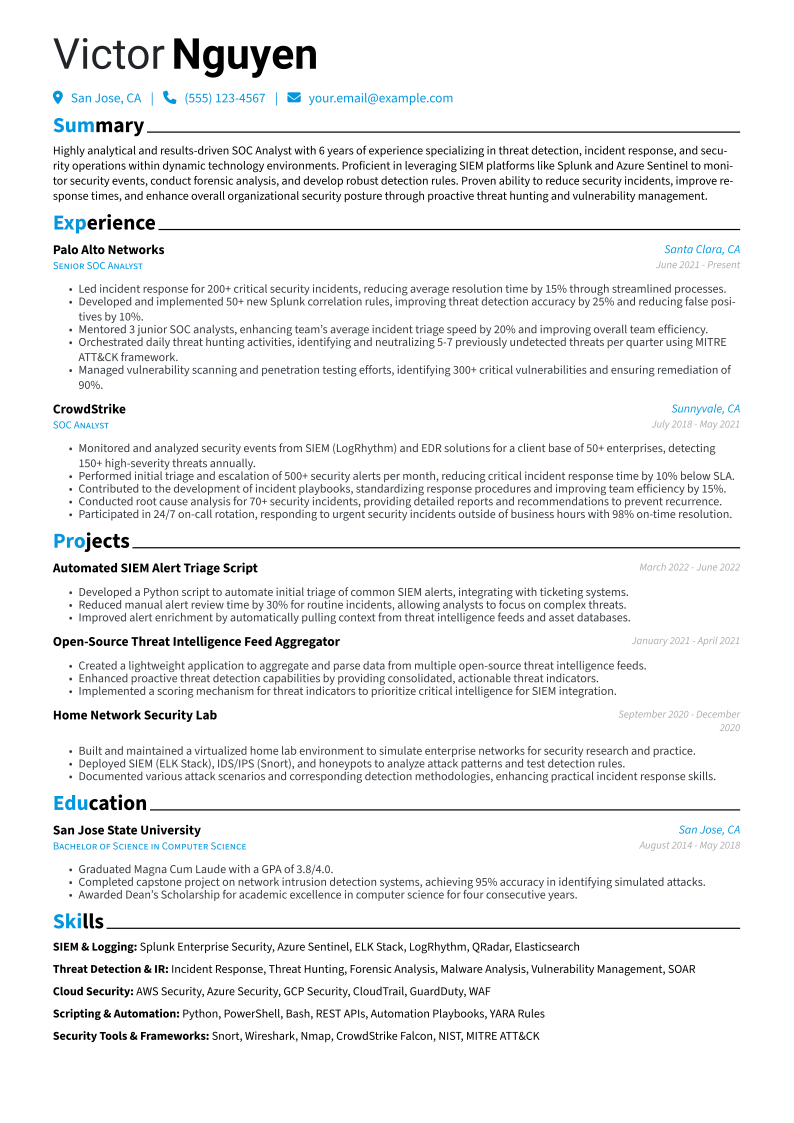
Victor Nguyen · SOC Analyst
Summary
Highly analytical and results-driven SOC Analyst with 6 years of experience specializing in threat detection, incident response, and security operations within dynamic technology environments. Proficient in leveraging SIEM platforms like Splunk and Azure Sentinel to monitor security events, conduct forensic analysis, and develop robust detection rules. Proven ability to reduce security incidents, improve response times, and enhance overall organizational security posture through proactive threat hunting and vulnerability management.
Experience
Senior SOC Analyst · Palo Alto Networks
Santa Clara, CA · 2021 - Present
- Led incident response for 200+ critical security incidents, reducing average resolution time by 15% through streamlined processes.
- Developed and implemented 50+ new Splunk correlation rules, improving threat detection accuracy by 25% and reducing false positives by 10%.
- Mentored 3 junior SOC analysts, enhancing team's average incident triage speed by 20% and improving overall team efficiency.
- Orchestrated daily threat hunting activities, identifying and neutralizing 5-7 previously undetected threats per quarter using MITRE ATT&CK framework.
- Managed vulnerability scanning and penetration testing efforts, identifying 300+ critical vulnerabilities and ensuring remediation of 90%.
SOC Analyst · CrowdStrike
Sunnyvale, CA · 2018 - 2021
- Monitored and analyzed security events from SIEM (LogRhythm) and EDR solutions for a client base of 50+ enterprises, detecting 150+ high-severity threats annually.
- Performed initial triage and escalation of 500+ security alerts per month, reducing critical incident response time by 10% below SLA.
- Contributed to the development of incident playbooks, standardizing response procedures and improving team efficiency by 15%.
- Conducted root cause analysis for 70+ security incidents, providing detailed reports and recommendations to prevent recurrence.
- Participated in 24/7 on-call rotation, responding to urgent security incidents outside of business hours with 98% on-time resolution.
Education
Bachelor of Science in Computer Science · San Jose State University
San Jose, CA · 2014 - 2018
- Graduated Magna Cum Laude with a GPA of 3.8/4.0.
- Completed capstone project on network intrusion detection systems, achieving 95% accuracy in identifying simulated attacks.
- Awarded Dean's Scholarship for academic excellence in computer science for four consecutive years.
Skills
SOC Analyst resume example: Different Focus
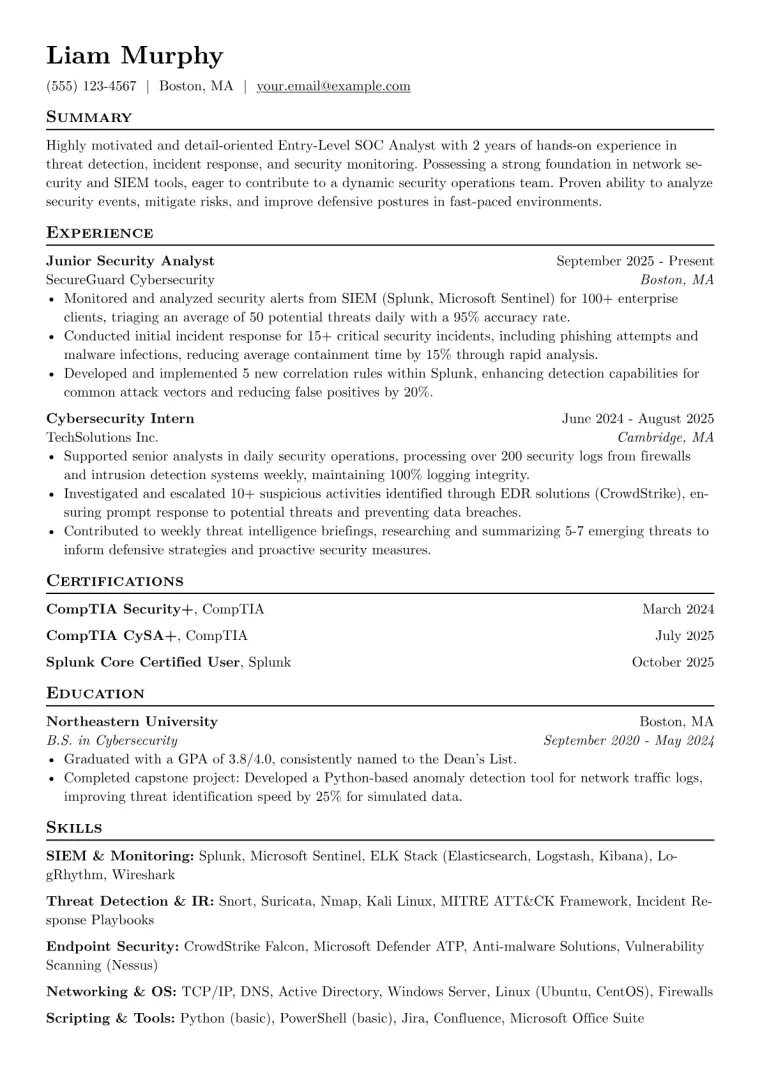
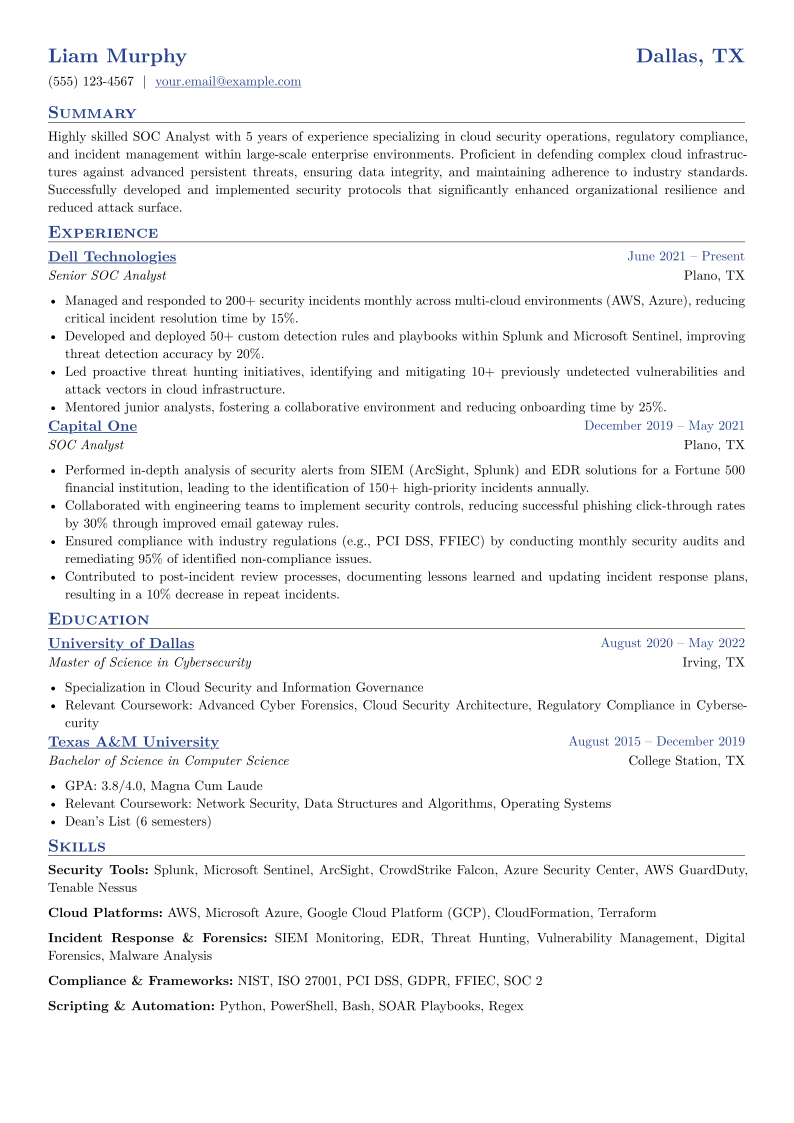
Liam Murphy · SOC Analyst
Summary
Highly skilled SOC Analyst with 5 years of experience specializing in cloud security operations, regulatory compliance, and incident management within large-scale enterprise environments. Proficient in defending complex cloud infrastructures against advanced persistent threats, ensuring data integrity, and maintaining adherence to industry standards. Successfully developed and implemented security protocols that significantly enhanced organizational resilience and reduced attack surface.
Experience
Senior SOC Analyst · Dell Technologies
Plano, TX · 2021 - Present
- Managed and responded to 200+ security incidents monthly across multi-cloud environments (AWS, Azure), reducing critical incident resolution time by 15%.
- Developed and deployed 50+ custom detection rules and playbooks within Splunk and Microsoft Sentinel, improving threat detection accuracy by 20%.
- Led proactive threat hunting initiatives, identifying and mitigating 10+ previously undetected vulnerabilities and attack vectors in cloud infrastructure.
- Mentored junior analysts, fostering a collaborative environment and reducing onboarding time by 25%.
SOC Analyst · Capital One
Plano, TX · 2019 - 2021
- Performed in-depth analysis of security alerts from SIEM (ArcSight, Splunk) and EDR solutions for a Fortune 500 financial institution, leading to the identification of 150+ high-priority incidents annually.
- Collaborated with engineering teams to implement security controls, reducing successful phishing click-through rates by 30% through improved email gateway rules.
- Ensured compliance with industry regulations (e.g., PCI DSS, FFIEC) by conducting monthly security audits and remediating 95% of identified non-compliance issues.
- Contributed to post-incident review processes, documenting lessons learned and updating incident response plans, resulting in a 10% decrease in repeat incidents.
Education
Master of Science in Cybersecurity · University of Dallas
Irving, TX · 2020 - 2022
- Specialization in Cloud Security and Information Governance
- Relevant Coursework: Advanced Cyber Forensics, Cloud Security Architecture, Regulatory Compliance in Cybersecurity
Bachelor of Science in Computer Science · Texas A&M University
College Station, TX · 2015 - 2019
- GPA: 3.8/4.0, Magna Cum Laude
- Relevant Coursework: Network Security, Data Structures and Algorithms, Operating Systems
- Dean's List (6 semesters)
Skills
SOC Analyst resume example: Career Changer
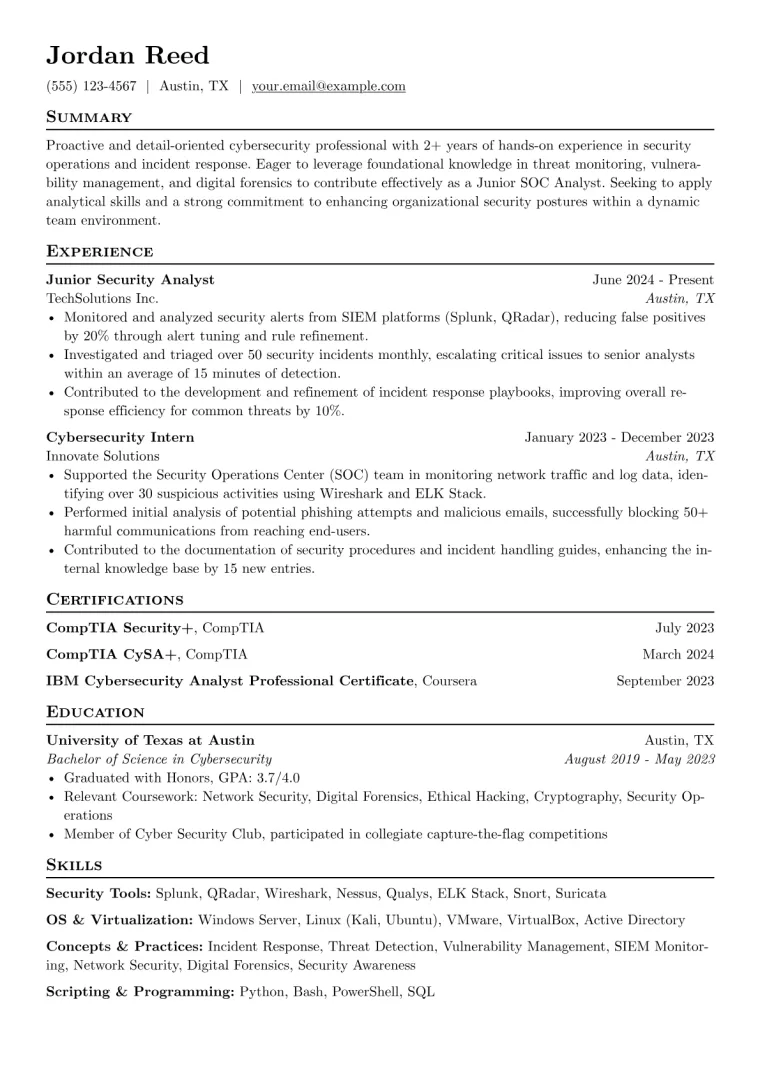
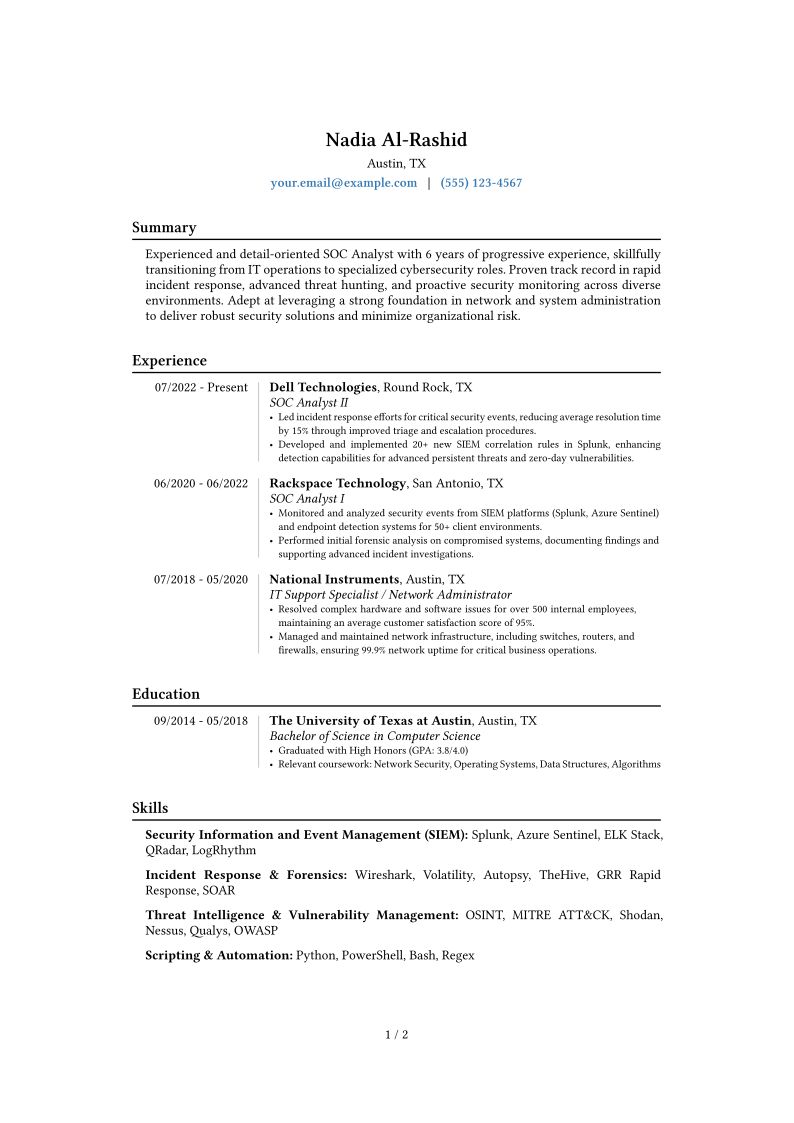
Nadia Al-Rashid · SOC Analyst
Summary
Experienced and detail-oriented SOC Analyst with 6 years of progressive experience, skillfully transitioning from IT operations to specialized cybersecurity roles. Proven track record in rapid incident response, advanced threat hunting, and proactive security monitoring across diverse environments. Adept at leveraging a strong foundation in network and system administration to deliver robust security solutions and minimize organizational risk.
Experience
SOC Analyst II · Dell Technologies
Round Rock, TX · 2022 - Present
- Led incident response efforts for critical security events, reducing average resolution time by 15% through improved triage and escalation procedures.
- Developed and implemented 20+ new SIEM correlation rules in Splunk, enhancing detection capabilities for advanced persistent threats and zero-day vulnerabilities.
- Conducted proactive threat hunting campaigns using MITRE ATT&CK framework, identifying and neutralizing 3 high-severity internal threats before exploitation.
- Mentored junior SOC analysts on security tool best practices and incident handling, improving team efficiency and knowledge sharing.
- Automated repetitive analysis tasks using Python scripting, decreasing manual effort by 25% for routine alert investigations.
SOC Analyst I · Rackspace Technology
San Antonio, TX · 2020 - 2022
- Monitored and analyzed security events from SIEM platforms (Splunk, Azure Sentinel) and endpoint detection systems for 50+ client environments.
- Performed initial forensic analysis on compromised systems, documenting findings and supporting advanced incident investigations.
- Contributed to the development of incident response playbooks, improving clarity and efficiency of response actions by 10%.
- Successfully identified and mitigated over 100 phishing attacks and malware infections, protecting sensitive client data.
IT Support Specialist / Network Administrator · National Instruments
Austin, TX · 2018 - 2020
- Resolved complex hardware and software issues for over 500 internal employees, maintaining an average customer satisfaction score of 95%.
- Managed and maintained network infrastructure, including switches, routers, and firewalls, ensuring 99.9% network uptime for critical business operations.
- Implemented security patches and updates across 200+ workstations and servers, reducing vulnerability exposure by 30%.
- Provided first-line support for security-related inquiries, escalating complex issues to the cybersecurity team.
Education
Bachelor of Science in Computer Science · The University of Texas at Austin
Austin, TX · 2014 - 2018
- Graduated with High Honors (GPA: 3.8/4.0)
- Relevant coursework: Network Security, Operating Systems, Data Structures, Algorithms
Skills
How useful was this template?
Example by JobSprout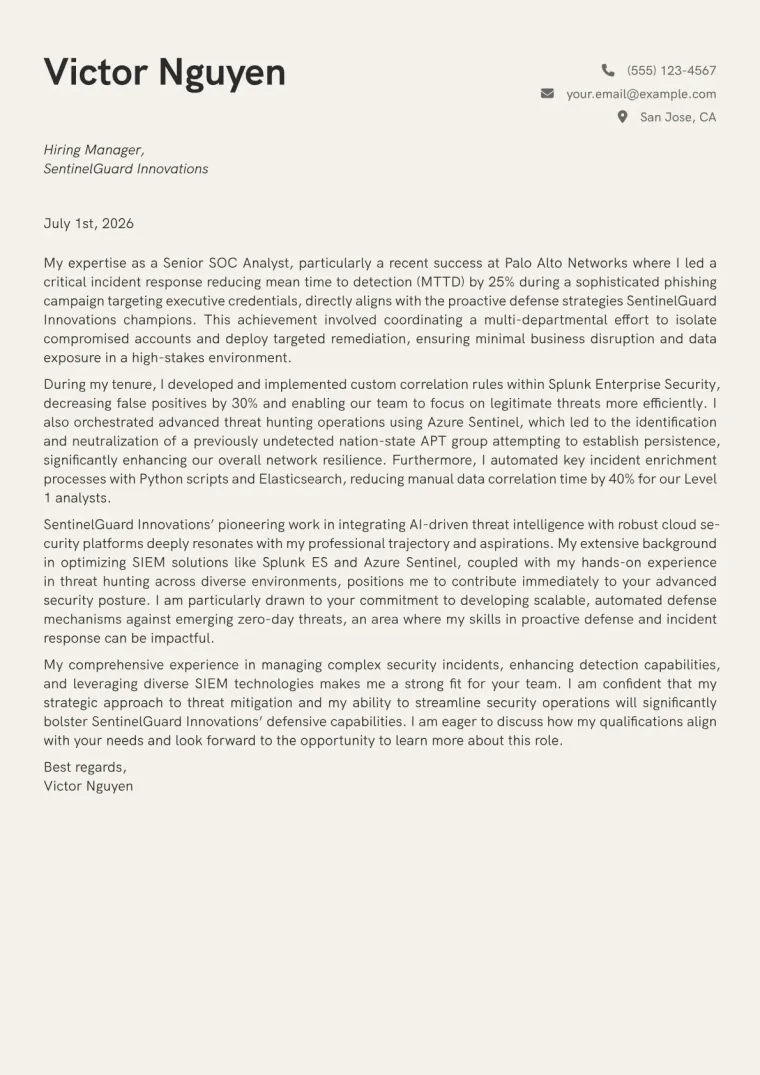
SOC Analyst Cover Letter Example
Written for the same person as this resume, ready to adapt.
SOC Analyst resume summary example
Highly analytical and results-driven SOC Analyst with 6 years of experience specializing in threat detection, incident response, and security operations within dynamic technology environments. Proficient in leveraging SIEM platforms like Splunk and Azure Sentinel to monitor security events, conduct forensic analysis, and develop robust detection rules. Proven ability to reduce security incidents, improve response times, and enhance overall organizational security posture through proactive threat hunting and vulnerability management.
SOC Analyst salary by country
| Country | 25th percentile | Median | 75th percentile |
|---|---|---|---|
| US | $108,571 | $134,074 | $143,152 |
| UK | £34,142 | £38,433 | £55,577 |
| Canada | C$105,000 | C$130,000 | C$172,305 |
| Australia | A$101,935 | A$126,667 | A$147,857 |
| Germany | €75,000 | €80,000 | €85,000 |
| France | €42,774 | €48,014 | €55,864 |
| Netherlands | €55,000 | €66,667 | €74,250 |
| Italy | €25,000 | €31,250 | €38,750 |
| Austria | €46,250 | €58,750 | €67,500 |
| New Zealand | NZ$102,500 | NZ$120,000 | NZ$162,500 |
| India | ₹416,667 | ₹833,333 | ₹2,000,000 |
| Poland | zł186,440 | zł209,338 | zł232,236 |
Annual salaries in local currency, aggregated from live job postings via Adzuna. Figures refresh continuously and reflect advertised pay, not negotiated offers.
SOC Analyst resume skills and keywords
Recruiters and applicant tracking systems scan SOC Analyst resumes for these skills and keywords. Include the ones that match your experience and mirror the wording in the job description. Check your resume against them with the free ATS checker.
Hard skills
Tools & software
Certifications
Soft skills
Market Insights
SOC Analyst
Salary Range
Salary Trend
12-Month Trend
Based on advertised IT & Cybersecurity roles.
US market data · Source: Adzuna · Updated Sep 2026
Frequently Asked Questions
What should a strong mid-level SOC analyst resume sample or example include?
Which key SOC analyst resume skills should I emphasize as a mid-level professional?
How can I write a compelling summary and achievement bullets for my SOC analyst resume?
What certifications or projects are essential for a SOC analyst resume?
How can JobSprout's Remix with AI help me tailor my SOC analyst resume for specific security operations roles?
The blank page is the hard part. Skip it.
Free to use. No download fee.
Related Articles
Cybersecurity Analyst Resume: Examples & Skills to Include (2026)
Write a cybersecurity resume that lands interviews. Resume examples, technical skills tables, certification guidance, and bullet point formulas for SOC analysts, pen testers, security engineers, and GRC roles.

How to Write a CV for Tech Applications [2026 Guide]
Learn how to write a software engineering CV that gets interviews. Real template analysis, what hiring managers look for, and common mistakes to avoid.

How to Write a CV That Shows Startup Experience [2026 Guide]
Learn how to write a CV that showcases founding engineer and startup experience. Real example from JobSprout's creator, what hiring managers look for, and how to position breadth as a strength.
Career moves from SOC Analyst
Usually need less experience or training
Includes information from the O*NET 30.3 Database by the U.S. Department of Labor, Employment and Training Administration (USDOL/ETA), used under the CC BY 4.0 license. We have modified it; USDOL/ETA has not approved, endorsed or tested these modifications. O*NET is a trademark of USDOL/ETA.